PhishER is presented as a lightweight Security Orchestration, Automation and Response (SOAR) platform to orchestrate threat response and manage the high volume of potentially malicious email messages reported by users. And, with automatic prioritization of emails, PhishER helps InfoSec and Security Operations team cut through the inbox noise and respond to the most dangerous threats more quickly.
$0.75
per month (billed annually) per seat
Microsoft Defender for Endpoint
Score8.8 out of 10
N/A
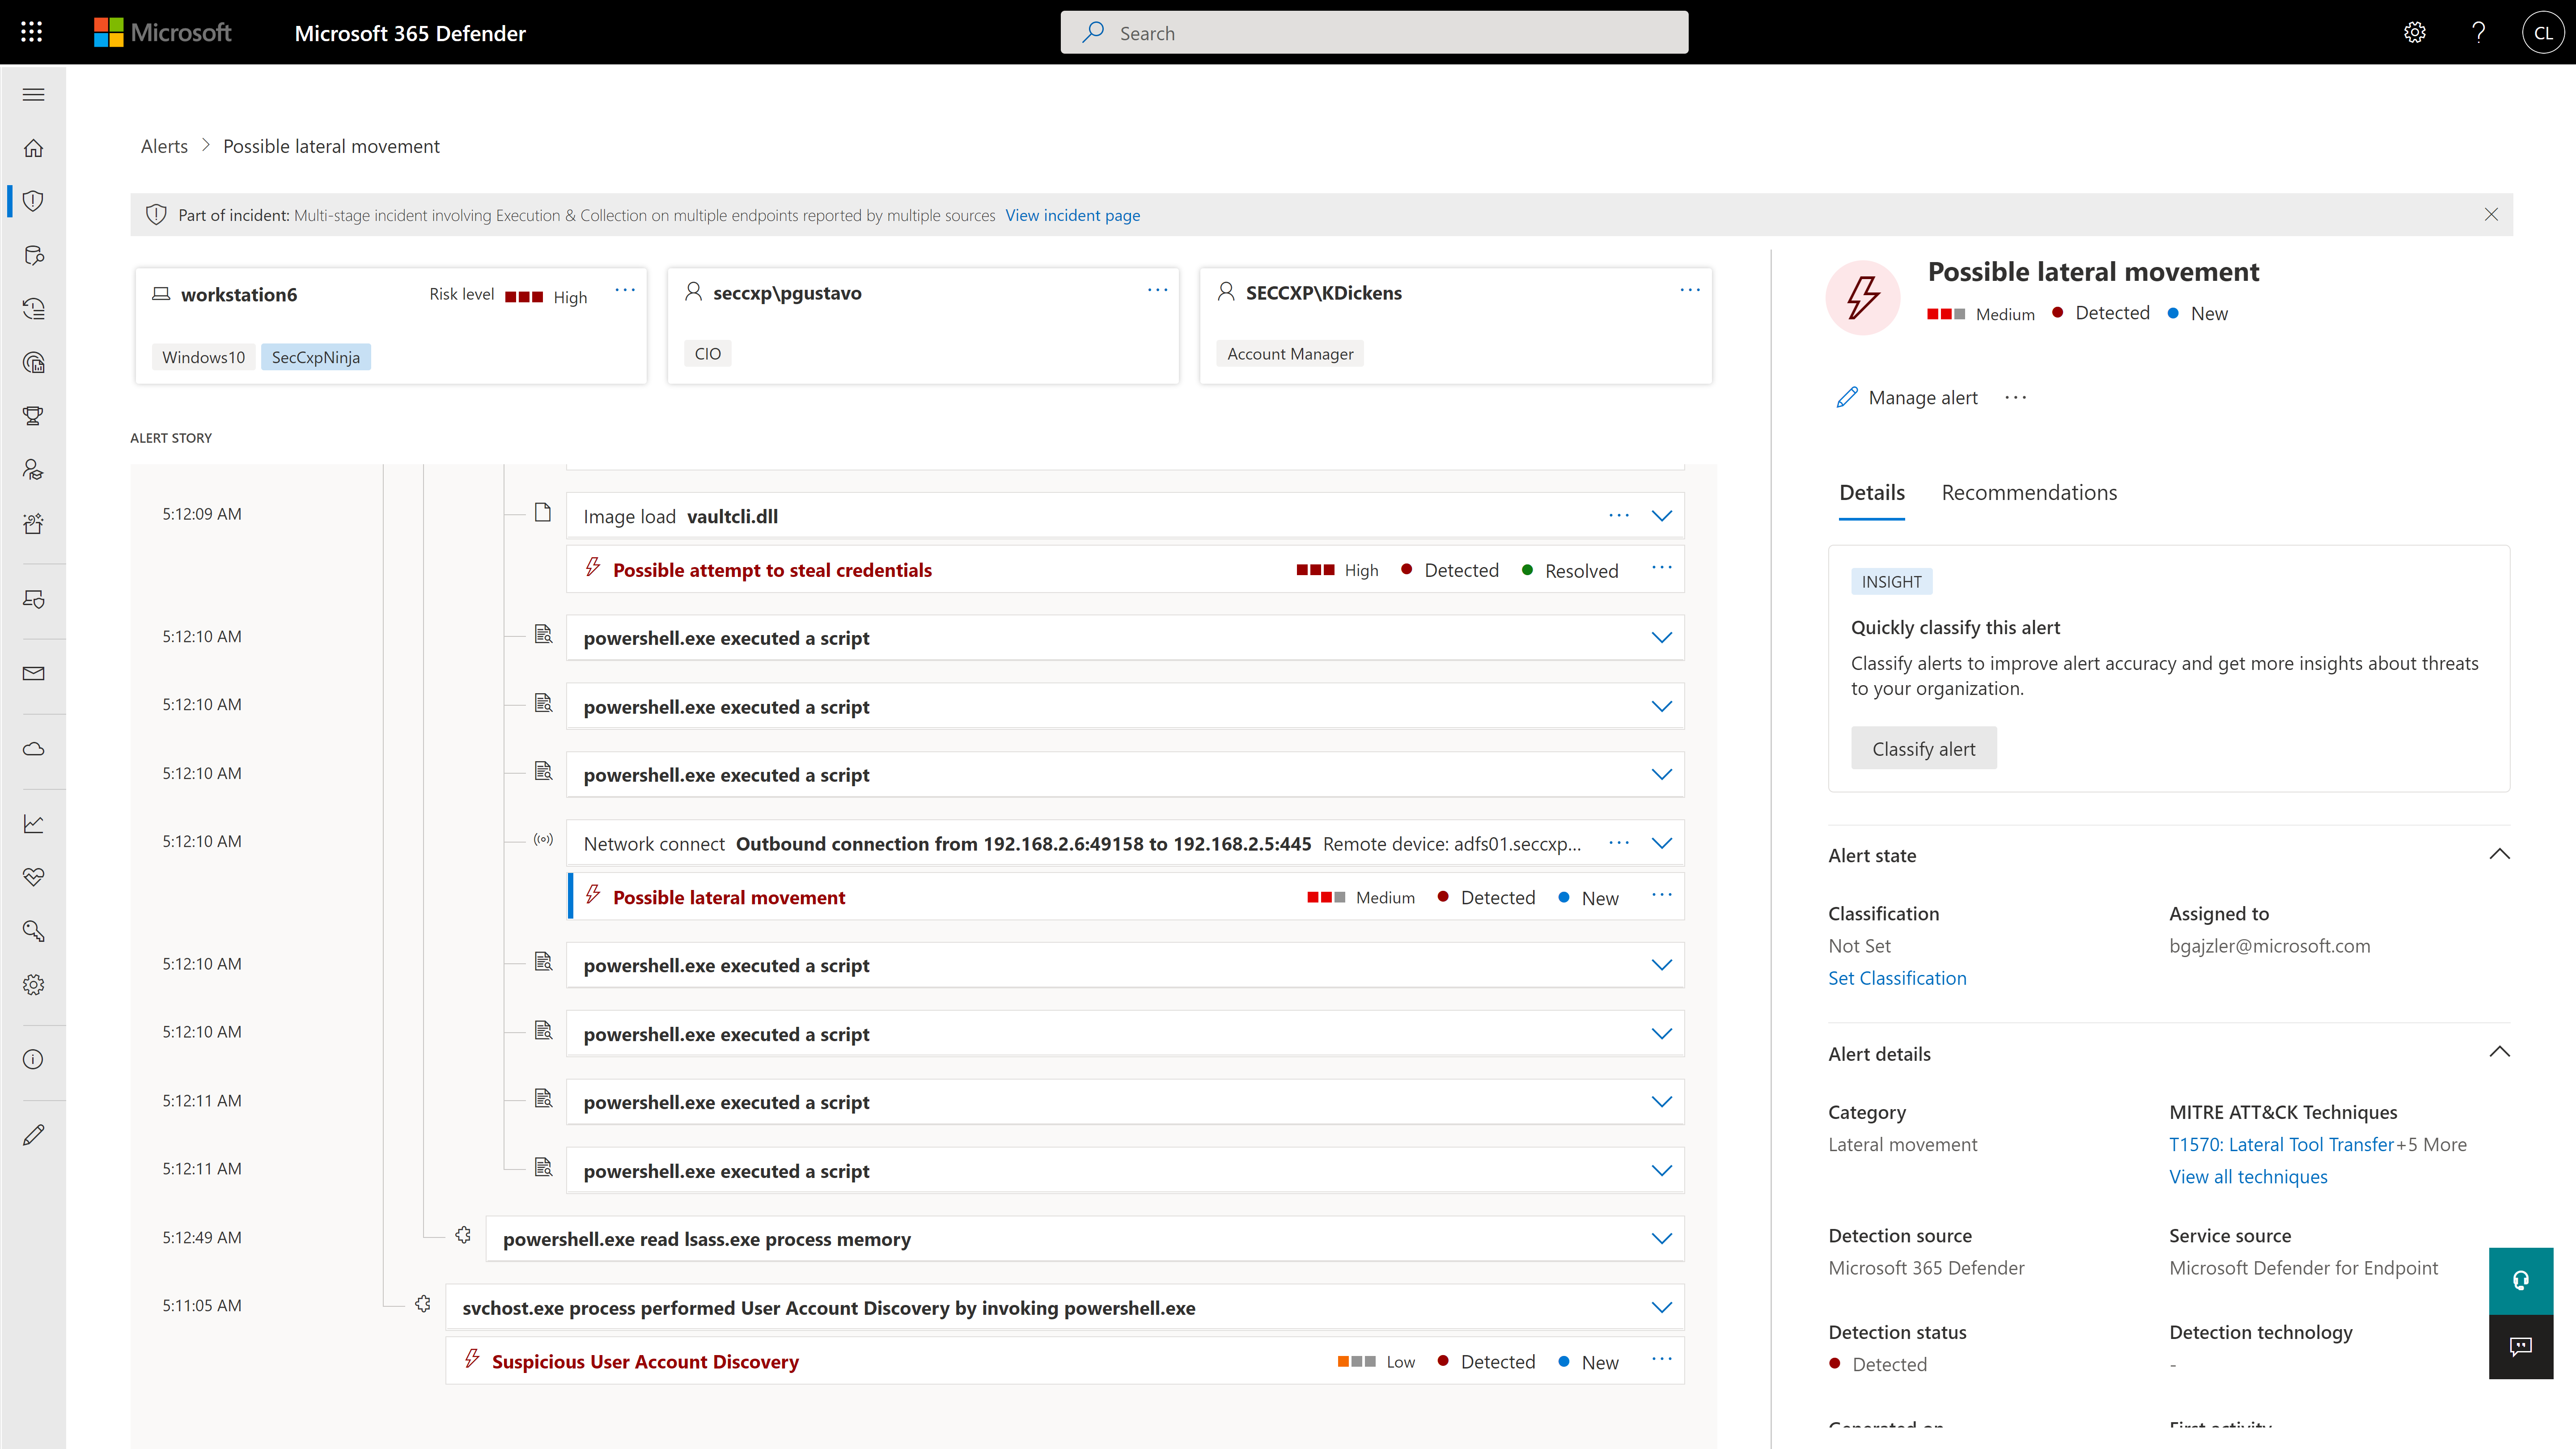
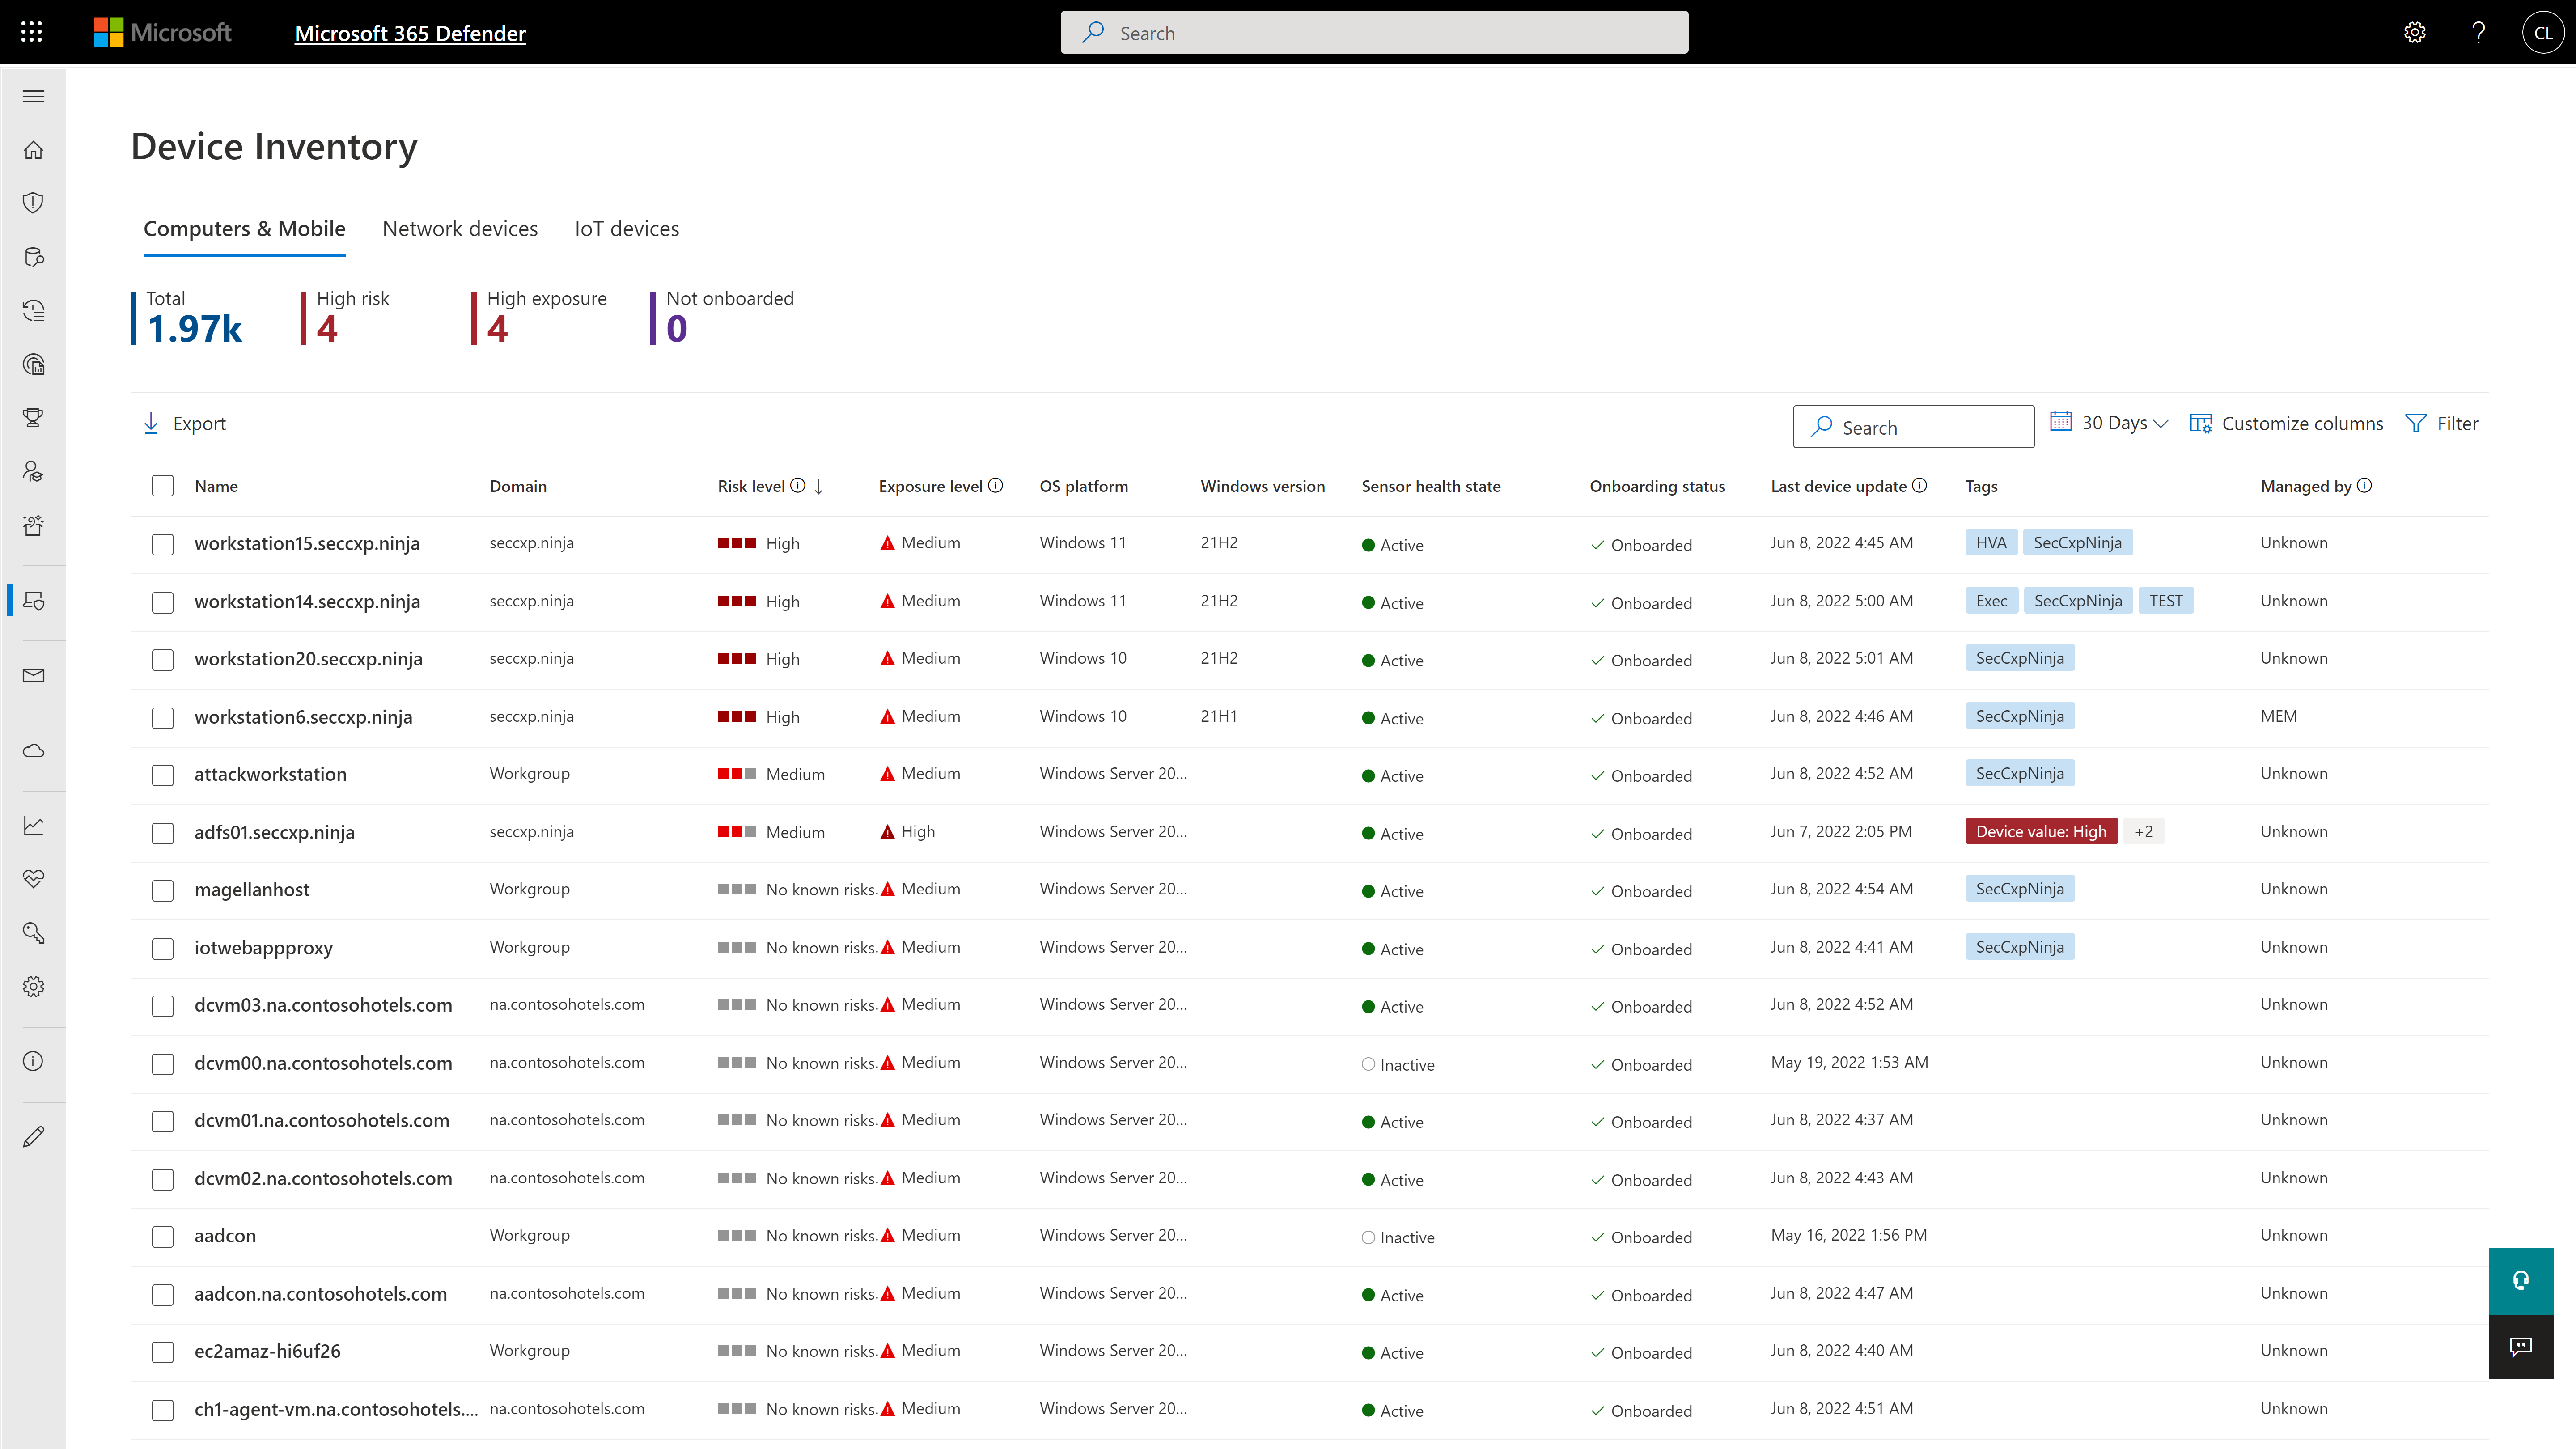
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
Microsoft's backed in email reporting tool is good but the time to resolution varies for all messages. It claims that it will help train filters to better classify messages into the tenant, but we have not seen much of that.
Barracuda offered a similar product to PhishER but …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
PhishER comes with some good features, such as PhishML, PhishRIP, PhishFlip, etc. These features help us manage phishing email reporting incidents. From reporting emails via Phish Alert Button plug-in to collecting all reported emails in one place at the PhishER dashboard. Now, the PhishML comes into play, scanning all reported emails and tagging each as clean, spam, or threat. With the help of this machine learning-based algorithm, our investigation process becomes easier. Other features, such as PhishRip, help to search and quarantine phishing emails, and PhishFlip converts a real phishing campaign to a test phishing campaign.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because of its integration with Windows, it is very easy to deploy and manage. Any IT department should be able to leverage the software and interface. The admin portal provides weighted recommendations that comprise the Secure Store, offering admins, security teams, and business owners valuable insights into their security footprint without requiring a strong security background. The software would be ideal for small and mid-sized businesses that cannot dedicate resources to security. Larger enterprises would also benefit, but may require the enhanced license.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One, it's crazy lightweight, so compared to some of the competitors that we also have used with our security services, it's really lightweight and so I don't have a lot of overhead on the system that it's running on.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
PhishRIP info tabs (i.e. if improperly check ripped emails are turned into tests. This has caused issues.) Info tabs or markers allow user to hover and get more information about what action a check box or slider provides.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
So the fact that Defender for Endpoint still works with signatures is actually, I don't know, a little difficult for us because, I mean, since Microsoft trusts those signatures, you can easily inject code. And we've done it many times. To show that you can inject code through vulnerabilities like CV 2013, 99, and 33 but still keep the signature. So because of the trust of those signatures, the malware just kind of slides into the environment without Defender knowing. That's the first part. The second part is that the behavioral analysis is not precisely its Prime. It's not Defender's best capability for endpoints. So, Defender does not identify all behaviors considered by other EDRs in the market.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
When we first discovered that KnowBe4 released something like this, we saw a demo of it and were floored at what it could do and how it could help us from a security standpoint. Gone are the days of us in IT sending out a mass email saying please don't click on anything in the email from sender "X", and it allows us to quietly and easily ensure that people don't take any action on malicious emails.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
I give it an eight for the feature set. While I only give it an eight because the complexity and interconnectedness of the tools mean that there needs to be quite a bit of RTFM to get the most out of the products.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It offers multiple security features and integrates well with Microsoft ecosystems. A workflow for threat detection, investigation, automated remediation, and a centralized dashboard is an added advantage. This application is mainly designed for experienced users; new users may feel challenged.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Harmony does not provide security awareness training or simulated phishing emails like KnowB4. However, it does provide a phish alert button & workflow similar to PhishER & we may stop using PhishER because the Phish Alert reports from PhishER don't feed into Harmony to help train it from phishing emails that go through. We got Harmony after KnowB4 because we needed a tool to PREVENT phishing emails from getting to people's inboxes in the first place, which KnowB4 has very little capability for other than PhishER+ blacklists. It is a shame KnowB4 does not have the anti threat phishing prevention like Harmony considering all the email data it has & its existing AI analytic capabilities.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cylance's policy is to block everything and requires an active person to monitor and unblock legitimate processes. As updates and software continue to evolve, it is a full-time job to be a Cylance administrator. Microsoft Defender for Endpoint is a set-and-forget solution that catches threats when they occur and leaves you to focus on your work unimpeded.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Phish/ER & PAD: Identifying email threats more quickly allowed us to send alert to the users' community in a timely manner based on the pattern of the threat.
KnowBe4 Training Campaigns have proven to noticeably increase users' awareness.
KnowBe4 Phishing Campaigns made users realize how dangerous and deceiving hacker can be.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info