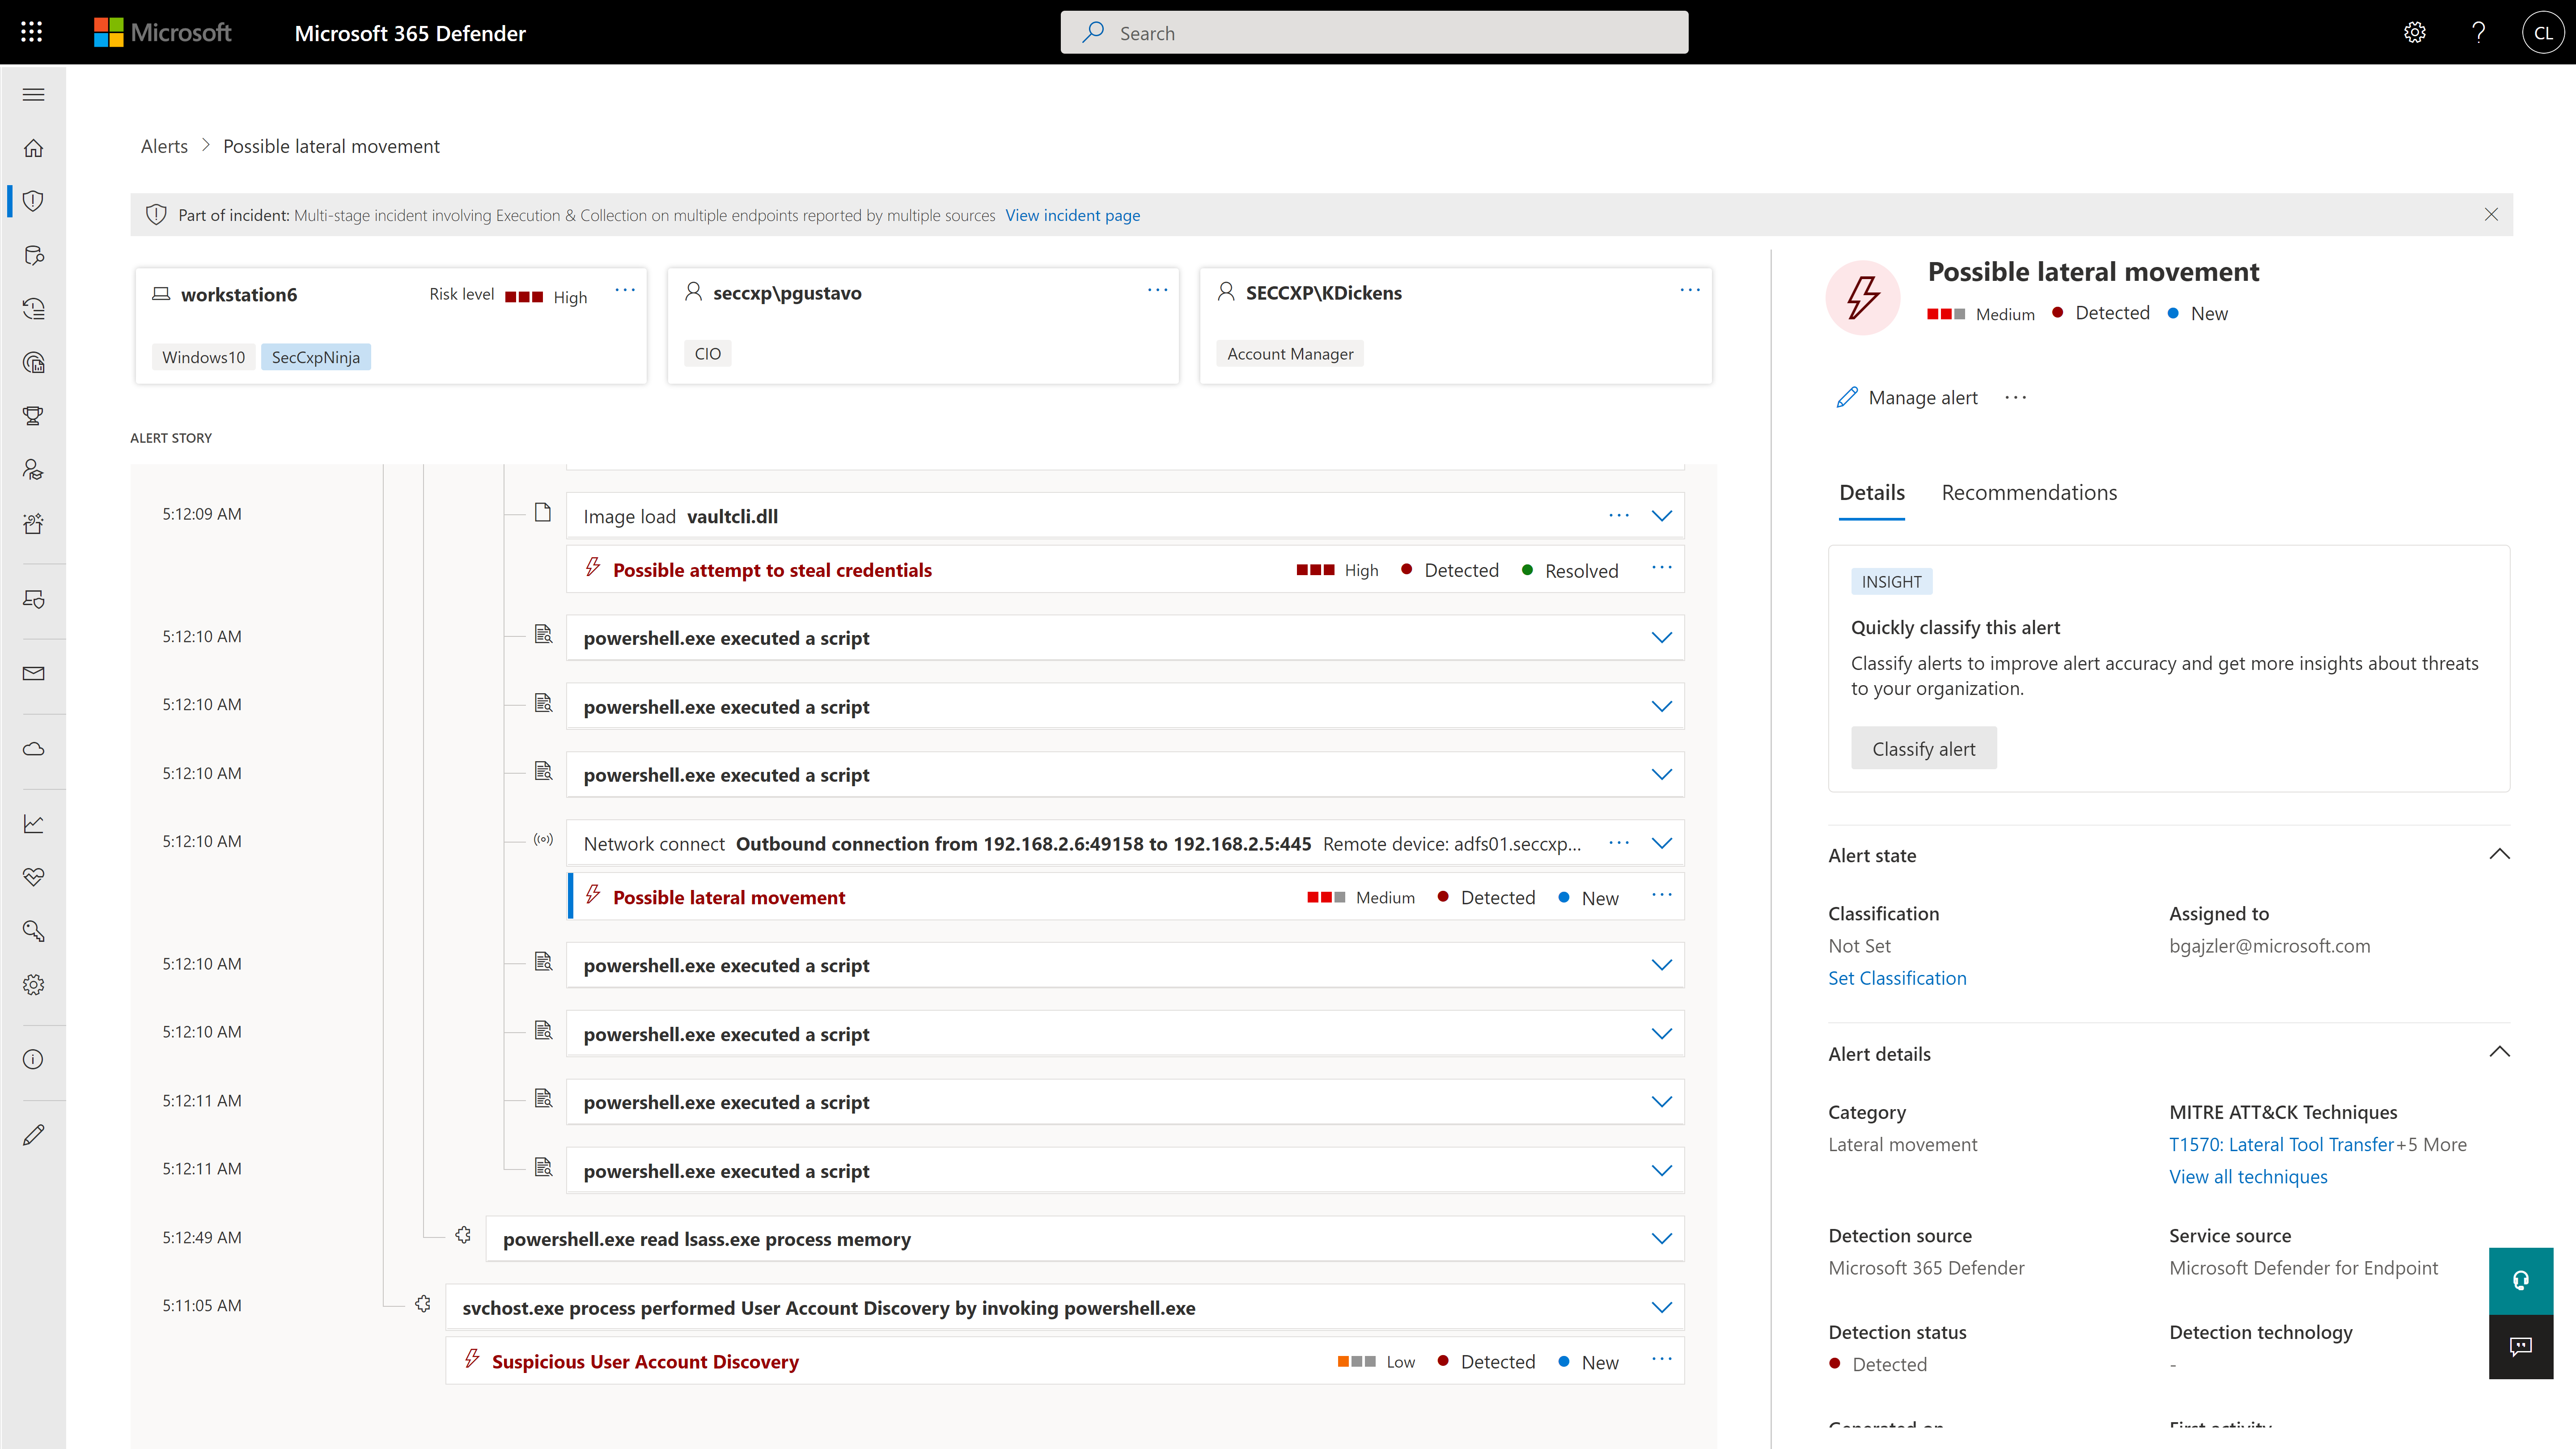
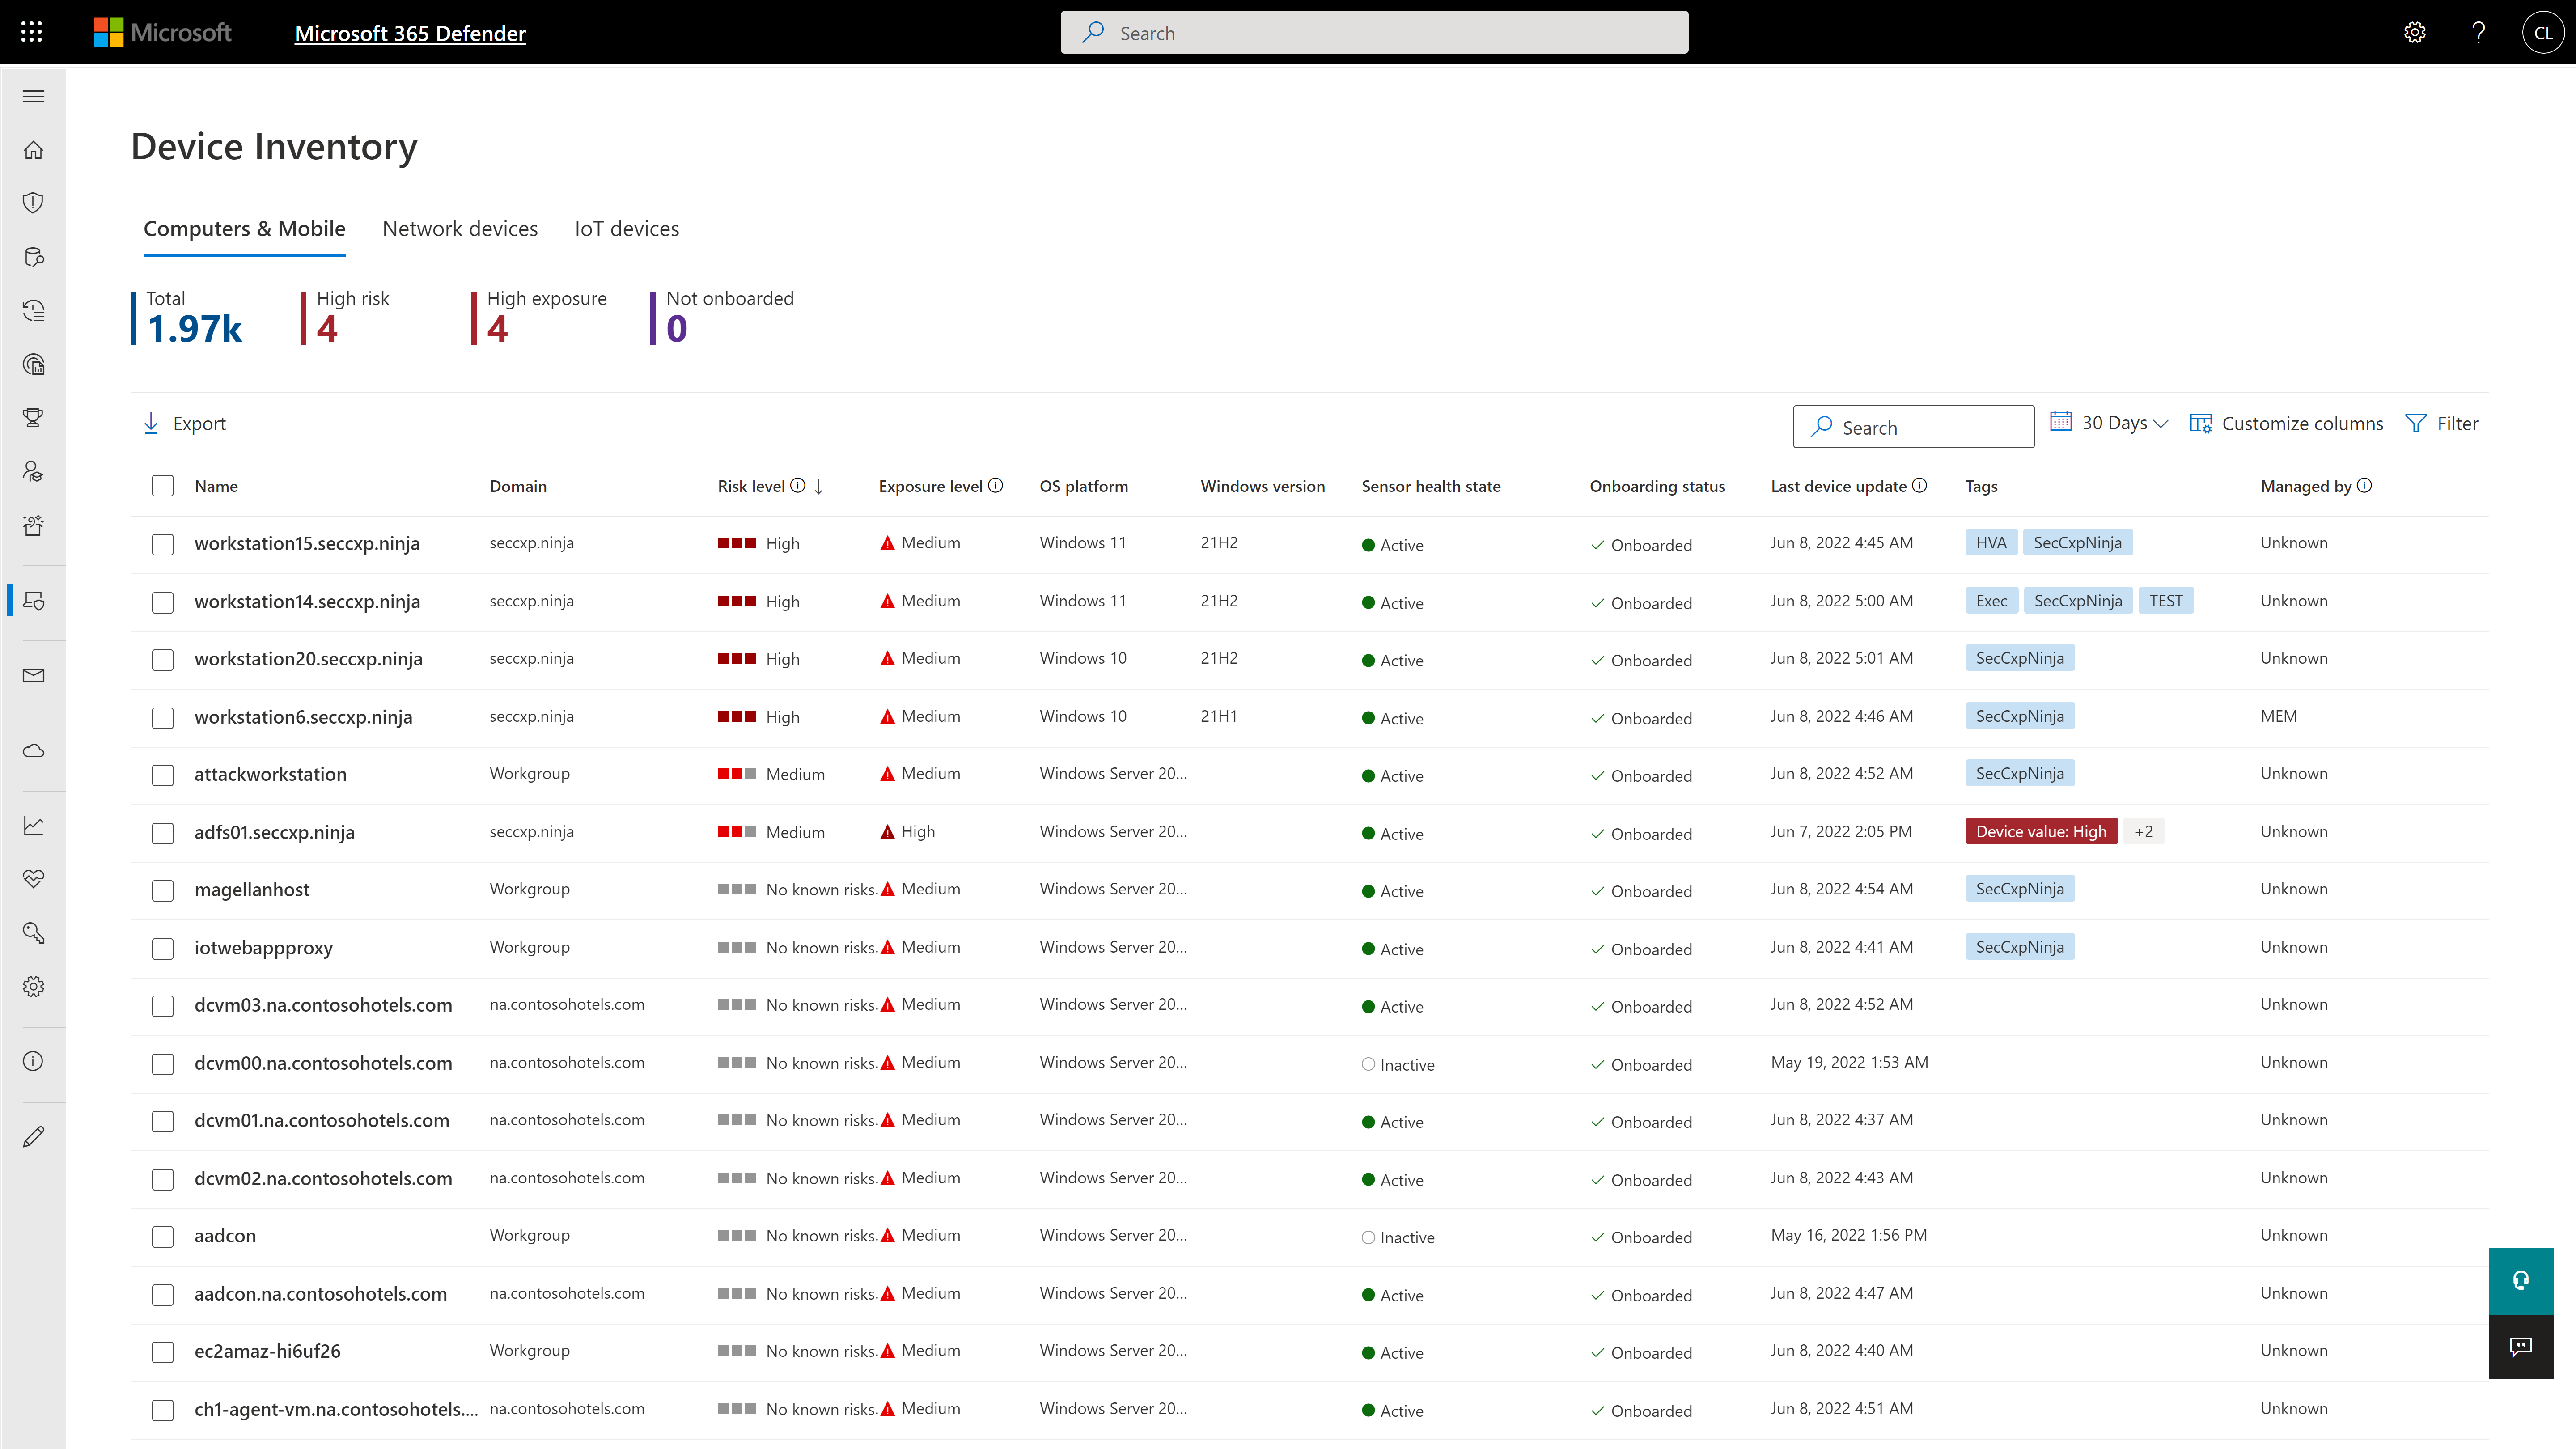
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
Pricing
Microsoft Defender for Endpoint
Editions & Modules
Academic
$2.50
per user/per month
Standalone
$5.20
per user/per month
Offerings
Pricing Offerings
Microsoft Defender for Endpoint
Free Trial
Yes
Free/Freemium Version
No
Premium Consulting/Integration Services
No
Entry-level Setup Fee
No setup fee
Additional Details
—
More Pricing Information
Community Pulse
Microsoft Defender for Endpoint
Considered Both Products
Microsoft
Verified User
Chose Microsoft Defender for Endpoint
It's very convenient and very well integrated with our environment.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Majorly because our suite is Microsoft, so make totally sense to have this in the company and the price. It is Microsoft is better than CrowdStrike.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Sophos. Because of the integration with Microsoft ecosystem, we selected Defender.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
We have not used anything else other than Microsoft Defender for Endpoint. Maybe we've used other antivirus software like Sophos and things like that. They're just not all encompassing and that's why we moved to use this product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cybersecurity Senior Engineer in Information Technology at Maureen Data Systems (MDS) (Information Technology & Services, 201-500 employees)
Chose Microsoft Defender for Endpoint
I have been working with customers that they are transitioning from Sentinel One, CrowdStrike to Defender for Endpoint, right? So I think it's because they see the value in the product and also they see how much they can save in terms of the cost for companies because they …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cybersecurity Director in Information Technology at Impresoft 4ward (Information Technology & Services, 501-1000 employees)
Chose Microsoft Defender for Endpoint
We previously used CrowdStrike on our servers. However, the seamless integration of Microsoft Defender (MD) with XDR and the entire Microsoft ecosystem led us to choose Microsoft Defender for Endpoint (MDE).
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
What we love more about this product is the way this pro gets integrated into the other family of solutions, especially Defender for Identity or the XDR solutions. We think that the market, the customers are full of unattended consults coming out from different vendors and that …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Lead Engineer in Information Technology at Rohde-Schwarz (Information Technology & Services, 5001-10,000 employees)
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint is more advantageous in our windows heavy infrastructure and it was unparalled in the ease of integration with windows endpoints. Security breaches, system crashes and outages with other competitors like Crowdstrike made it easier for us to go …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Senior Cyber Security Consultant in Information Technology at LTIMindtree (Information Technology & Services, 5001-10,000 employees)
Chose Microsoft Defender for Endpoint
CrowdStrike Falcon is also a good solution for endpoint protection which offer EDR Soultion, threat hunting and AI driven threat protection. Sophos Intercept X combines next-gen antivirus with advanced EDR capabilities with its deep learning technology, exploit prevention, and …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint is unique for its effortless deployment into the Microsoft ecosystem, where it taps the broadest set of threat intelligence from more than 1.5 billion endpoints. Its state-of-the-art AI-powered automated investigation and remediation minimize …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
We started onboarding macOS devices on jamf and started managing it. Because Defender for Endpoint is not working as expected for and compared to price and functionality we are switching from it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Microsoft Defender for Endpoint
CrowdStrike and SentinelOne. CrowdStrike, you have to deploy it, but it's the defender, it's already baked into the operating system. Same thing with SentinelOne.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Easier to integrate, less hidden fees, easier to maintain, and easier to update. Support is much better on the Microsoft side than CrowdStrike.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
I don't think, it's not really something that we were just using Microsoft and it was just an easy thing to do.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
I'm not familiar. It's just been one year plus that I started using, so I've just started using Defender, so I really don't know how to compare it with others.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
I would say at the end all they are doing the same, but with the benefit that we don't need to install anything. So it's just kind of enabling and then the functionality is available, so other products need to be installed, which is not necessary with the defend
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
We use Defender in the cloud. We are currently using Defender in the cloud and also evaluating the XDR solution for programmatic. It's just arguments, the defense in depth. You have Defender Endpoint and then you have what you have in the cloud as well, so it's just augmenting …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Application Evaluator at University of Tampa (Higher Education, 1001-5000 employees)
Chose Microsoft Defender for Endpoint
Before using Defender for Endpoint, we basically had the starter version of the Microsoft product, which comes prebuilt into the system. We had them using in the initial run, but then what usually happened was the employees started disabling it, and that usually made, we guys …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
I am a big fan of Tanium actually, so I think it is good. Tanium seemed like it was maybe a little bit easier, but maybe the capability was lacking. Maybe that's the reason why it seems like Defender for Endpoint might be a little harder to understand. There might just be more …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
CrowdStrike Falcon, and Sentinel One are other big ones that we use a bit. Cisco Secure Endpoint we've evaluated as well. Cisco Secure Endpoint capability-wise doesn't match up to Defender, SentinelOne, and CrowdStrike both do, but the cost profiles are a bit higher. So most of …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
I would say not to name specific company names, because I'm a partner with one of them and that's the account that I work with. But I use some competing solutions that I would say are pretty heavy from an overhead perspective with the agent that has to be installed in the …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Because of its integration with Windows, it is very easy to deploy and manage. Any IT department should be able to leverage the software and interface. The admin portal provides weighted recommendations that comprise the Secure Store, offering admins, security teams, and business owners valuable insights into their security footprint without requiring a strong security background. The software would be ideal for small and mid-sized businesses that cannot dedicate resources to security. Larger enterprises would also benefit, but may require the enhanced license.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
One, it's crazy lightweight, so compared to some of the competitors that we also have used with our security services, it's really lightweight and so I don't have a lot of overhead on the system that it's running on.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
So the fact that Defender for Endpoint still works with signatures is actually, I don't know, a little difficult for us because, I mean, since Microsoft trusts those signatures, you can easily inject code. And we've done it many times. To show that you can inject code through vulnerabilities like CV 2013, 99, and 33 but still keep the signature. So because of the trust of those signatures, the malware just kind of slides into the environment without Defender knowing. That's the first part. The second part is that the behavioral analysis is not precisely its Prime. It's not Defender's best capability for endpoints. So, Defender does not identify all behaviors considered by other EDRs in the market.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It offers multiple security features and integrates well with Microsoft ecosystems. A workflow for threat detection, investigation, automated remediation, and a centralized dashboard is an added advantage. This application is mainly designed for experienced users; new users may feel challenged.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cylance's policy is to block everything and requires an active person to monitor and unblock legitimate processes. As updates and software continue to evolve, it is a full-time job to be a Cylance administrator. Microsoft Defender for Endpoint is a set-and-forget solution that catches threats when they occur and leaves you to focus on your work unimpeded.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info