Cylance, a Blackberry company since the early 2019 acquisition, developed their flagship business antivirus and endpoint protection software in CylancePROTECT, featured in business and home editions boasting artificial intelligence guided protection. BlackBerry Protect is a post-acquisition evolution of CylanceProtect.
N/A
Microsoft Defender for Endpoint
Score8.7 out of 10
N/A
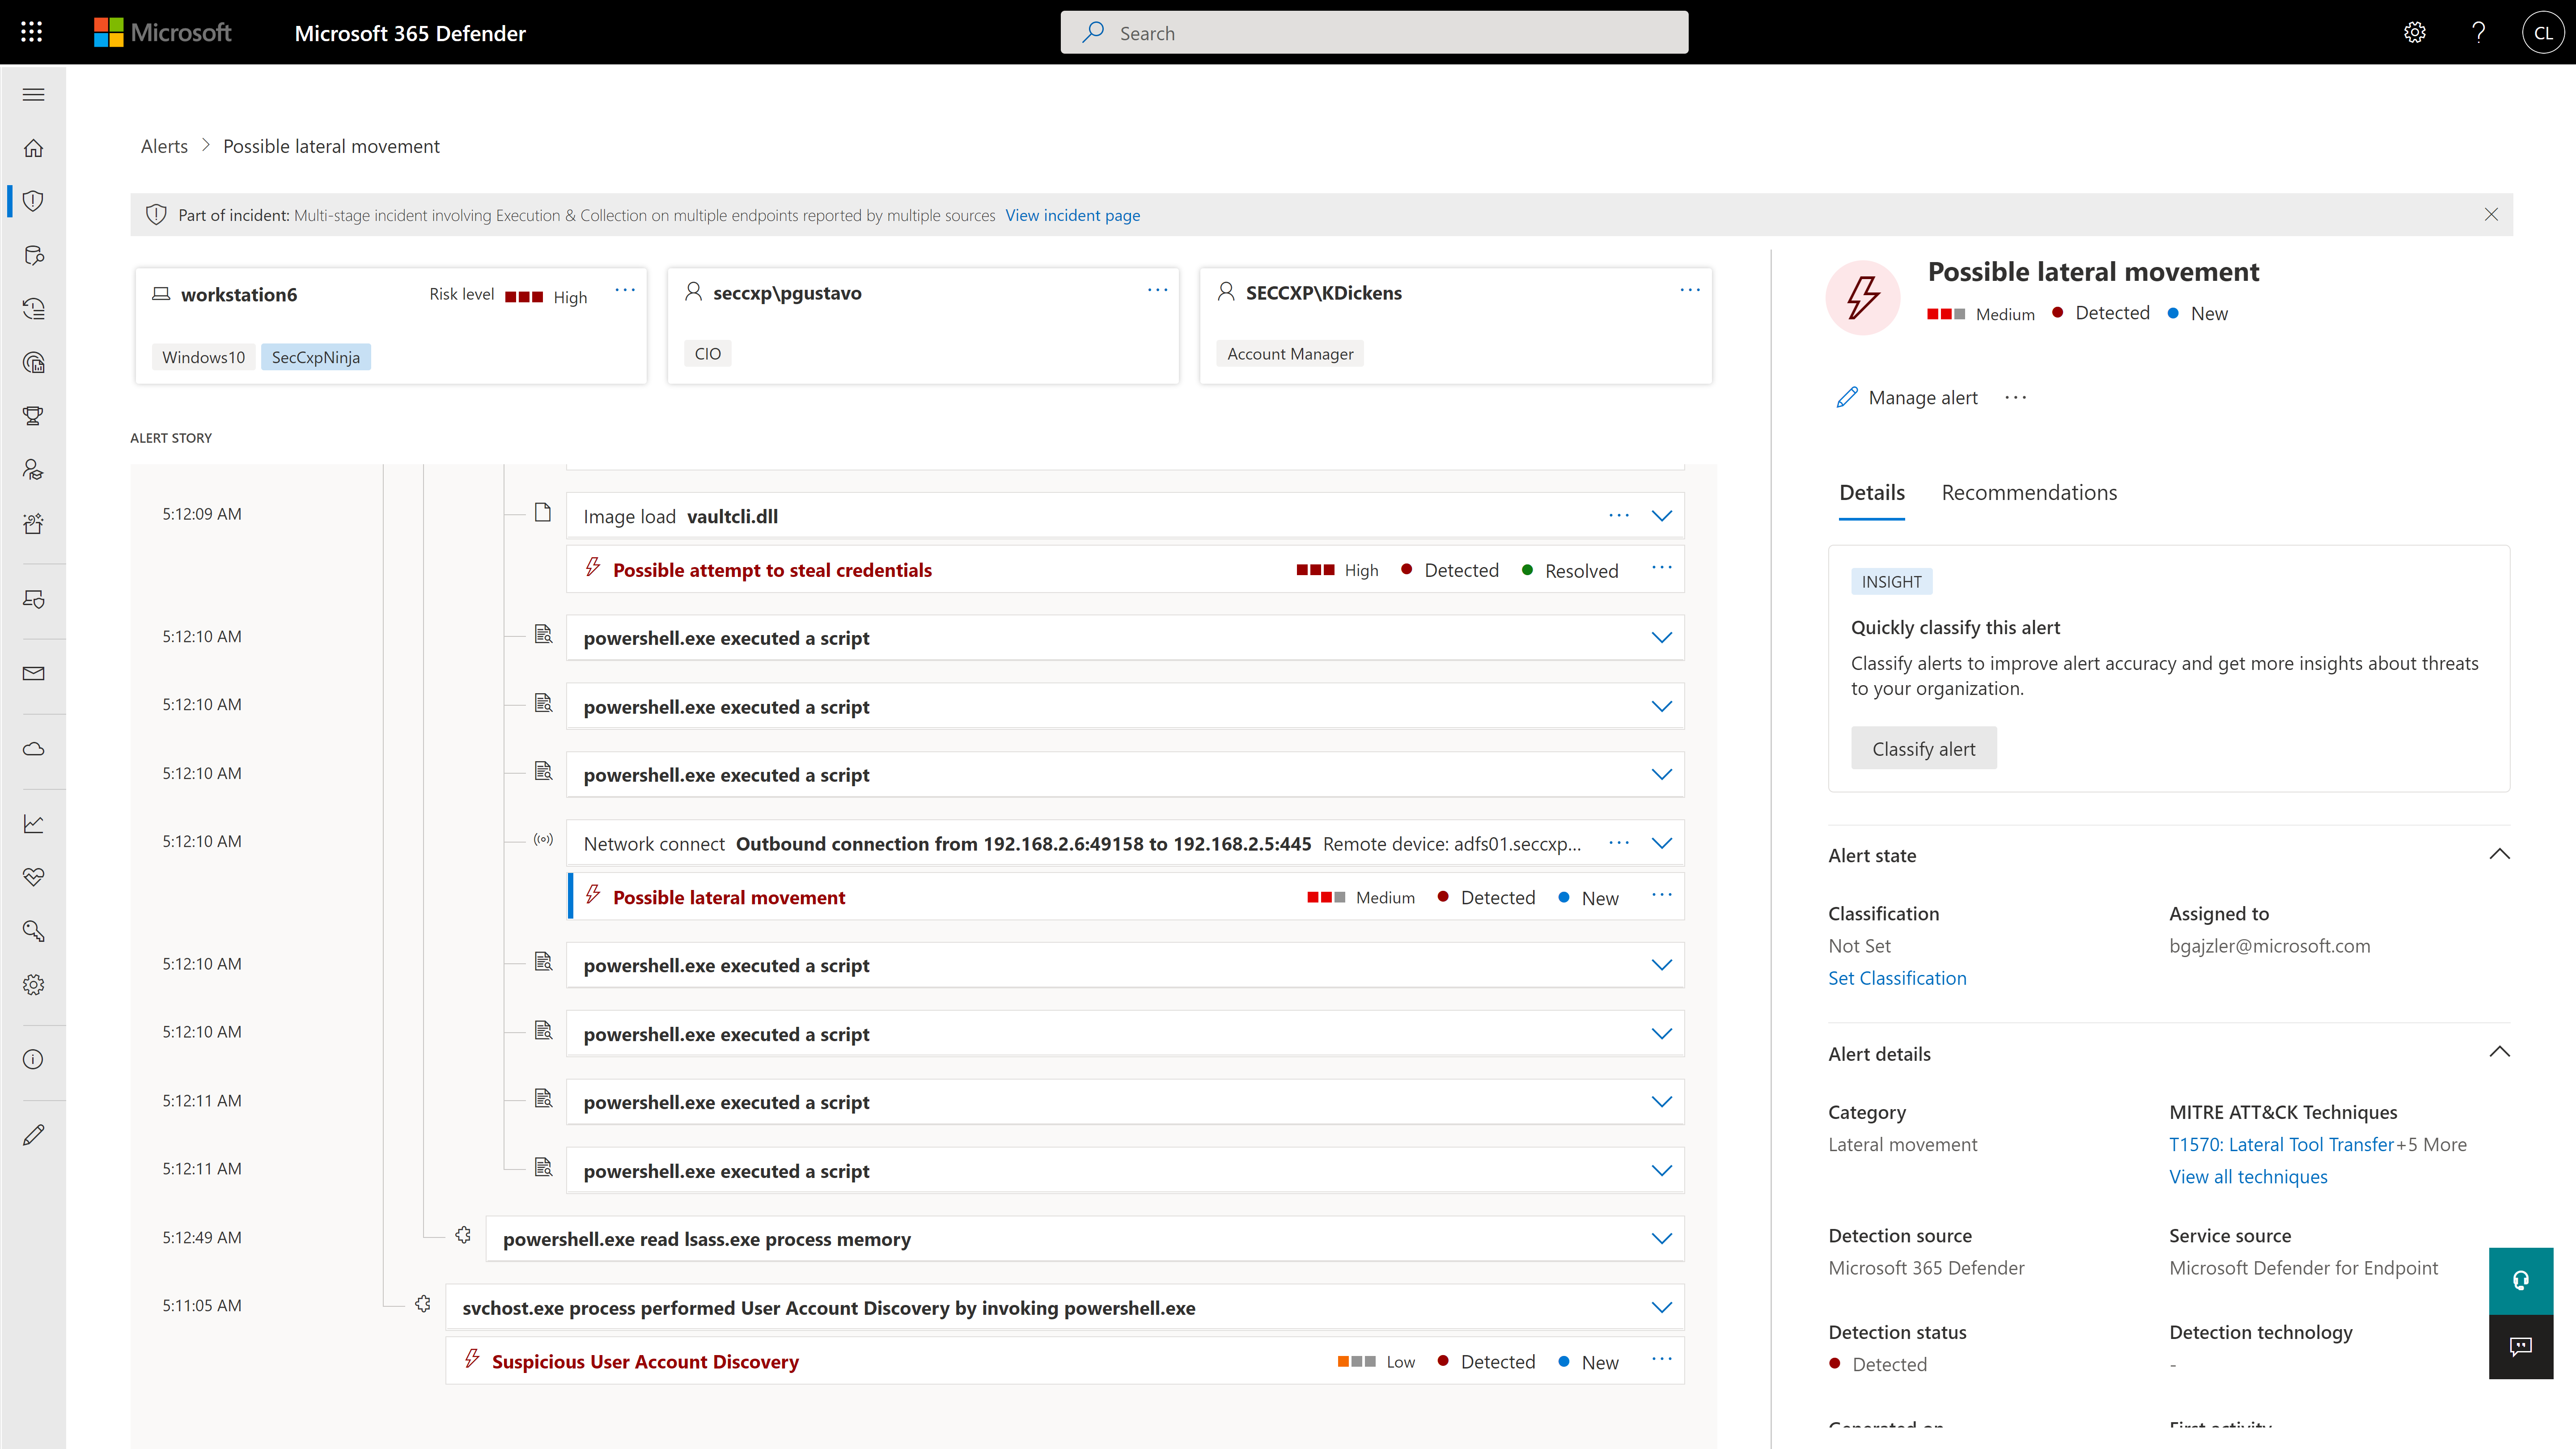
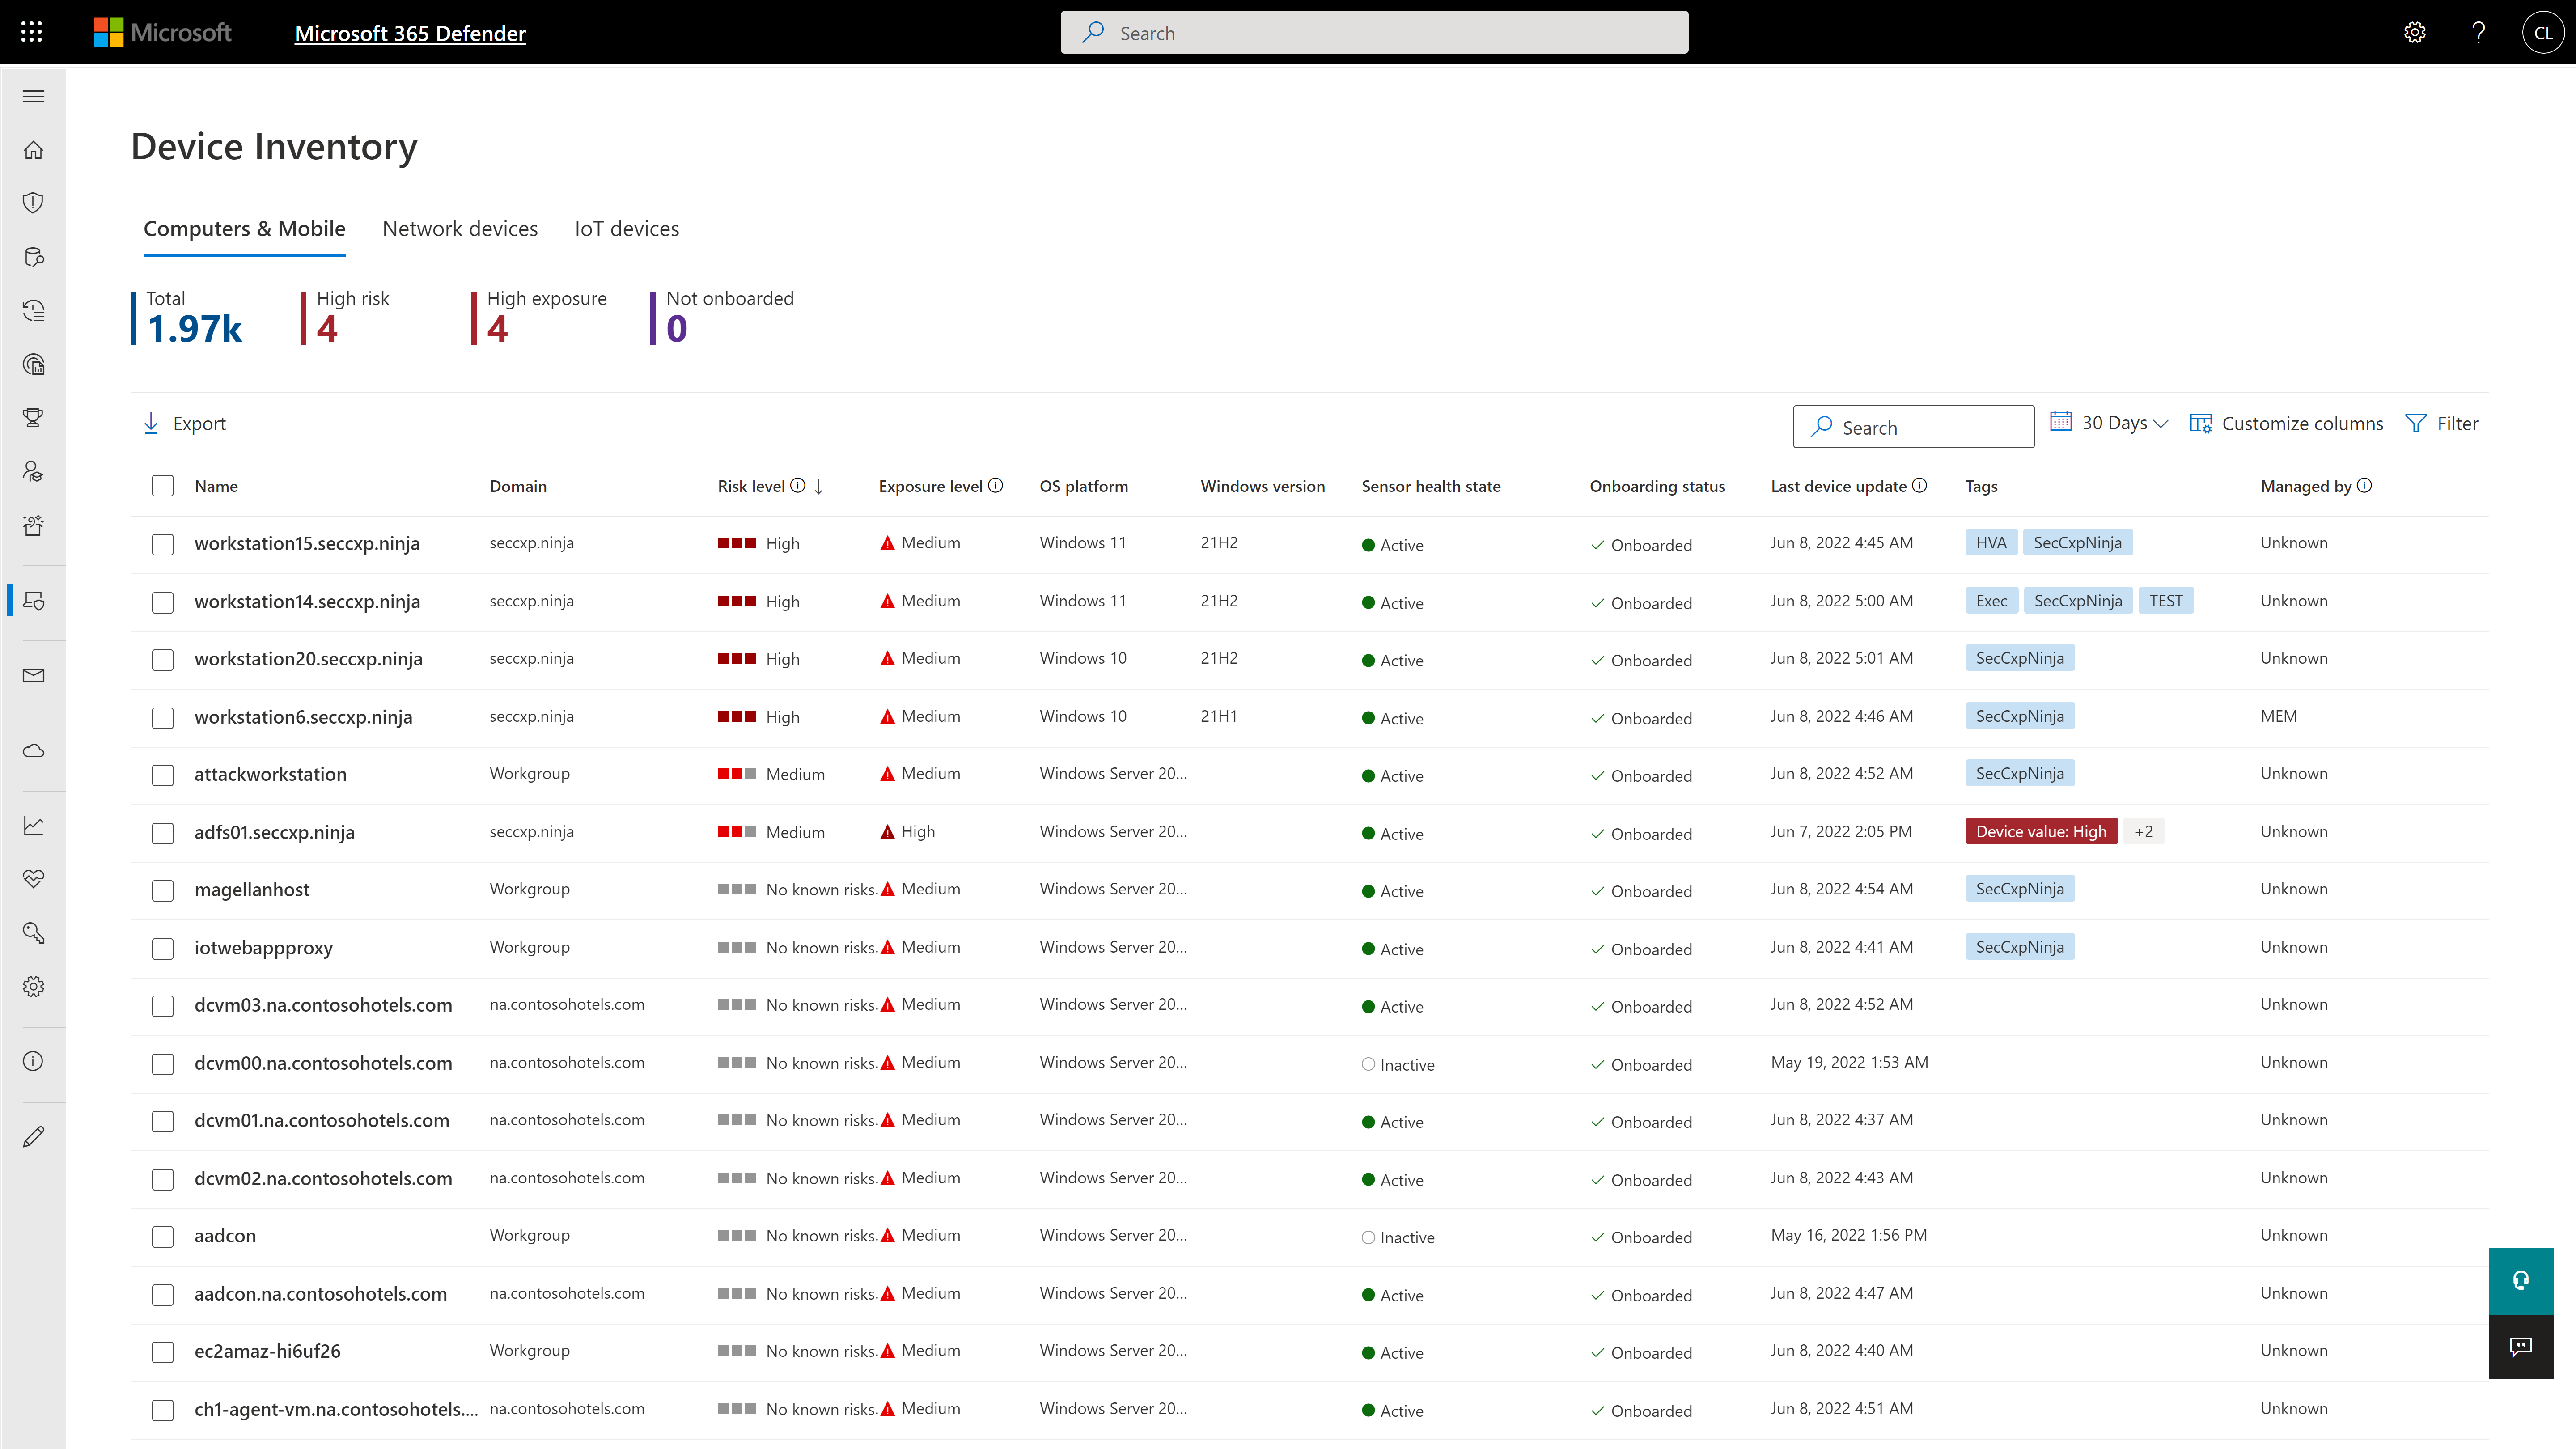
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
Pricing
BlackBerry Protect (CylancePROTECT)
Microsoft Defender for Endpoint
Editions & Modules
No answers on this topic
Academic
$2.50
per user/per month
Standalone
$5.20
per user/per month
Offerings
Pricing Offerings
BlackBerry Protect (CylancePROTECT)
Microsoft Defender for Endpoint
Free Trial
No
Yes
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
—
—
More Pricing Information
Community Pulse
BlackBerry Protect (CylancePROTECT)
Microsoft Defender for Endpoint
Considered Both Products
BlackBerry
No answer on this topic
Microsoft
Verified User
Chose Microsoft Defender for Endpoint
Cylance's policy is to block everything and requires an active person to monitor and unblock legitimate processes. As updates and software continue to evolve, it is a full-time job to be a Cylance administrator. Microsoft Defender for Endpoint is a set-and-forget solution that …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The policies that you make is where it's key. The "less you let people do, the better it will be" so to speak. So if you really clamp down on a policy and don't let people do specific things, then it'll be better for you. It also helps to protect the "not so tech savvy" people as well. Basically the same thing as above, if you have users that need more flexibility, on occasion the policies might come into play and interfere if you're not careful.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Because of its integration with Windows, it is very easy to deploy and manage. Any IT department should be able to leverage the software and interface. The admin portal provides weighted recommendations that comprise the Secure Store, offering admins, security teams, and business owners valuable insights into their security footprint without requiring a strong security background. The software would be ideal for small and mid-sized businesses that cannot dedicate resources to security. Larger enterprises would also benefit, but may require the enhanced license.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Fast and Unobtrusive, users hardly notice that Cylance is running on their computer, except when it detects something malicious
User interface is simple for end users, and the management interface is streamlined and easy to get started with. The management interface has a quick tutorial that comes up upon first login that explains all the different aspects of how to configure CylanceProtect.
Customer support is fantastic - in that if you get stuck or need help understanding a feature/setting, they are quick to respond and help to ensure that your configuration is set as optimal as possible for your scenarios.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One, it's crazy lightweight, so compared to some of the competitors that we also have used with our security services, it's really lightweight and so I don't have a lot of overhead on the system that it's running on.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It would be great if there was a way for an administrator to make a file as safe from the end user device when a false positive has occurred (which is rare). At present and administrator has to log into the web console, create an exception and then wait 60-120 seconds for this to be effective on the end user device, still great, but this can be frustrating for users that are urgently trying to use the file.
Executive reporting could be better. Just a single page dashboard report that could be included in other monthly reporting.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
So the fact that Defender for Endpoint still works with signatures is actually, I don't know, a little difficult for us because, I mean, since Microsoft trusts those signatures, you can easily inject code. And we've done it many times. To show that you can inject code through vulnerabilities like CV 2013, 99, and 33 but still keep the signature. So because of the trust of those signatures, the malware just kind of slides into the environment without Defender knowing. That's the first part. The second part is that the behavioral analysis is not precisely its Prime. It's not Defender's best capability for endpoints. So, Defender does not identify all behaviors considered by other EDRs in the market.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It offers multiple security features and integrates well with Microsoft ecosystems. A workflow for threat detection, investigation, automated remediation, and a centralized dashboard is an added advantage. This application is mainly designed for experienced users; new users may feel challenged.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I have only used CylancePROTECT support one time and they were very fast and responsive with the answers that solved my issue. That is the only reason I gave them a 7 as I have only had one interaction with them.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cylance, I believe is the only one that uses the predict and prevent execution of advanced threats and malware at the endpoint. Cylance is by far a superior product.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cylance's policy is to block everything and requires an active person to monitor and unblock legitimate processes. As updates and software continue to evolve, it is a full-time job to be a Cylance administrator. Microsoft Defender for Endpoint is a set-and-forget solution that catches threats when they occur and leaves you to focus on your work unimpeded.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info