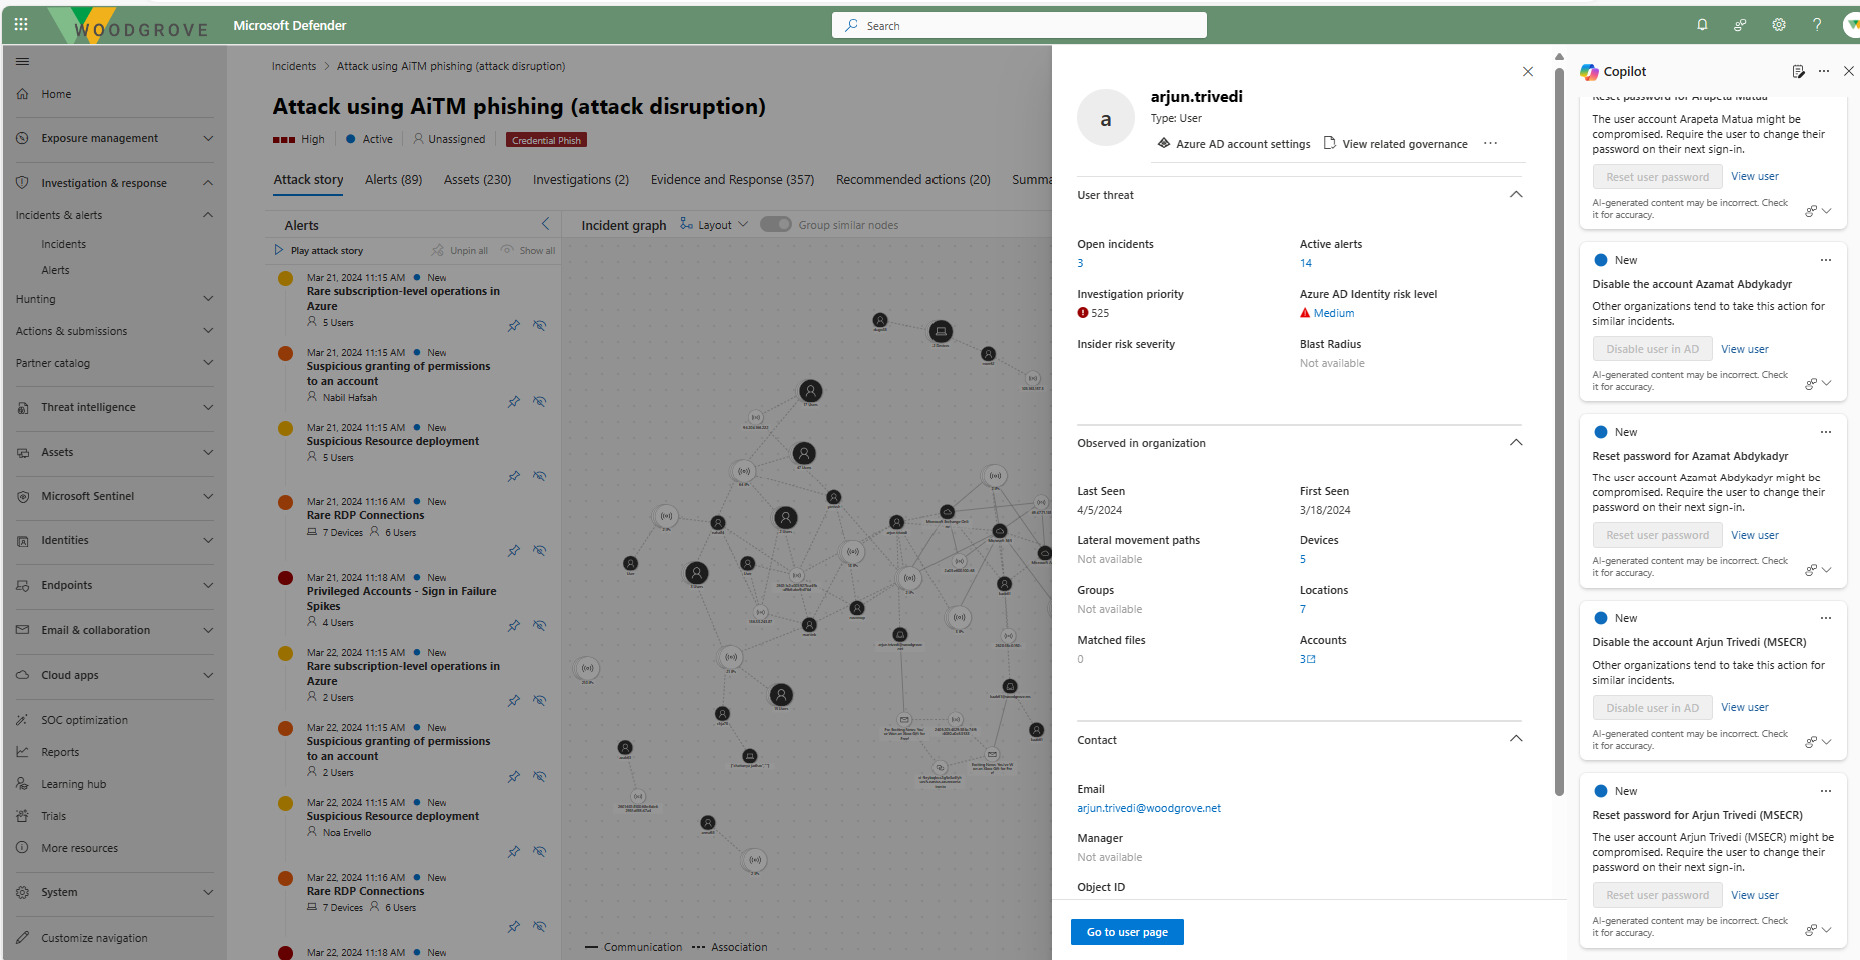
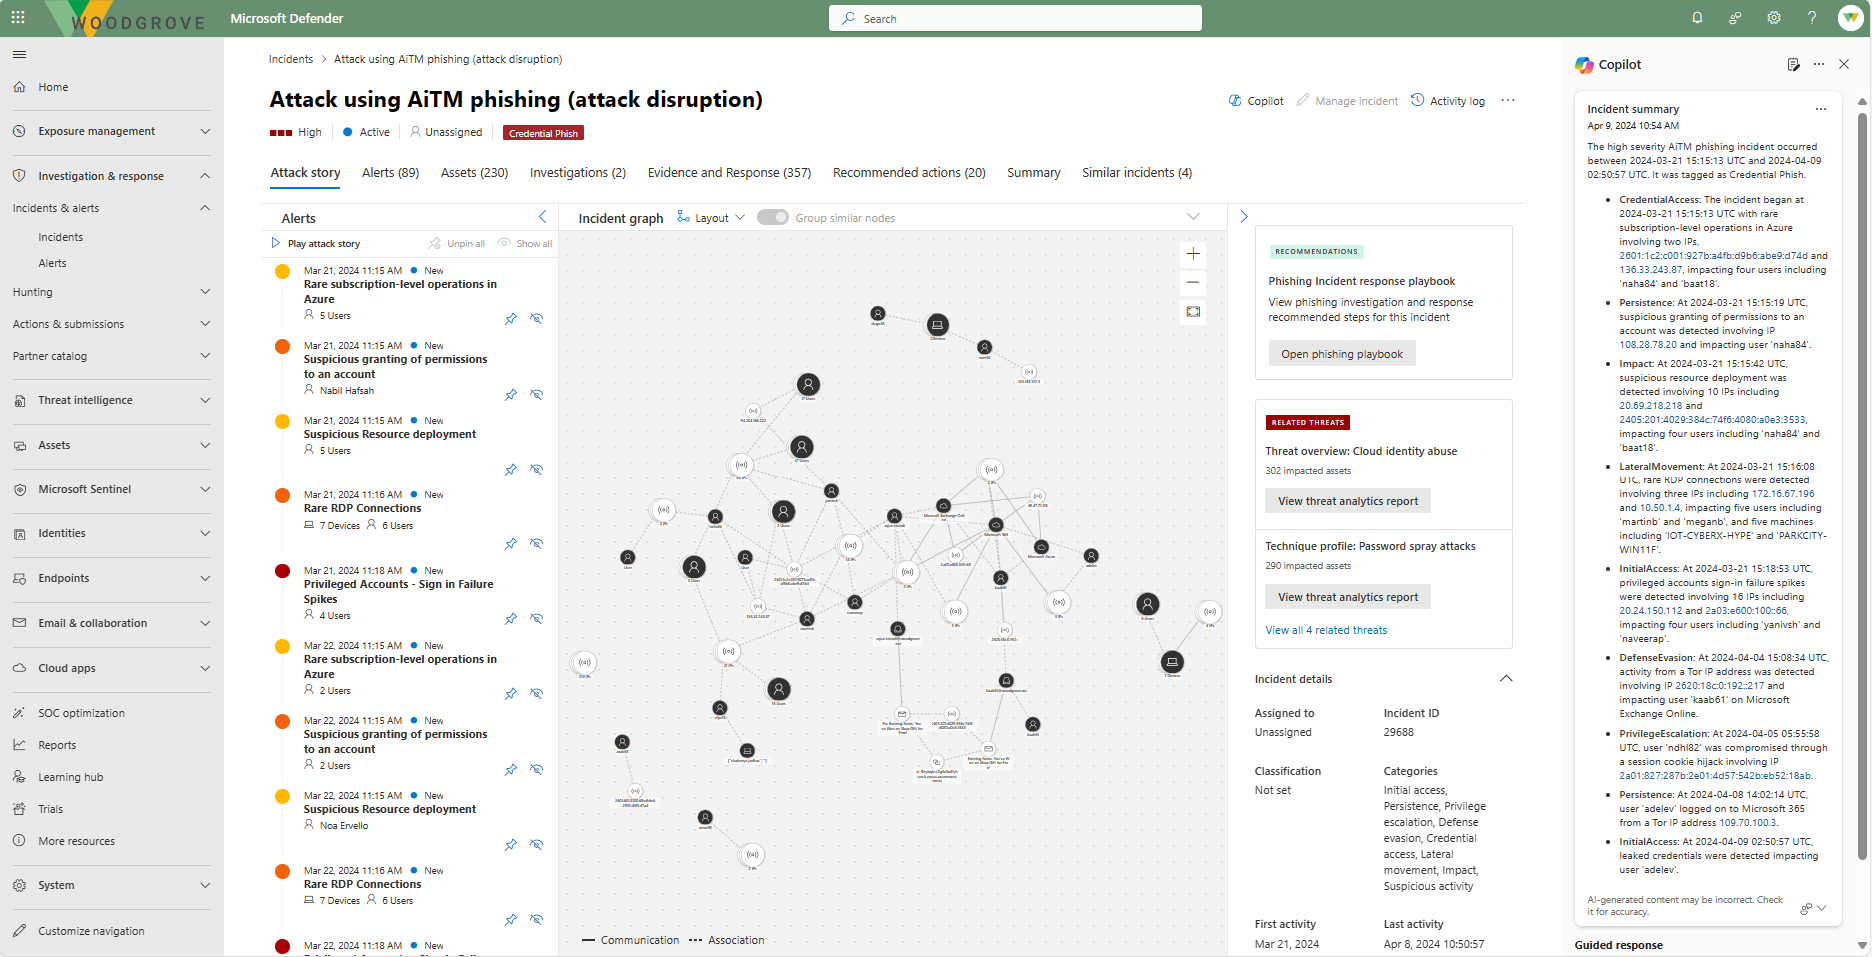
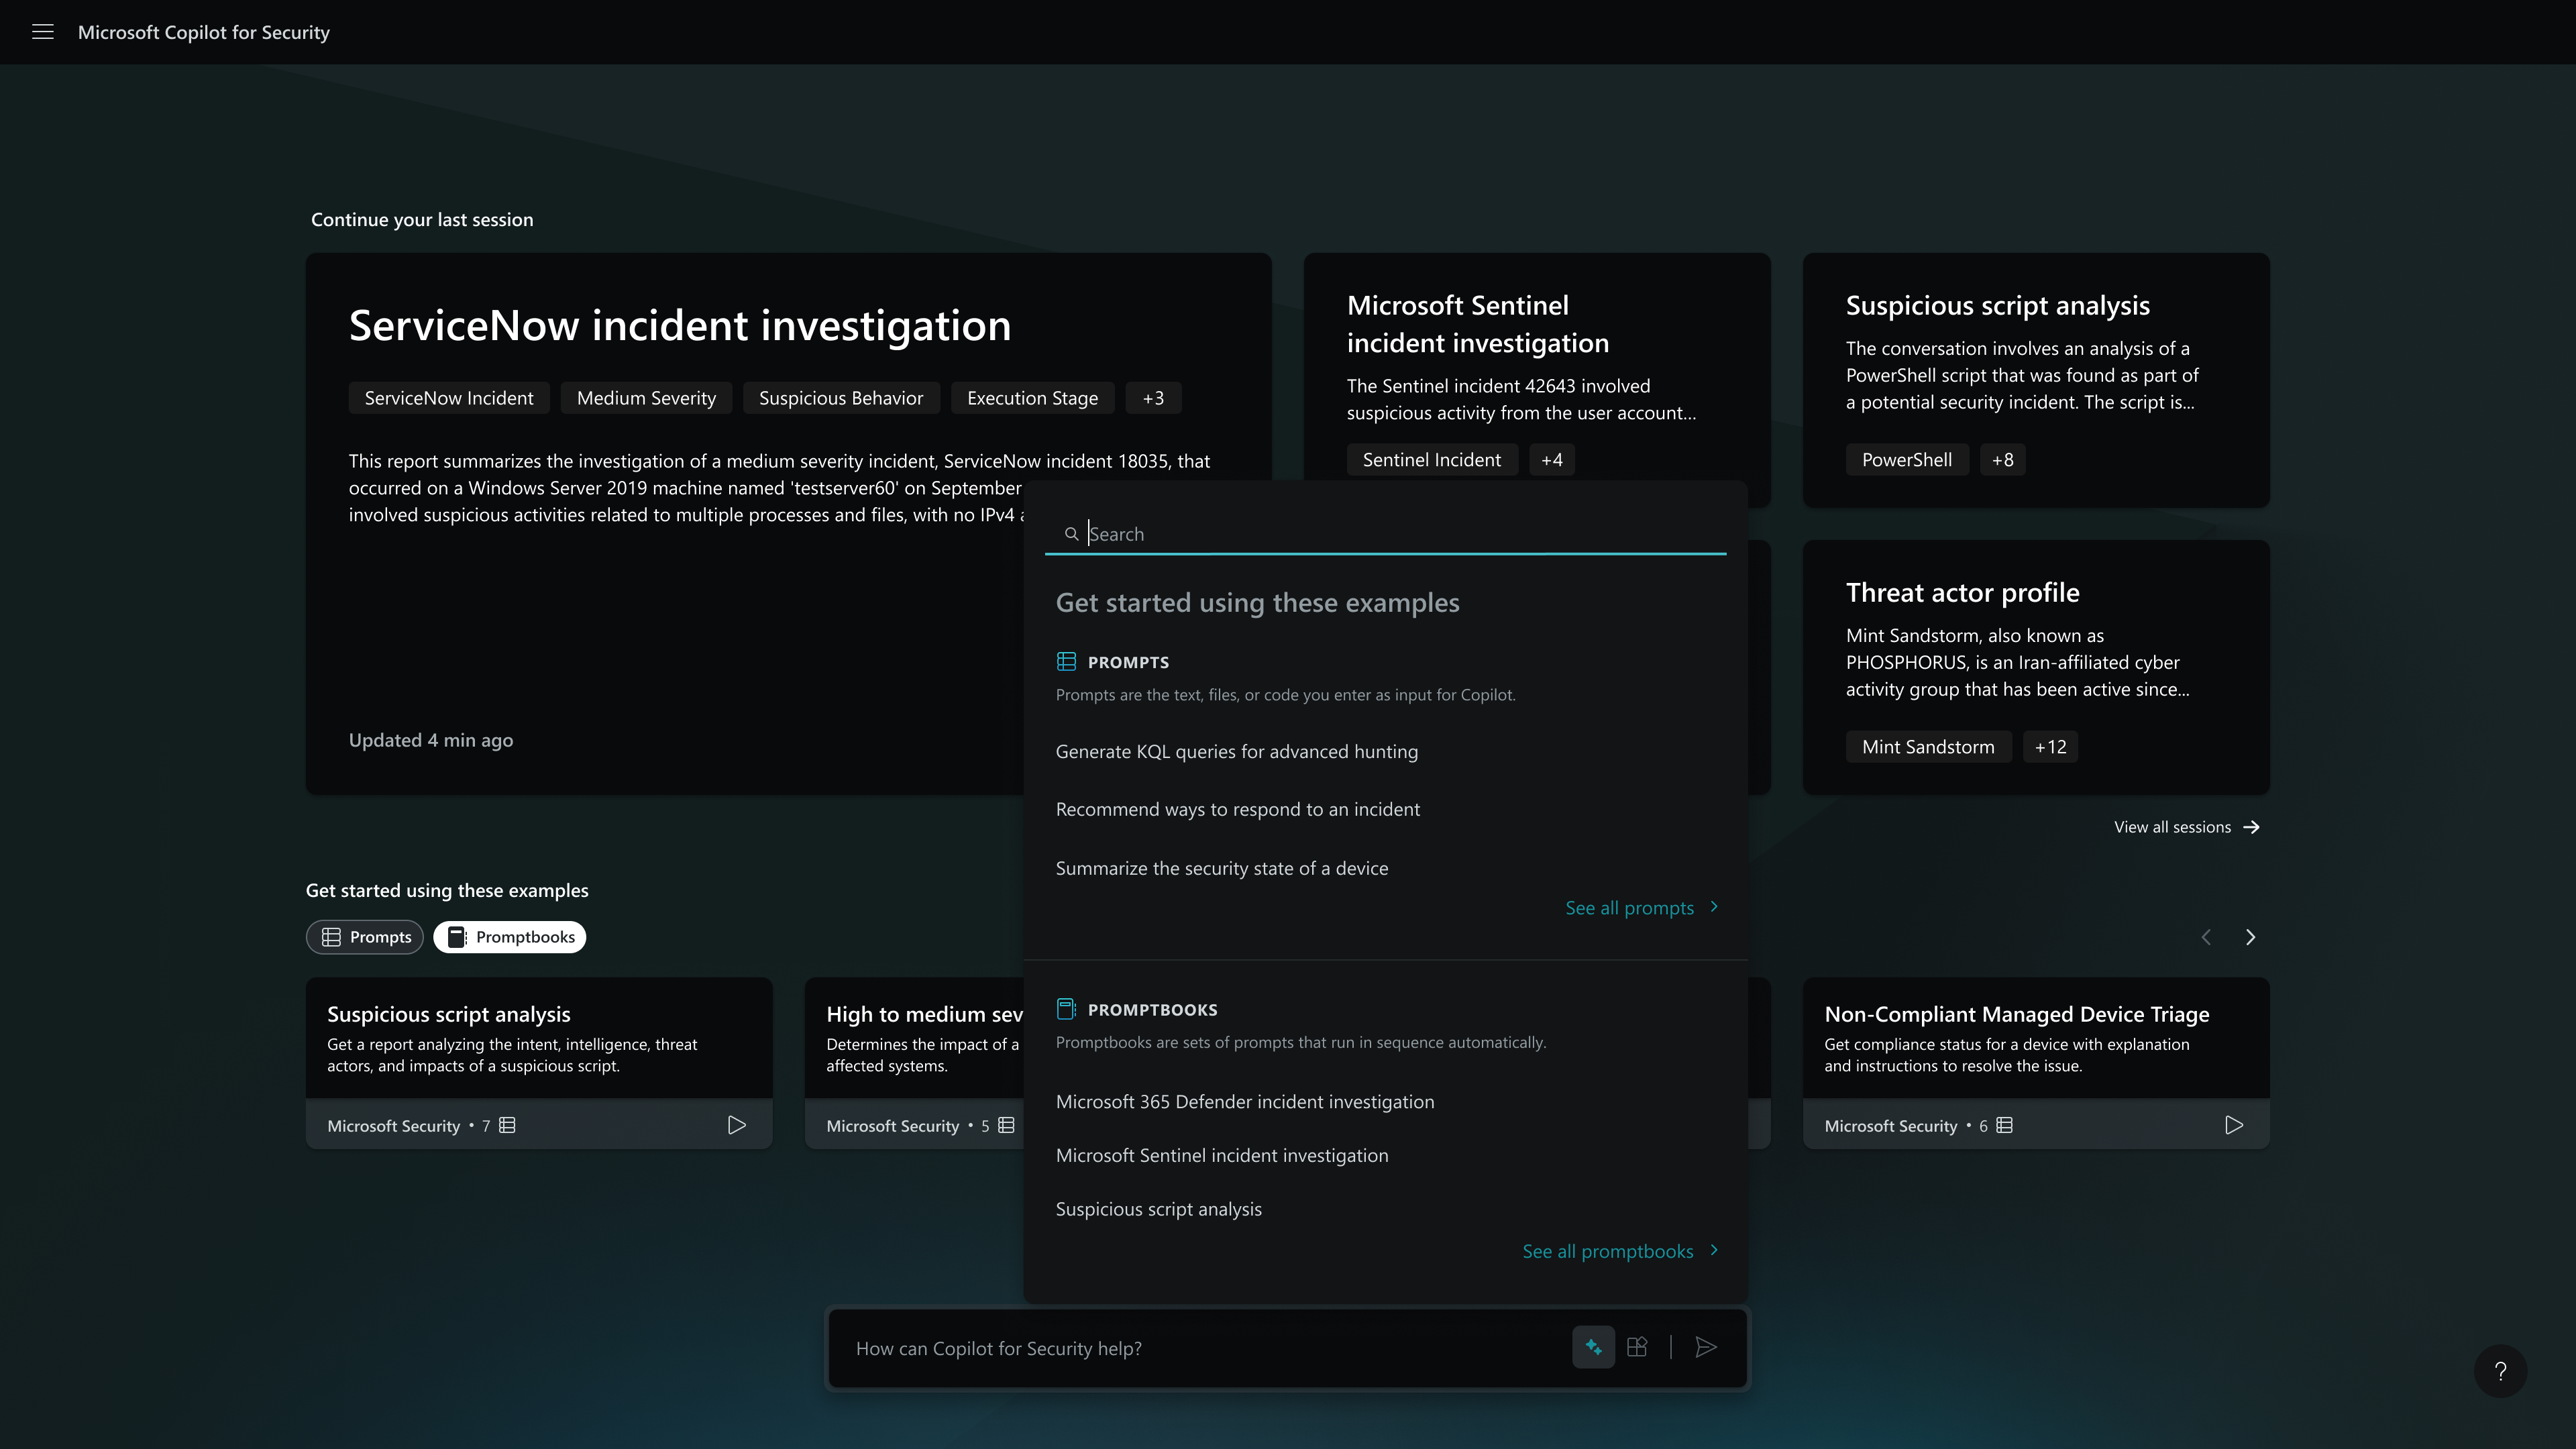
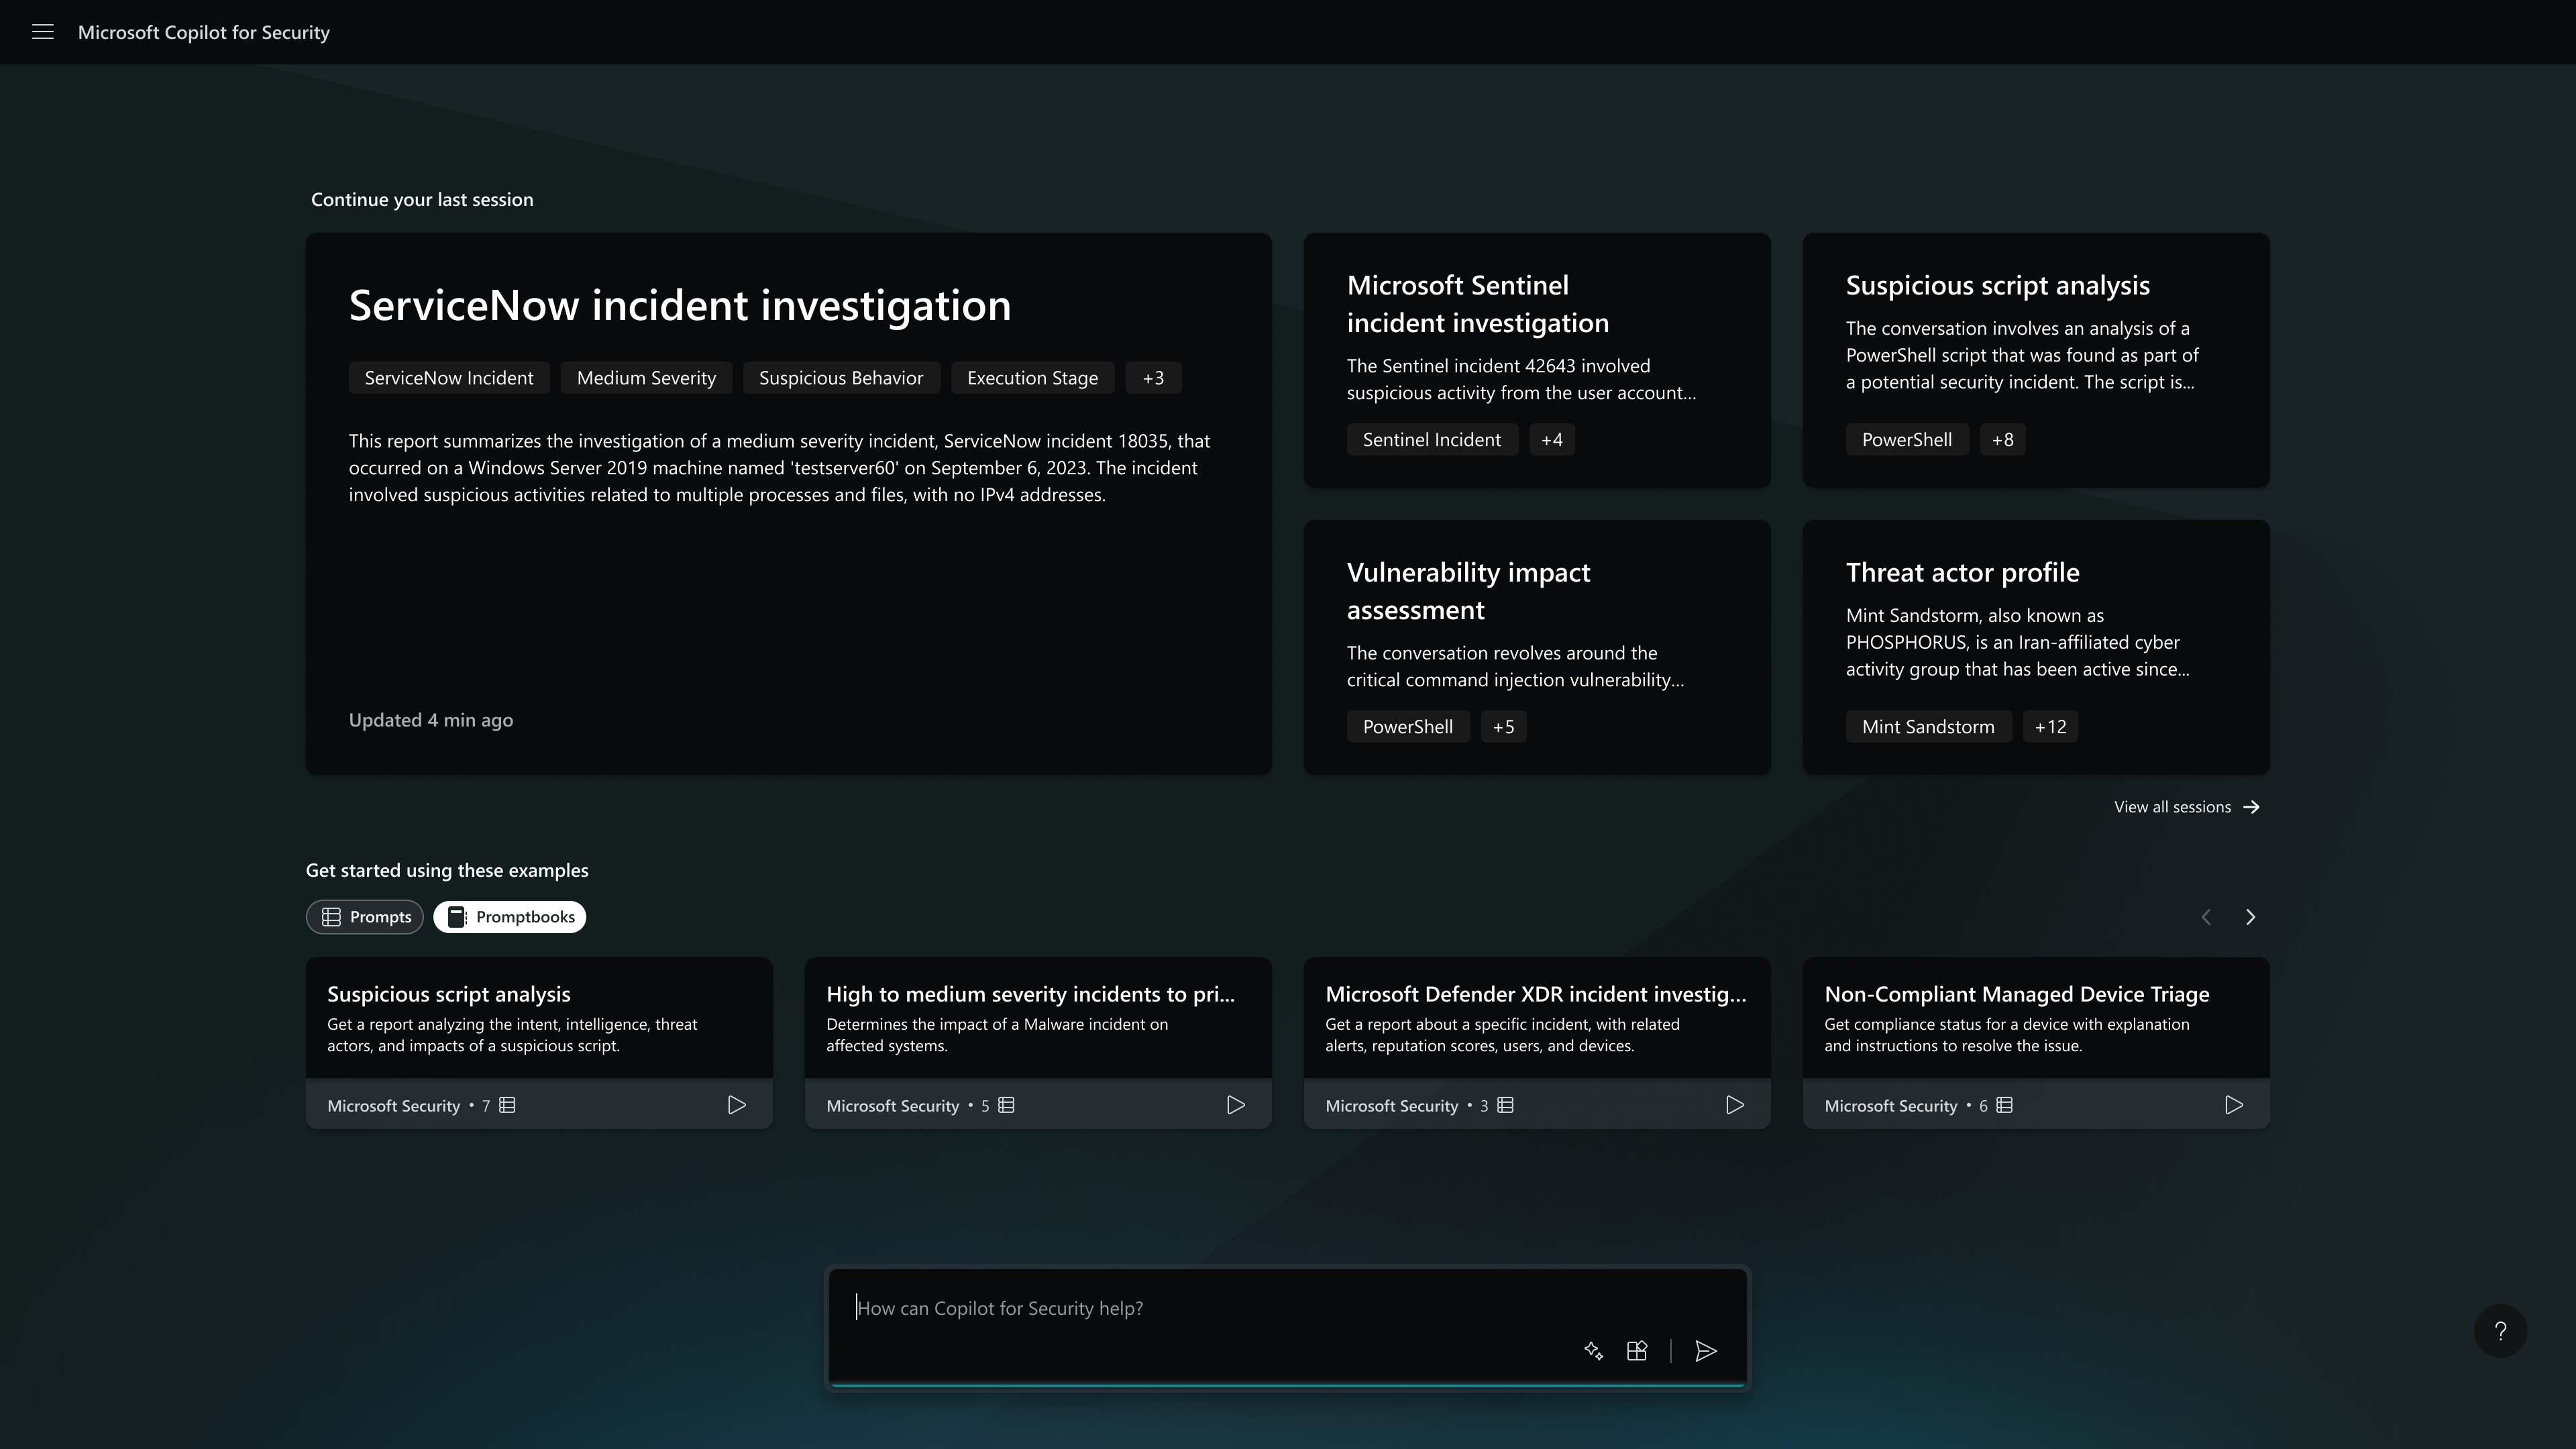
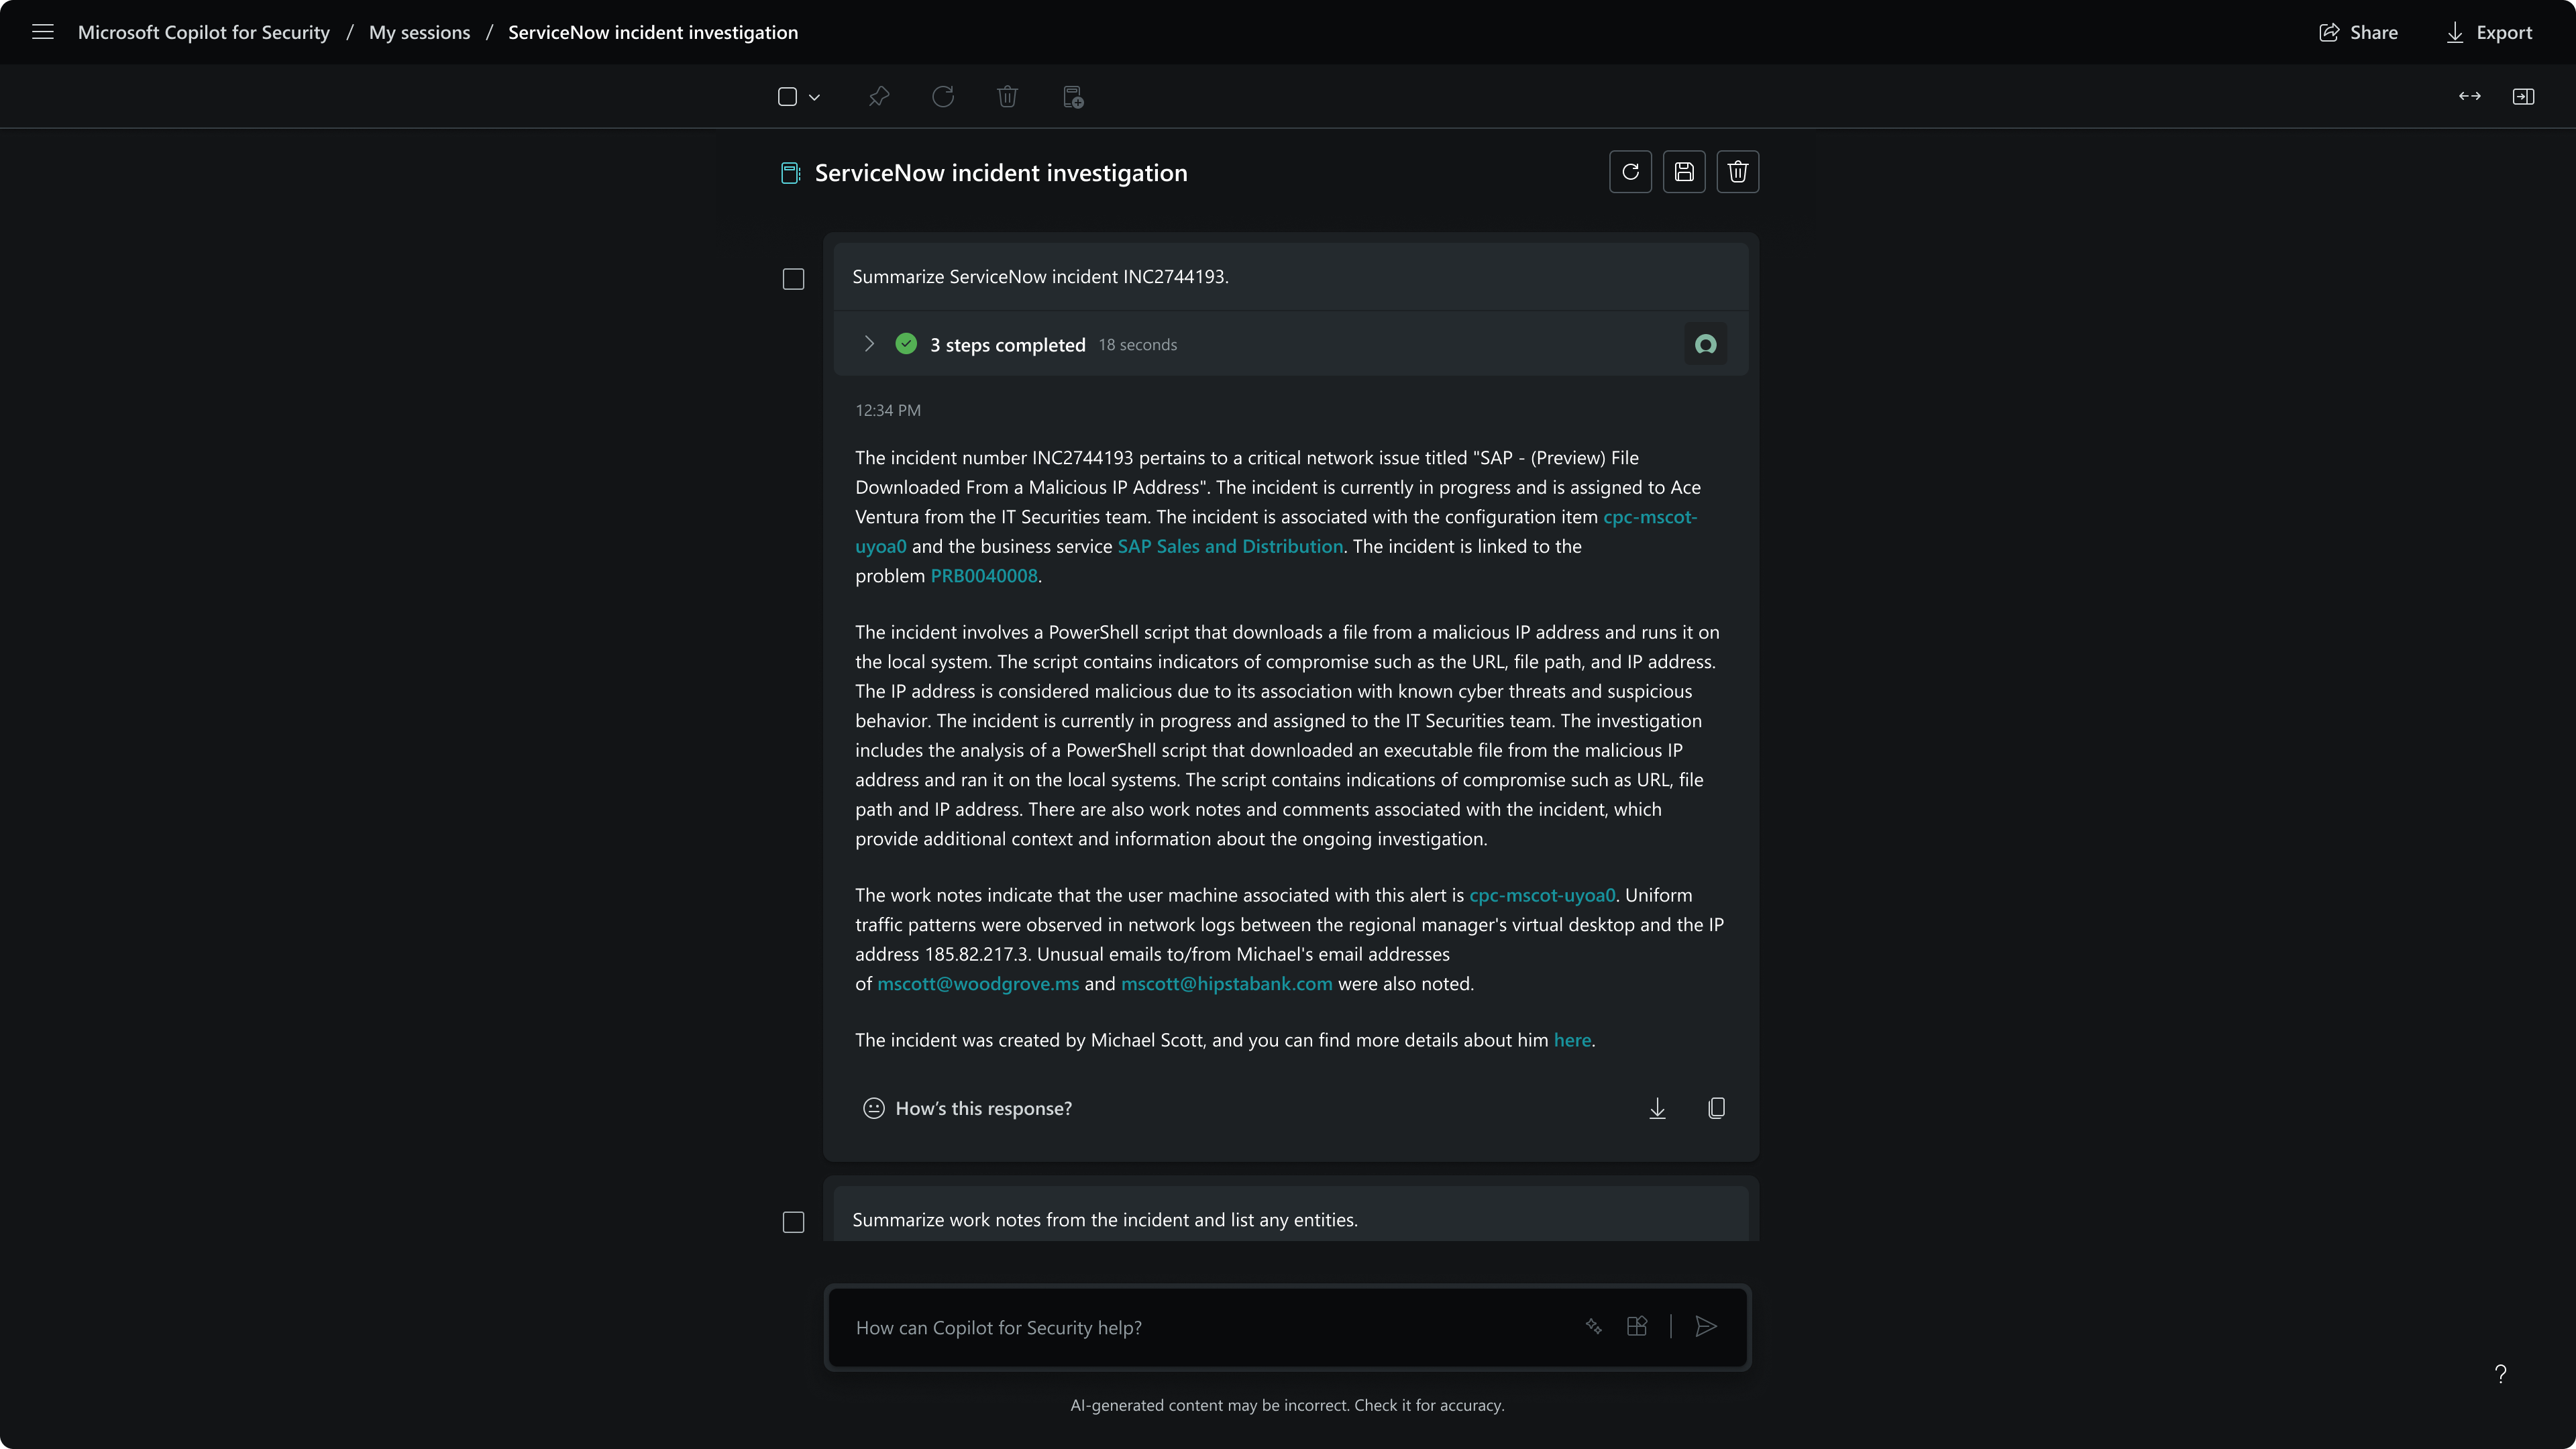
Microsoft Security Copilot helps security and IT teams to protect organizations at the speed and scale of AI. It is available in a standalone experience or embedded into other Microsoft Security products.
N/A
Palo Alto Networks WildFire
Score9.8 out of 10
N/A
Palo Alto Network’s WildFire is a malware prevention service. It specializes in addressing zero-day threats through dynamic and static analysis, machine learning, and advanced sandbox testing environments.
Microsoft Security Copilot is well-suited for environments where security teams face high alert volumes and need rapid triage. It is effective during active threat response, helping us establish timelines and suggest remediation steps quickly. Copilot also excels in executive reporting, generating clear summaries for leadership without much effort. Security Copilot is less effective outside of Microsoft's ecosystem because it doesn't integrate well with other products.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Palo Alto Networks WildFire is highly effective in enterprise environments where detecting zero-day threats and unknown malware is critical. Small businesses may find the cost of advanced subscriptions prohibitive, especially if they only need basic protection. Much of our infrastructure is OT and Palo Alto Networks WildFire is cloud dependent so cannot be used where we have air-gapped systems.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
This is could base and easily manageable for our collocation. While working within the could can review in live time potential treats that it has reported from other devices.
Worked very well with existing Palo Alto devices.
Another huge plus is the simplicity of managing and ease of scalability.
Its cost is competitive with similar/like products available.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
It works very well and takes care of protecting us from threats new and well-known. It's been a game changer in terms of threat detection & prevention.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Anyone can use it. Easy to prompt, also capabilities to become advance with custom agents. It can become custom to your workflow. Many people will have their unique experiences to share and results are generally positive. This is a growth in the product from the effect of community and adoption/usage.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It is a great product that has definitely improved our security posture, however it does require quite a bit of training and time spent customizing for the environment. We had several difficulties in deployment but Palo Alto support was able to help us work through the problems that we were not able to figure out on our own.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
PAN support is very good. You can get the reasonable and timely support on any conditions. When the product is already integrated with the PAN firewalls, you can choose the severity levels based on the effect. The customer service/TAC is very helpful, they even have additional recommendations of advises for product usability. Local partners are also assisting the cases and give their expertise.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
My usage of other products is based on SIEM tools. So far, Microsoft Security Copilot is the only product I've seen that works across multiple technologies/products to provide full visibility into security tooling using AI. I know other vendors are working towards this, but Microsoft has definitely taken a lead.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
WildFire from Palo Alto Networks provides security with very little overhead. With AutoFocus, they’ve got threat intelligence built right in. That way, it can prepare us to react swiftly when a significant danger is identified and dealt with as soon as possible. They introduced firewalls that are aware of applications and can make use of Wildfire. It sped our ability to respond to emerging threats up because of this game-changing development.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Helps reduce time spent creating a baseline script.
Some errors get corrected but then get reintroduced while adding functionality.
I noticed that when using this for PowerShell it will sometimes have you install the module in the script without verifying if it is already installed. You must read the script before executing.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We've had one or two malware files that were blocked by Wildfire. We use it occasionally to check unusual or unexpected files. Hard to monetize ROI, because we don't know what the impact would have been if the file made it through.
We pay significantly for the Wildfire licenses, but given the potential impact to our business, we feel it is worthwhile. Figure costs are somewhere around $1,500 per year per firewall for a mid-range model. Can be higher or lower for different sized firewalls. Onsite appliance was somewhere between $50-100K, which was too much for us, so we use the cloud model.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info