Cisco Secure Endpoint is a comprehensive, cloud-managed endpoint security solution designed to protect devices from advanced malware and cyber threats throughout the entire attack lifecycle—before, during, and after an attack. It offers powerful prevention capabilities to identify and stop threats before they compromise your systems, using multifaceted techniques including risk-based vulnerability management and posture assessments. The solution provides deep visibility and advanced detection…
N/A
Microsoft Defender for Endpoint
Score8.7 out of 10
N/A
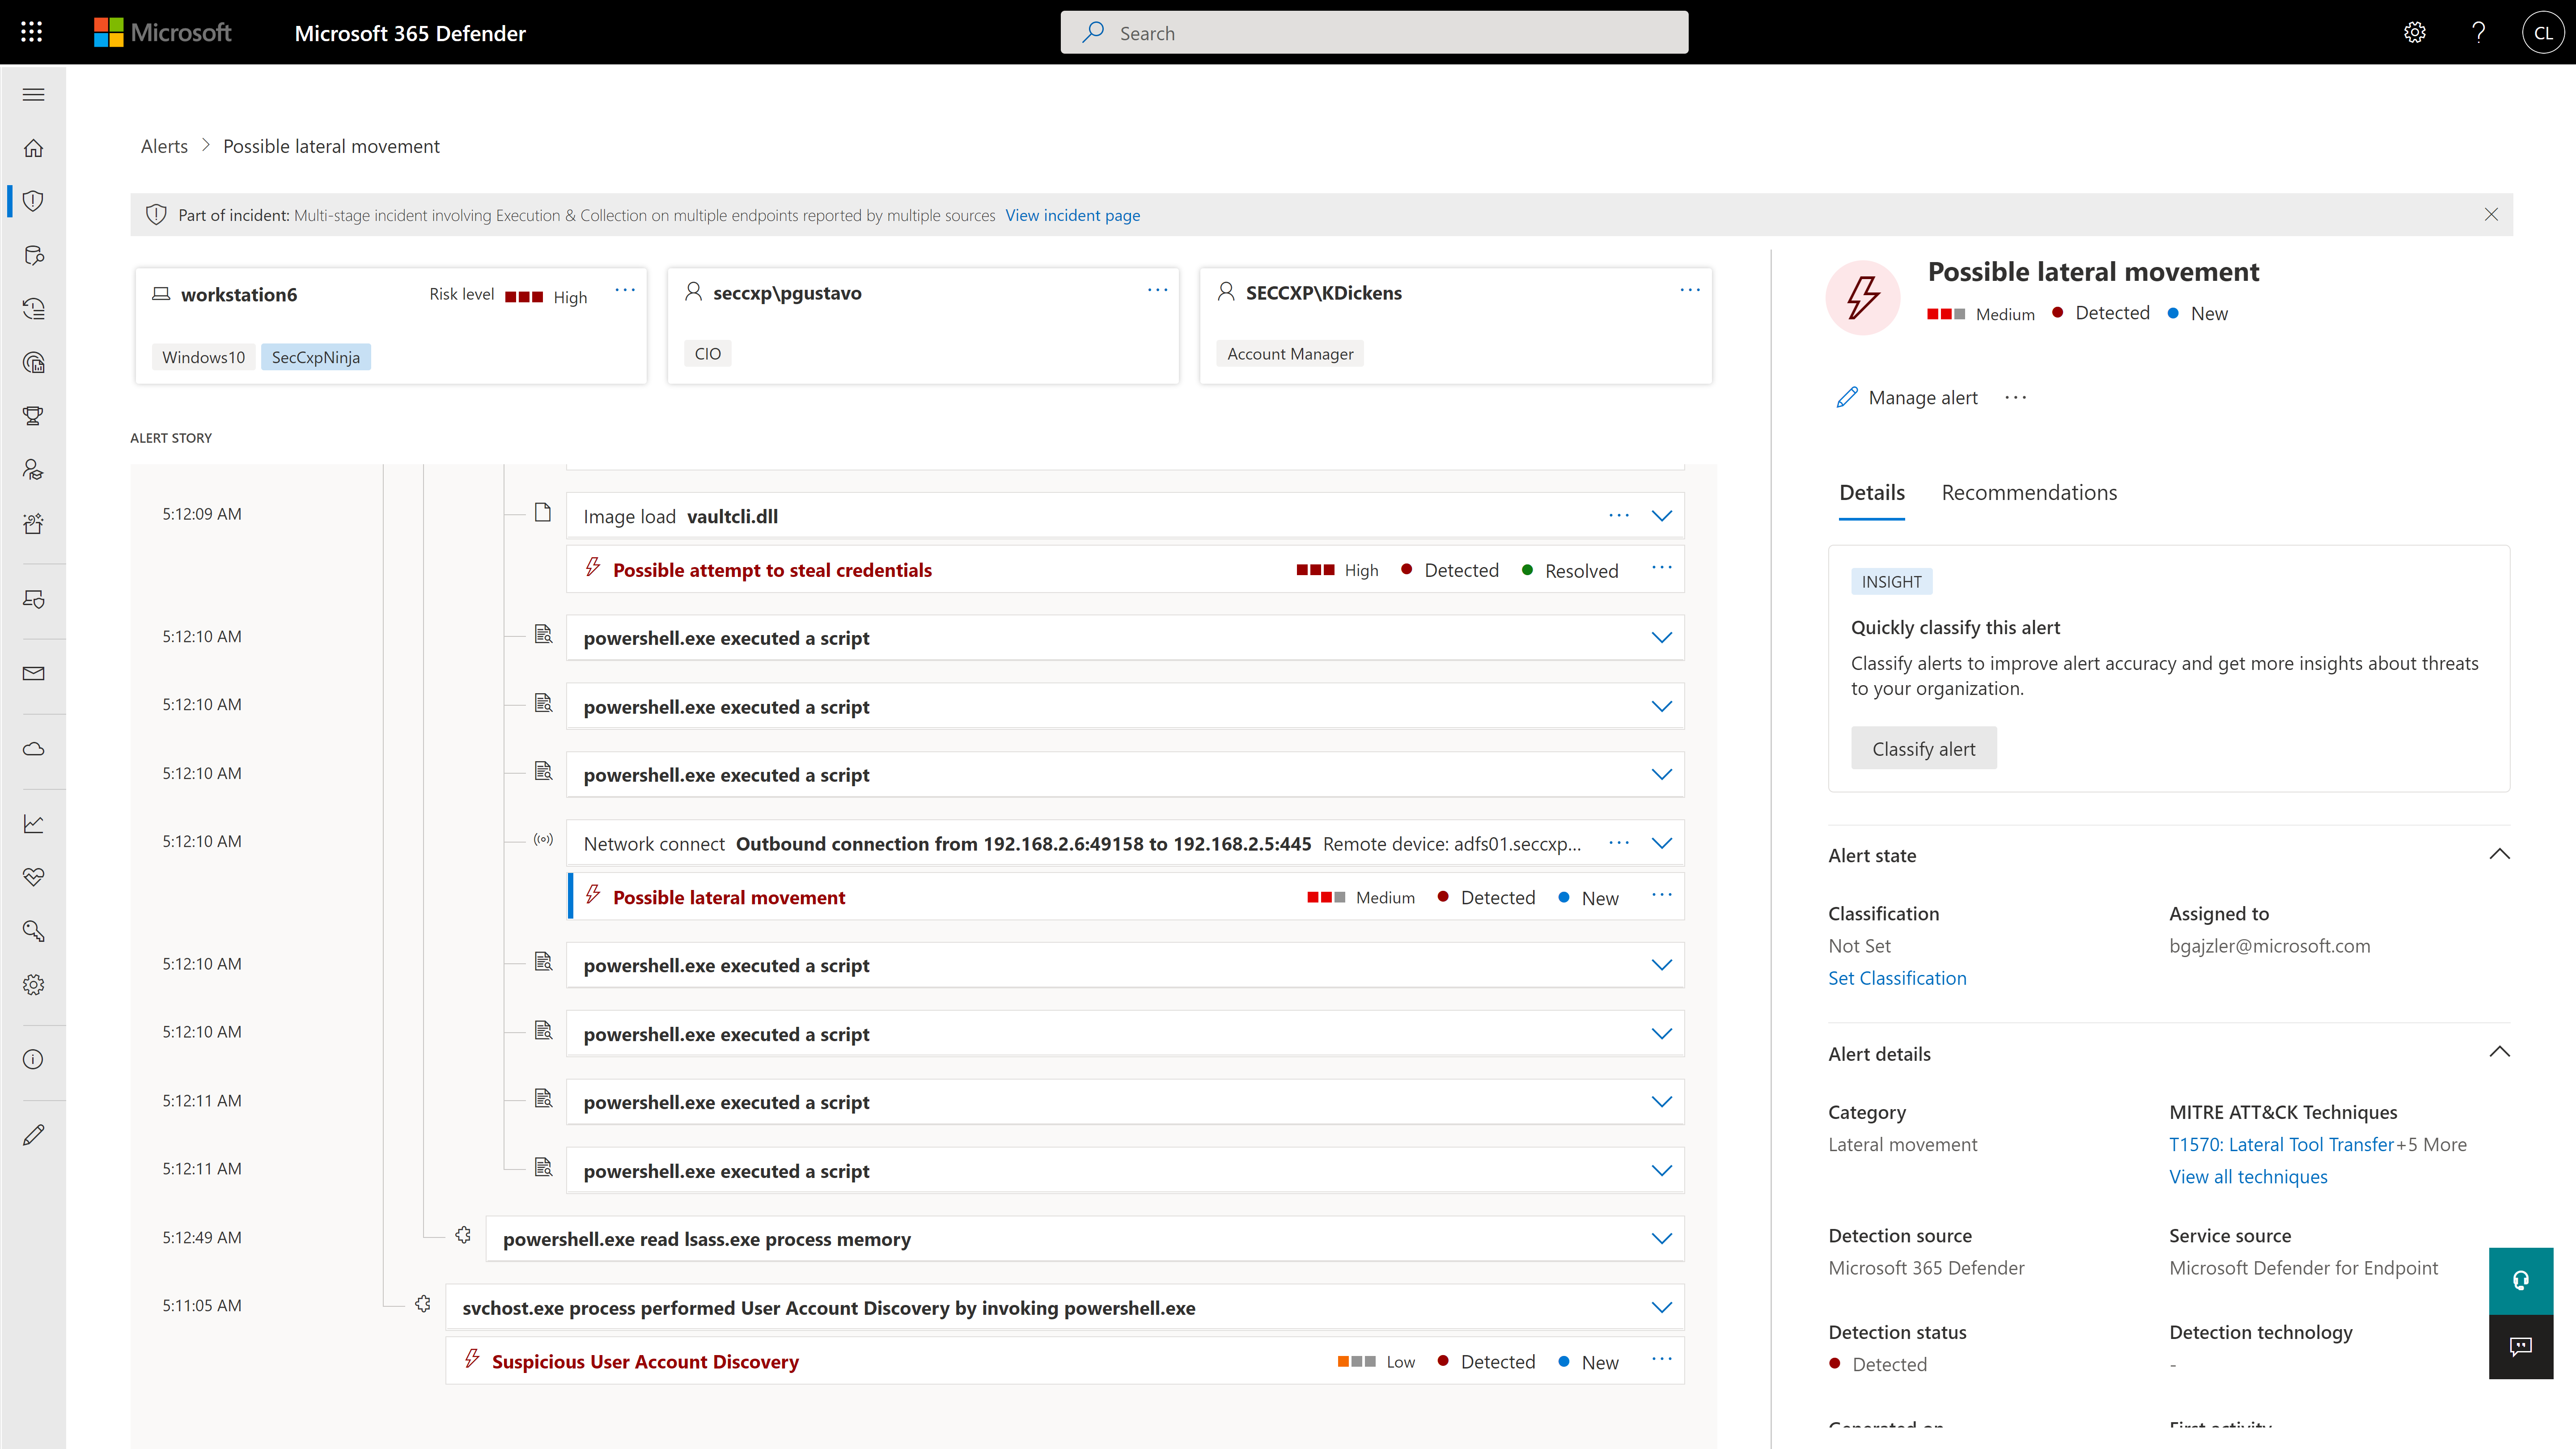
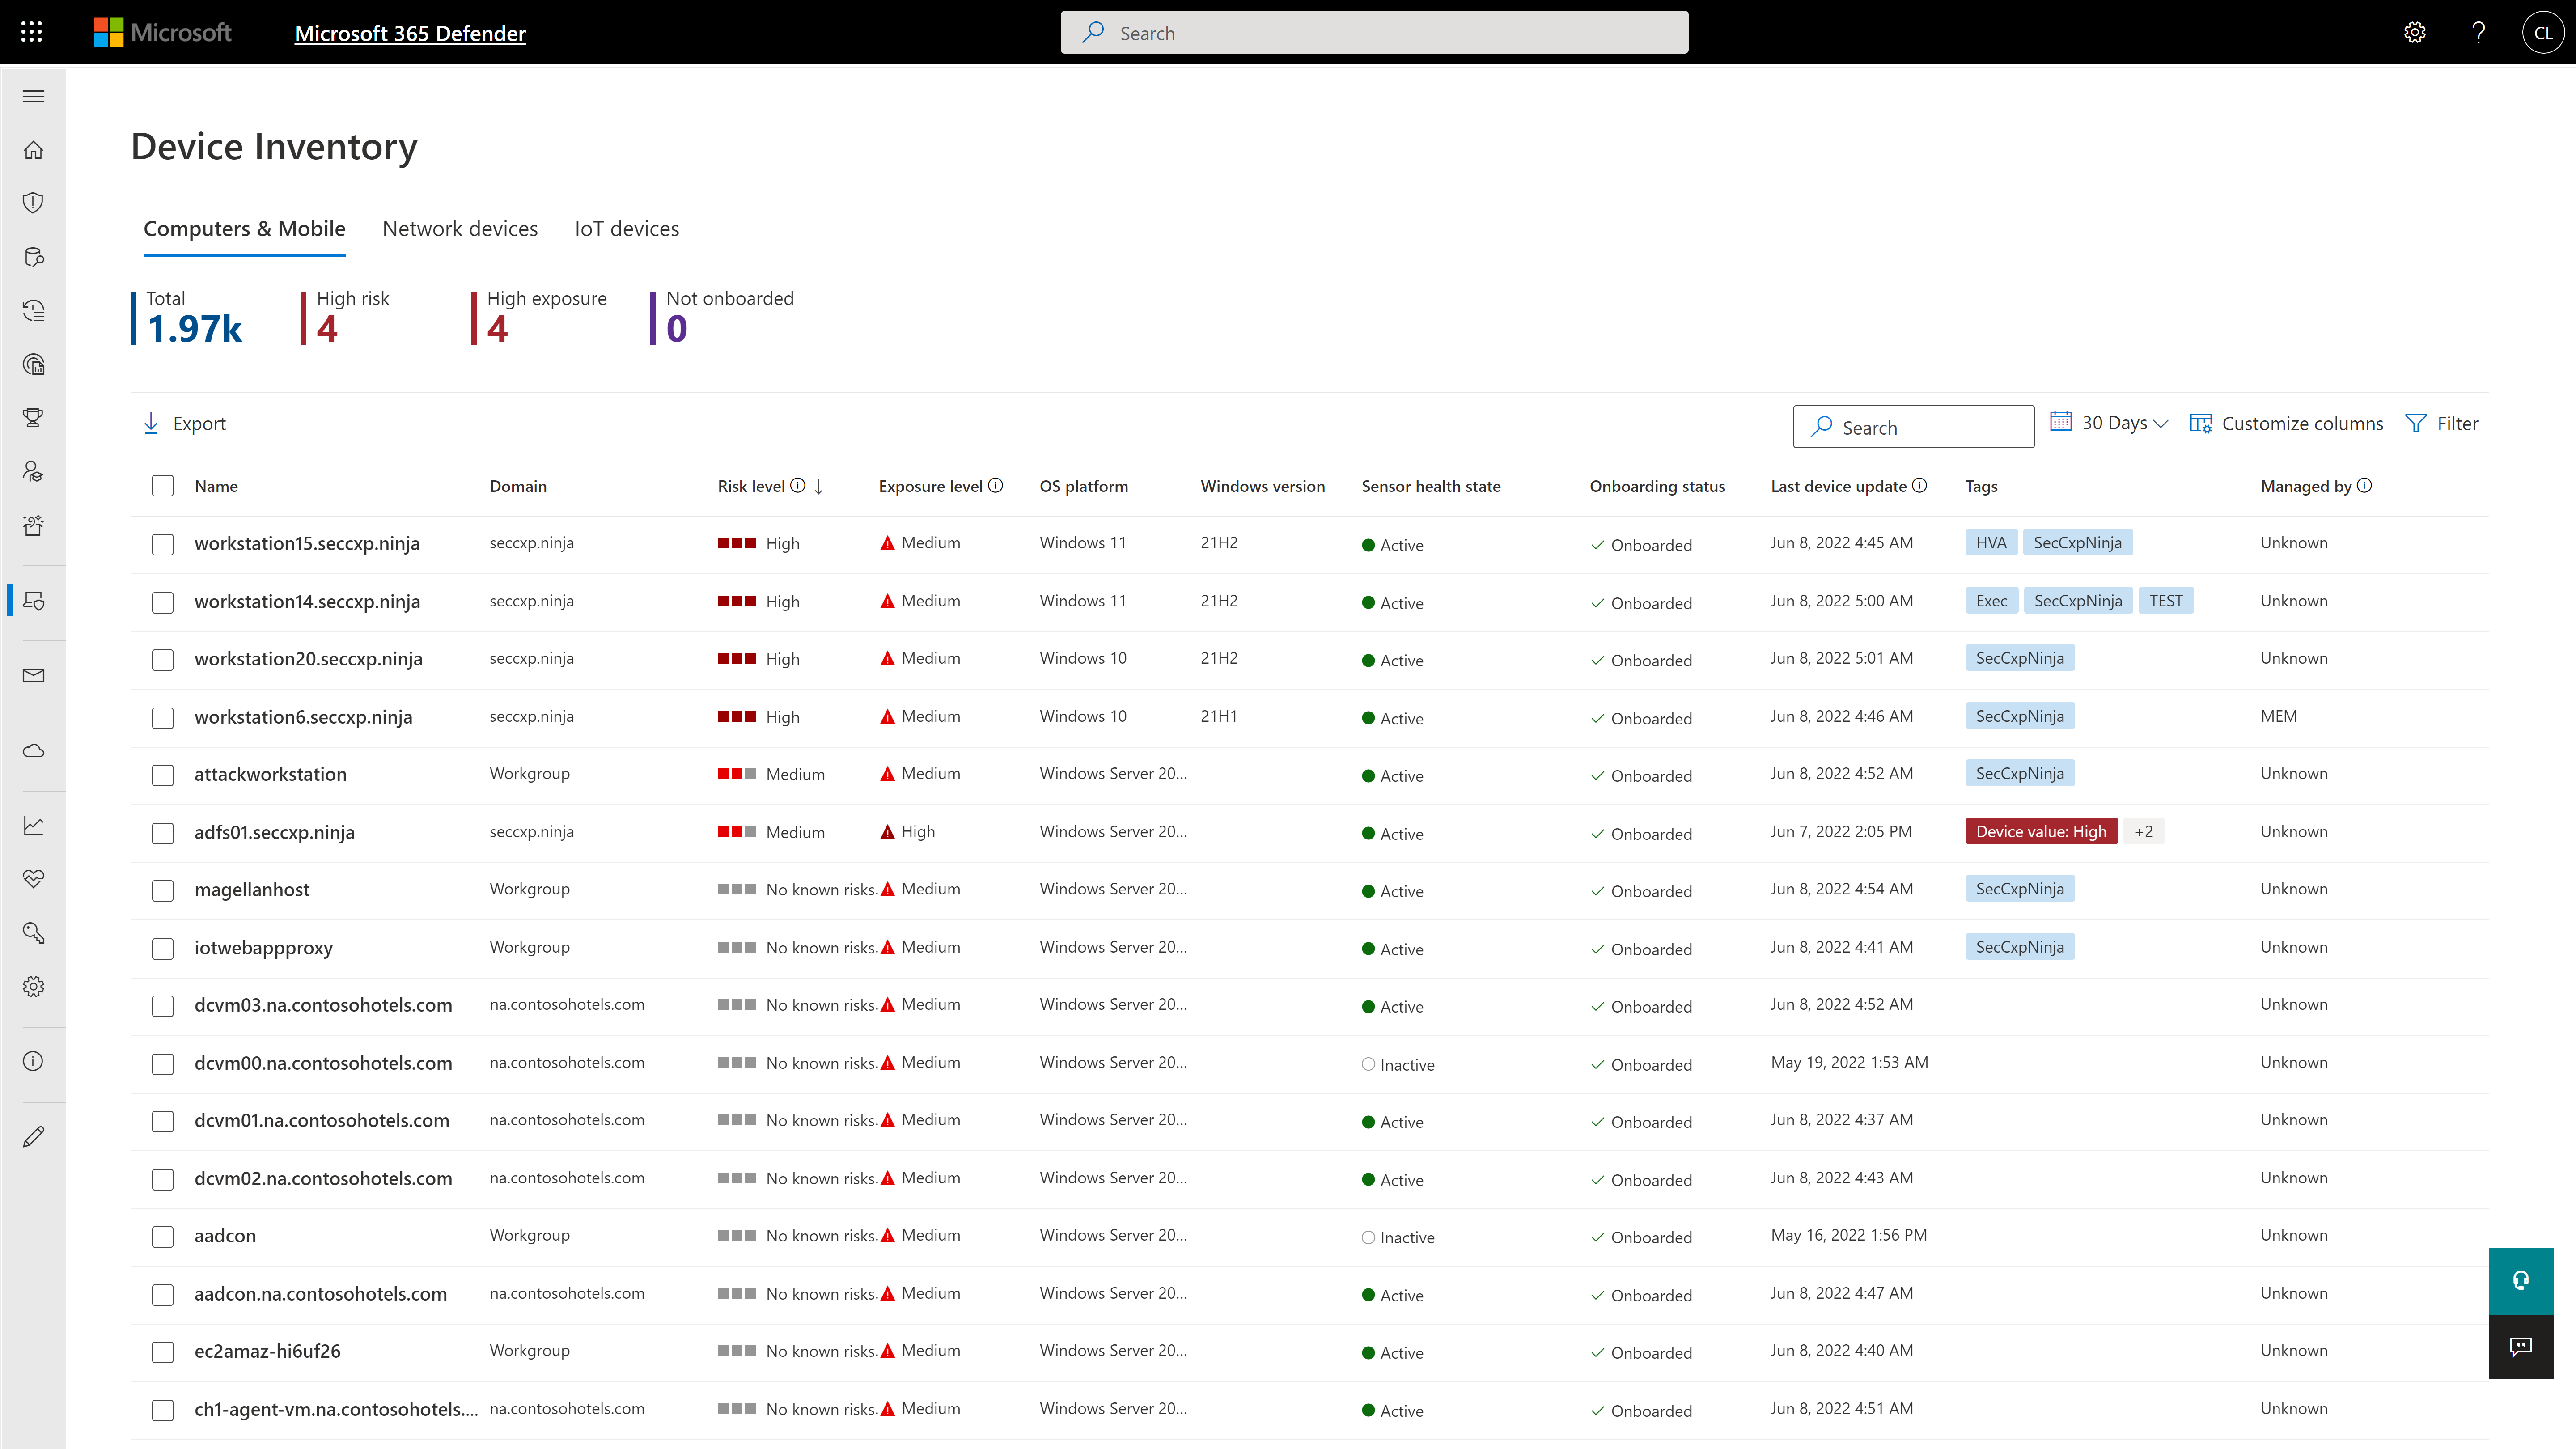
Microsoft Defender for Endpoint (formerly Microsoft Defender ATP) is a holistic, cloud delivered endpoint security solution that includes risk-based vulnerability management and assessment, attack surface reduction, behavioral based and cloud-powered next generation protection, endpoint detection and response (EDR), automatic investigation and remediation, managed hunting services, rich APIs, and unified security management.
$2.50
per user/per month
Pricing
Cisco Secure Endpoint
Microsoft Defender for Endpoint
Editions & Modules
No answers on this topic
Academic
$2.50
per user/per month
Standalone
$5.20
per user/per month
Offerings
Pricing Offerings
Cisco Secure Endpoint
Microsoft Defender for Endpoint
Free Trial
No
Yes
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
—
—
More Pricing Information
Community Pulse
Cisco Secure Endpoint
Microsoft Defender for Endpoint
Considered Both Products
Cisco
Verified User
Chose Cisco Secure Endpoint
Cisco Secure Endpoint provides better overall support and detection compared to other products used. Strong visibility and a strong range of tools when researching an issue to find either information or resolution. Dashboards are also a lot cleaner than most products and easier …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Verified User
Chose Cisco Secure Endpoint
I was not part of the selection process but know this was purchased on a suite of tools. We get so much more from MDE, CSE doesn’t compare.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
IT Security Manager in Information Technology at RS&H Inc. (Design, 1001-5000 employees)
Chose Cisco Secure Endpoint
Cisco Secure Endpoint is an advanced EDR solution that is highly effective and scalable. Our experience previously with MalwareBytes and Microsoft Defender was not horrible, but these products were not as effective and did not integrate well with our other security products to …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Microsoft
Verified User
Chose Microsoft Defender for Endpoint
CrowdStrike Falcon, and Sentinel One are other big ones that we use a bit. Cisco Secure Endpoint we've evaluated as well. Cisco Secure Endpoint capability-wise doesn't match up to Defender, SentinelOne, and CrowdStrike both do, but the cost profiles are a bit higher. So most of …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint has the best integration for us in our (mostly) Windows environment. Also we are using M365 E3 so this already included Microsoft Defender for Endpoint P1. The extra cost for Defender for Endpoint P2 is definitely worth it. You need to see these …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Verified User
Chose Microsoft Defender for Endpoint
Microsoft Defender for Endpoint offers strong integration with Microsoft 365 and Azure services, which provide a unified security experience. While McAfee Trellix is known for solid antivirus, Microsoft Defender excels in integration in the ecosystem.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cisco Secure Endpoint is well suited for keeping track of the many different and points that we have in our organization. All of these devices can easily be monitored with Cisco Secure Endpoint. It can monitor our servers and our desktops and laptops in our environment. It isn’t as appropriate for our student devices. However, those aren’t as critical since they are just Chromebooks.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Because of its integration with Windows, it is very easy to deploy and manage. Any IT department should be able to leverage the software and interface. The admin portal provides weighted recommendations that comprise the Secure Store, offering admins, security teams, and business owners valuable insights into their security footprint without requiring a strong security background. The software would be ideal for small and mid-sized businesses that cannot dedicate resources to security. Larger enterprises would also benefit, but may require the enhanced license.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Once we, I guess one turned out that path because we have a small IT team, one of the big factors that came into play is how easy it was to deploy and the kind of security it provides for your endpoint devices. For us, it's got all those AI capabilities that really help. So traditionally when there was an incident on Alert on an antivirus program, you'd have a couple of guys run across the office to try to pull a plug. One of the awesome features with Secure Endpoint is its isolation mode that clamps down endpoint devices and then just isolate it. It's connected to, I think Cisco's tell us the threat intel environment. So they've got up-to-date metrics and fixes on threats out in the wild. And once they detect that, they apply it across your whole brand. So yeah, really effective for us.
One of the things that really stands out is the retrospective detections. So say something's detected two weeks later of a product that you had on your system. Initially it scanned it past, but then they discover vulnerability. The product has the ability to come back and retrospectively apply restrictions on specific applications you have on your environment. So I think that's one key winner.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
One, it's crazy lightweight, so compared to some of the competitors that we also have used with our security services, it's really lightweight and so I don't have a lot of overhead on the system that it's running on.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The interface has many views that all look the same, except that functionalities are different. This makes it incredibly difficult to find the action you want to take.
Built-in exclusion sets are missing a number of notable Anti-Malware products and must be manually implemented.
High learning curve due to complexity of the solution and the range of features it contains. Provided documentation is hidden in a small icon at the top of the page which is often off-screen when needed.
Color choices lead to panic situations during deployment. 1 questionable file could lead to the main display showing a large, bright red alert which makes customers think their whole environment is compromised.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
So the fact that Defender for Endpoint still works with signatures is actually, I don't know, a little difficult for us because, I mean, since Microsoft trusts those signatures, you can easily inject code. And we've done it many times. To show that you can inject code through vulnerabilities like CV 2013, 99, and 33 but still keep the signature. So because of the trust of those signatures, the malware just kind of slides into the environment without Defender knowing. That's the first part. The second part is that the behavioral analysis is not precisely its Prime. It's not Defender's best capability for endpoints. So, Defender does not identify all behaviors considered by other EDRs in the market.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cost add-ons for Security features is nickel and diming the process to keep pace with cybercrime. Limited Education budgets require us to be more pro-active in finding cost-effective measures to protect our devices, staff and students. Defender is a strong, well-featured product that is pricing itself out of the education market
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
AMP is very difficult to use compared to other products we've seen. It's hard to understand why there are so many different logins for the various products that supposedly integrate with AMP. We had weekly phone calls for months to implement the product yet none of the IT department really enjoys using this product or feels comfortable with the accuracy of detections. The number of false positives is high.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
It offers multiple security features and integrates well with Microsoft ecosystems. A workflow for threat detection, investigation, automated remediation, and a centralized dashboard is an added advantage. This application is mainly designed for experienced users; new users may feel challenged.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Microsoft Defender for Endpoint chugs along just fine no matter what we throw at it and what systems it's running on. It doesn't take up a lot of resources either, so that's welcomed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
In terms of technical support for Cisco Secure Endpoint, the support has been pretty good. All the cases I submitted were solved in a reasonable time frame, and it was a good experience. However, I find that not as many vendors have the expertise I would expect.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The first time I tried to onboard my macOS endpoints to MDE I struggled for quite a bit. I had to reach out to Microsoft's MDE support team. The tech was very helpful in walking me through the steps during a screen share session
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Deployment was handled by our team here and everything went pretty smoothly. We did have a few hiccups in our test group, but that only took a bit to get ironed out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cisco Secure Endpoint is an advanced EDR solution that is highly effective and scalable. Our experience previously with MalwareBytes and Microsoft Defender was not horrible, but these products were not as effective and did not integrate well with our other security products to allow us to monitor and react quickly to address threats that were within our network. Key to any security effort is mitigation and the ability to quickly identify and respond so any damage can be avoided or limited.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Cylance's policy is to block everything and requires an active person to monitor and unblock legitimate processes. As updates and software continue to evolve, it is a full-time job to be a Cylance administrator. Microsoft Defender for Endpoint is a set-and-forget solution that catches threats when they occur and leaves you to focus on your work unimpeded.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info