TrustRadius: an HG Insights company

Symantec Email Threat Detection and Response vs. LogicHub MDR+

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    Symantec Email Threat Detection and Response

    Score8.8 out of 10
    N/ASymantec email threat detection and response, from Broadcom, is a software solution designed to protect against the most sophisticated email threats and gain comprehensive insights into targeted & advanced email attacks.N/A

    LogicHub MDR+

    N/AN/AMDR+ offers automation-driven Managed Detection and Response. The solution integrates with the user's security stack to deliver expert threat detection and automated incident response, with optional one-click authorization, mapped to the MITRE ATT&CK framework. The MDR Services include the vendor's SOAR+ platform with case management (and optional Elk-based SIEM), and integrateswith the user's existing tools. Users can see all the threats the LogicHub expert SOC…N/A
    Pricing
    Symantec Email Threat Detection and ResponseLogicHub MDR+
    Editions & Modules
    No answers on this topic
    No answers on this topic
    Offerings
    Pricing Offerings
    Symantec Email Threat Detection and ResponseLogicHub MDR+
    Free Trial
    NoNo
    Free/Freemium Version
    NoNo
    Premium Consulting/Integration Services
    NoNo
    Entry-level Setup FeeNo setup feeNo setup fee
    Additional Details——
    More Pricing Information
    Best Alternatives
    Symantec Email Threat Detection and ResponseLogicHub MDR+
    Small Businesses
    No answers on this topic
    No answers on this topic
    Medium-sized Companies
    Proofpoint Targeted Attack Protection (TAP)
    Score9.1 out of 10
    No answers on this topic
    Enterprises
    Proofpoint Targeted Attack Protection (TAP)
    Score9.1 out of 10
    No answers on this topic
    All AlternativesView all alternativesView all alternatives
    User Ratings
    Symantec Email Threat Detection and ResponseLogicHub MDR+
    Likelihood to Recommend
    8.8
    (3 ratings)
    -
    (0 ratings)
    Usability
    9.0
    (1 ratings)
    -
    (0 ratings)
    User Testimonials
    Symantec Email Threat Detection and ResponseLogicHub MDR+
    Likelihood to Recommend
    Broadcom
    I have had a suitation where the company domain was being blasted by tons of spam emails and the Symantec Email Threat Detection stood to the test and block all these harmful email from entering our users mailbox, for a less appropriate scenario would be the frequency of the false positives that are reported that I have to train the tool how to allow these traffic to pass.
    Incentivized
    Read full review
    LogicHub
    No answers on this topic
    Pros
    Broadcom
    • Scans computers for viruses
    • Notifies admins of infections
    • Good licensing process
    Incentivized
    Read full review
    LogicHub
    No answers on this topic
    Cons
    Broadcom
    • Adding malicious sources taking time
    • Reporting function is very basic
    • Symantec ATP has no integration with Symantec ETDAD.
    Incentivized
    Read full review
    LogicHub
    No answers on this topic
    Usability
    Broadcom
    Symantec Email Threat Detection and Response is a treadsetter, it has great features and works well overall
    Incentivized
    Read full review
    LogicHub
    No answers on this topic
    Alternatives Considered
    Broadcom
    We are making a migration from Symantec to SentinelOne in the near future for easier deployment, better EDR and management functionality.
    Incentivized
    Read full review
    LogicHub
    No answers on this topic
    Return on Investment
    Broadcom
    • Integration with ETDAD will make Symantec ATP more powerful for future AD threats
    • Implemeting Symantec ATP was easy and took little time
    Incentivized
    Read full review
    LogicHub
    No answers on this topic
    ScreenShots

    LogicHub MDR+ Screenshots

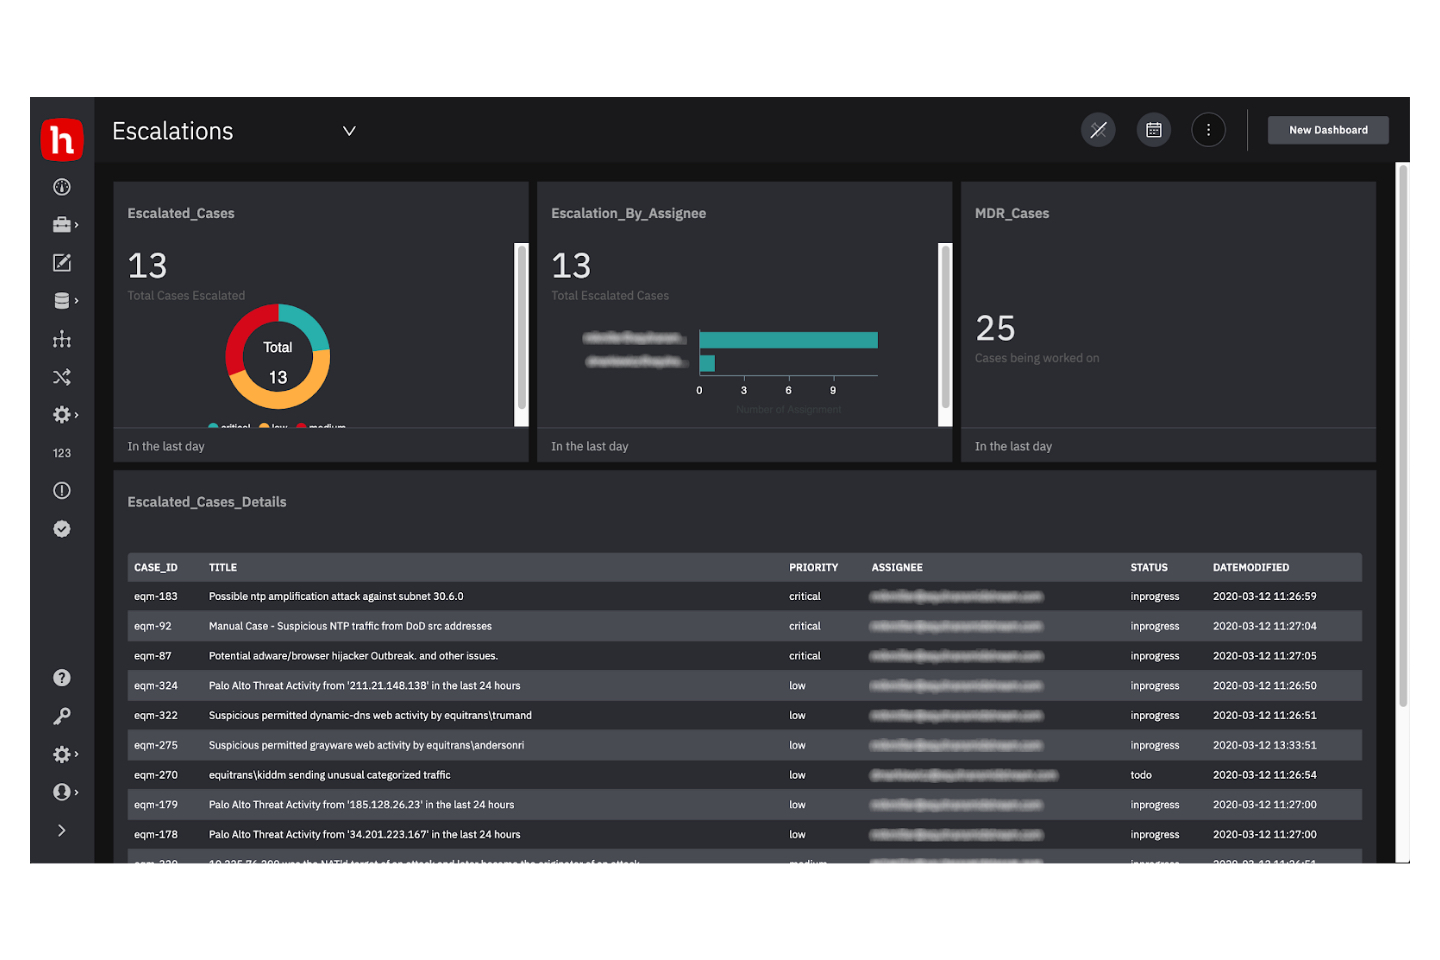
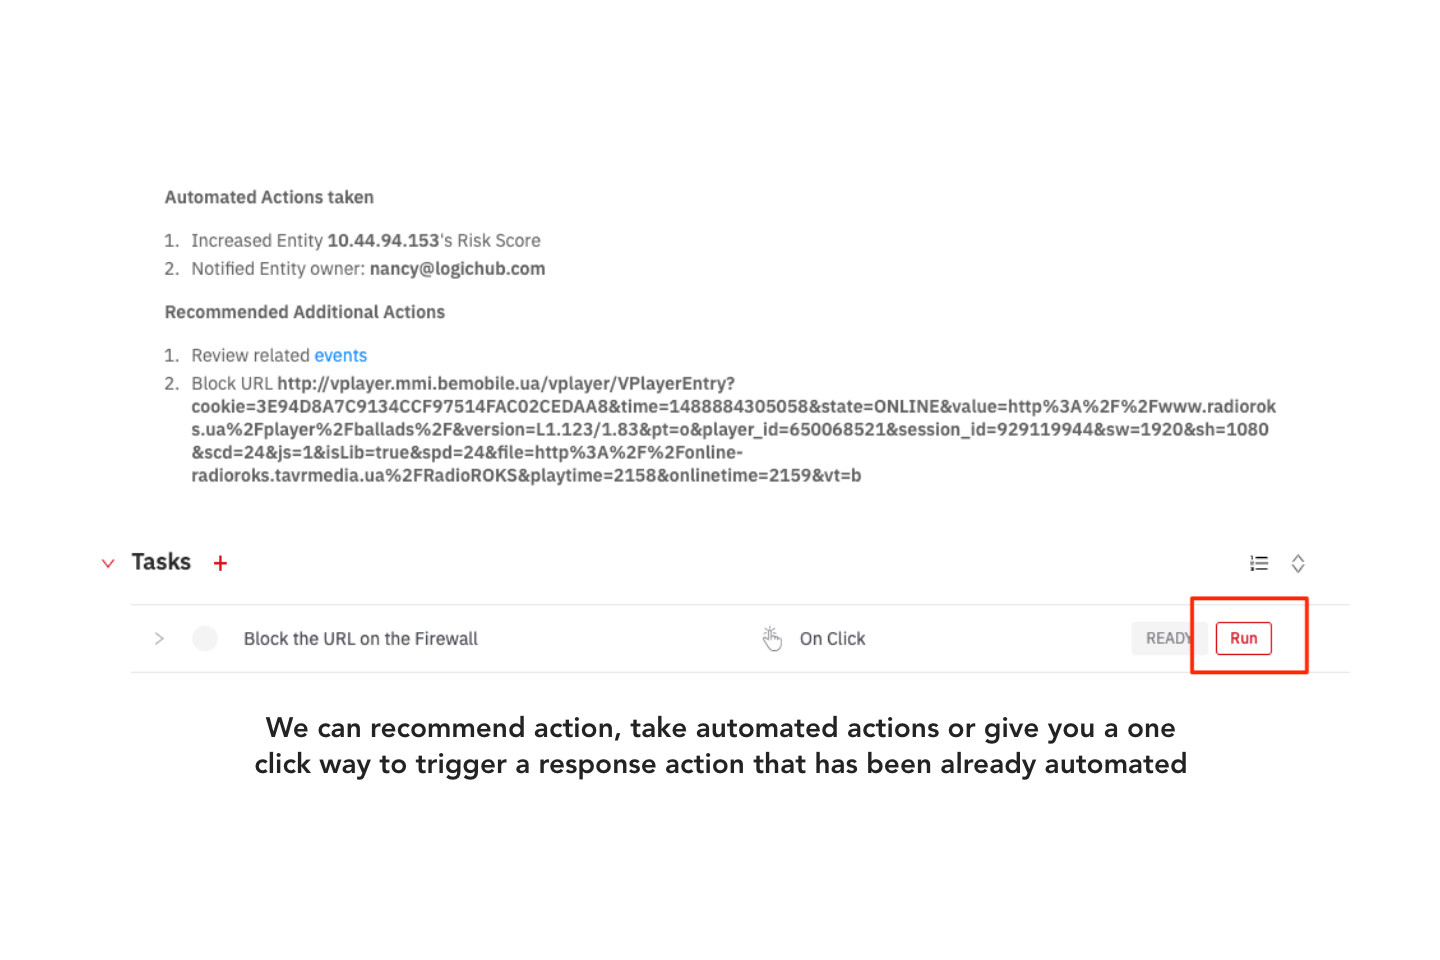
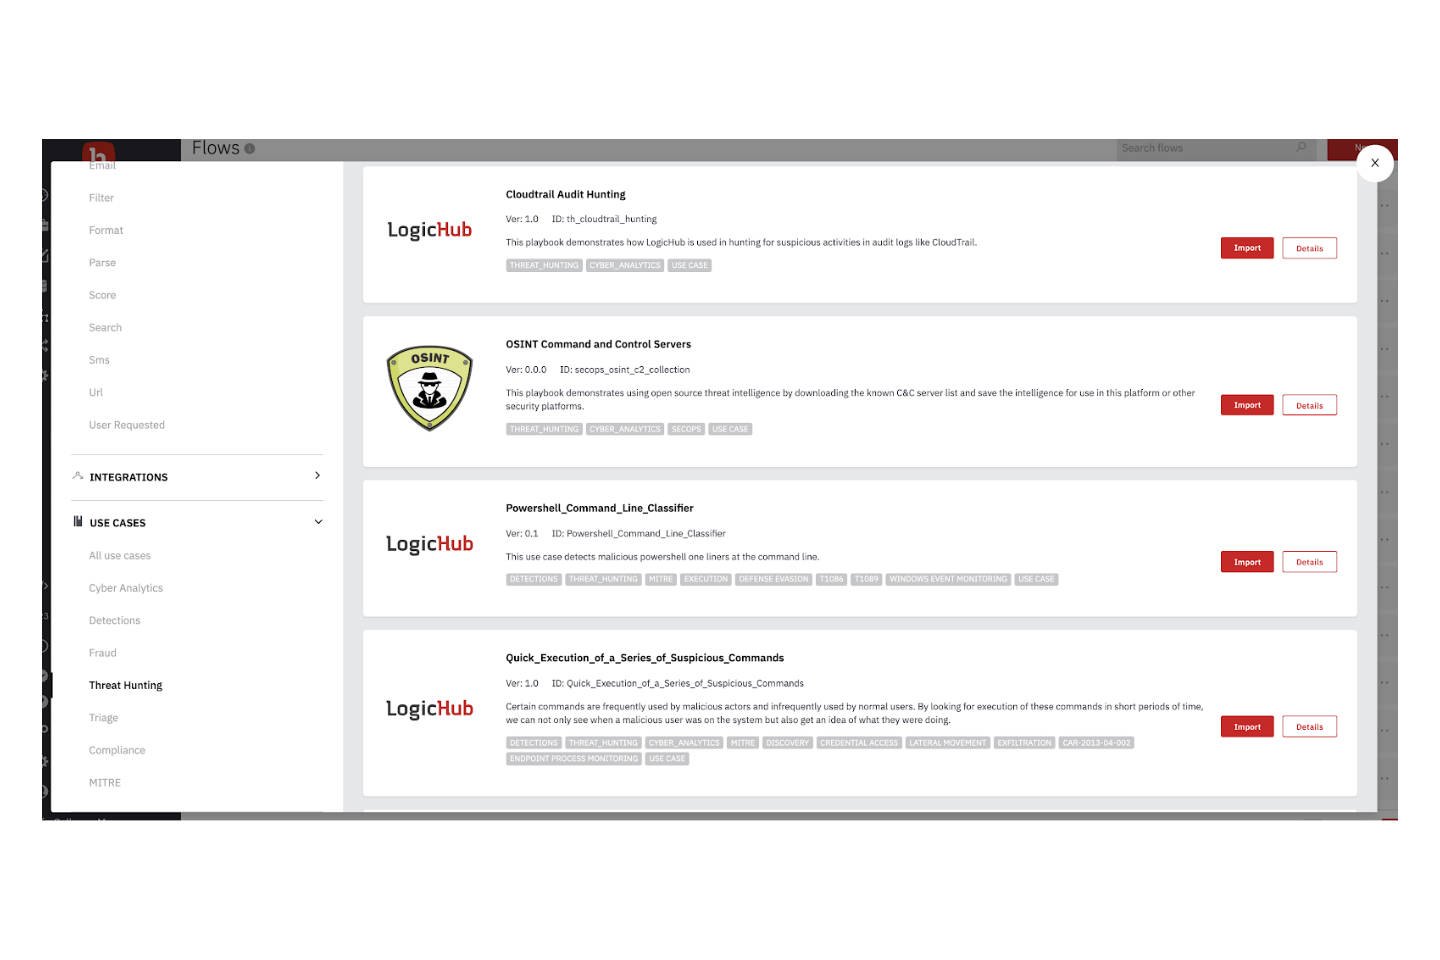
    Screenshot of End-to-end visibility - Executive level dashboards, detailed cases and detection and response playbooks deliver complete visibility into your security posture at all times.Screenshot of Fully integrated case management - Customizable case management delivers detailed confirmed threat data, fully investigated by experts and automatically enriched by the platform.Screenshot of Automation driven incident response - Delivers the flexibility to respond in the way that works best for you with options for one-click authorization or fully automated actions.Screenshot of Extensive Integrations - Adapts to fit your existing security stack and operating requirements, no matter what you have in place,Screenshot of Customizable playbooks - Lets you customize any out-of-the-box playbook or create your own for alert triage, case enrichment, and incident response.Screenshot of Threat hunting automation -Performs 24x7, continuous deep threat detection mapped to the MITRE ATT&CK framework.