TrustRadius: an HG Insights company

Mandiant Advantage Threat Intelligence vs. Palo Alto Networks AutoFocus

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    Mandiant Advantage Threat Intelligence

    Score8.8 out of 10
    Enterprise companies (1,001+ employees)
    Since 2004, Mandiant has been a partner to security-conscious organizations. Mandiant’s approach helps organizations develop more effective and efficient cyber security programs and instills confidence in their readiness to defend against and respond to cyber threats.N/A

    Palo Alto Networks AutoFocus

    Score8 out of 10
    N/AAutoFocus™ contextual threat intelligence service, from Palo Alto Networks, accelerates analysis, correlation and prevention workflows. Targeted attacks are automatically prioritized with full context, allowing security teams to respond to critical attacks faster, without additional IT security resources.N/A
    Pricing
    Mandiant Advantage Threat IntelligencePalo Alto Networks AutoFocus
    Editions & Modules
    No answers on this topic
    No answers on this topic
    Offerings
    Pricing Offerings
    Mandiant Advantage Threat IntelligencePalo Alto Networks AutoFocus
    Free Trial
    YesNo
    Free/Freemium Version
    YesNo
    Premium Consulting/Integration Services
    YesNo
    Entry-level Setup FeeOptionalNo setup fee
    Additional DetailsPriced by company size—
    More Pricing Information
    Community Pulse
    Mandiant Advantage Threat IntelligencePalo Alto Networks AutoFocus
    Considered Both Products
    Mandiant
    No answer on this topic
    Palo Alto Networks
    No answer on this topic
    Key User Insights
    Would buy again
    100%
    Would buy again
    17 Answers
    No answers on this topic
    Delivers good value for the price
    100%
    Delivers good value for the price
    14 Answers
    No answers on this topic
    Happy with the feature set
    100%
    Happy with the feature set
    17 Answers
    No answers on this topic
    Lived up to sales and marketing promises
    80%
    Lived up to sales and marketing promises
    8 Answers
    No answers on this topic
    Implementation went as expected
    100%
    Implementation went as expected
    14 Answers
    No answers on this topic
    Features
    Mandiant Advantage Threat IntelligencePalo Alto Networks AutoFocus
    Endpoint Security
    Comparison of Endpoint Security features of Mandiant Advantage Threat Intelligence and Palo Alto Networks AutoFocus
    Feature
    Mandiant Advantage Threat Intelligence
    7.2
    6 Ratings
    0% below category average
    Palo Alto Networks AutoFocus
    -
    Ratings
    Infection Remediation7.26 Ratings00 Ratings
    Threat Intelligence
    Comparison of Threat Intelligence features of Mandiant Advantage Threat Intelligence and Palo Alto Networks AutoFocus
    Feature
    Mandiant Advantage Threat Intelligence
    7.8
    10 Ratings
    5% above category average
    Palo Alto Networks AutoFocus
    -
    Ratings
    Network Analytics7.79 Ratings00 Ratings
    Threat Recognition7.89 Ratings00 Ratings
    Vulnerability Classification7.510 Ratings00 Ratings
    Automated Alerts and Reporting8.09 Ratings00 Ratings
    Threat Analysis7.510 Ratings00 Ratings
    Threat Intelligence Reporting8.210 Ratings00 Ratings
    Automated Threat Identification7.99 Ratings00 Ratings
    User Ratings
    Mandiant Advantage Threat IntelligencePalo Alto Networks AutoFocus
    Likelihood to Recommend
    7.8
    (18 ratings)
    8.0
    (4 ratings)
    Usability
    7.6
    (18 ratings)
    -
    (0 ratings)
    User Testimonials
    Mandiant Advantage Threat IntelligencePalo Alto Networks AutoFocus
    Likelihood to Recommend
    Mandiant
    Usually SOC leverages Intel from mutiple sources. The scenarios are: 1.Suitable: In large scale SOC where more than 5000 devices are being monitored and the tech stack is wide, Mandiant will play an excellent role in that scenario. 2.Not Suitable: In small scale SOCs wherein limited devices belonging to the same tech stack is being used then the analysts can rely on OSINT and it is not useful to buy the solution.
    Incentivized
    Read full review
    Palo Alto Networks
    Analytics, Threat Hunting and detailed investigations for the security incidents are the main use cases. Automation on the cloud based on the feeds through the minemeld is another use case. When you deploy PAN on perimeter, Autofocus gives you a temendaous value. If you have non PAN firewall/products running Auto focus doe not make sense.
    Incentivized
    Read full review
    Pros
    Mandiant
    • accelerated threat response feature, prioritizing threats according to requirement.
    • Optimization of the threat intelligence , and can be integrated with 3rd party tools.
    • Features like - Breach ,Adversary, Machine and Operational Intelligence.
    • Mandiant dynamic host and the malware views along with indicators.
    Incentivized
    Read full review
    Palo Alto Networks
    • Threat intelligence
    • Emerging Threats
    • Intelligence feeds
    Incentivized
    Read full review
    Cons
    Mandiant
    • Paywalls exist throughout the data set and can halt an investigation without the right model
    • Some data was incomplete or broken up between pay tiers
    • Navigation through the data lacked a definitive trail or breadcrumbs to retrace steps during investigations
    Incentivized
    Read full review
    Palo Alto Networks
    • third party product integration
    • simplicity of the managment console
    • integration to cortex agents directly
    Incentivized
    Read full review
    Usability
    Mandiant
    Mandiant Advantage Threat Intelligence has a very usable platform, with well-differentiated sections for the analyst, as well as the possibility of cross-searching to obtain the desired results. All this is presented with an interface that is easy on the eye and not very messy, which increases productivity and the speed with which work is done.
    Incentivized
    Read full review
    Palo Alto Networks
    No answers on this topic
    Alternatives Considered
    Mandiant
    It gives more ways to analyze threats and options to fixed it. This device gives more visibility on vulnerability detection and its analysis. It provides detailed reports to have more information of all malwares which help us to increase overall security of our current organization
    Incentivized
    Read full review
    Palo Alto Networks
    If you have Palo Alto, autofocus is the selected choice. If you have Checkpoint than the threat cloud. Price of autofocus is much cheaper. Unit42 is the real differentiator. Minemeld is unique to PAN and working perfectly. Search outputs and are detailed and gives lots of data. Integration with SOAR is much easier with autofocus. Indicator list is huge. Tagging works magnificent.
    Incentivized
    Read full review
    Return on Investment
    Mandiant
    • Improved incident response time
    • Specific investigations that have reduced the attack surface
    • Technical reports on threats not controlled by the bank's local team
    Incentivized
    Read full review
    Palo Alto Networks
    • Cheap for us
    • Easy integration
    • Easy management
    Incentivized
    Read full review
    ScreenShots

    Mandiant Advantage Threat Intelligence Screenshots
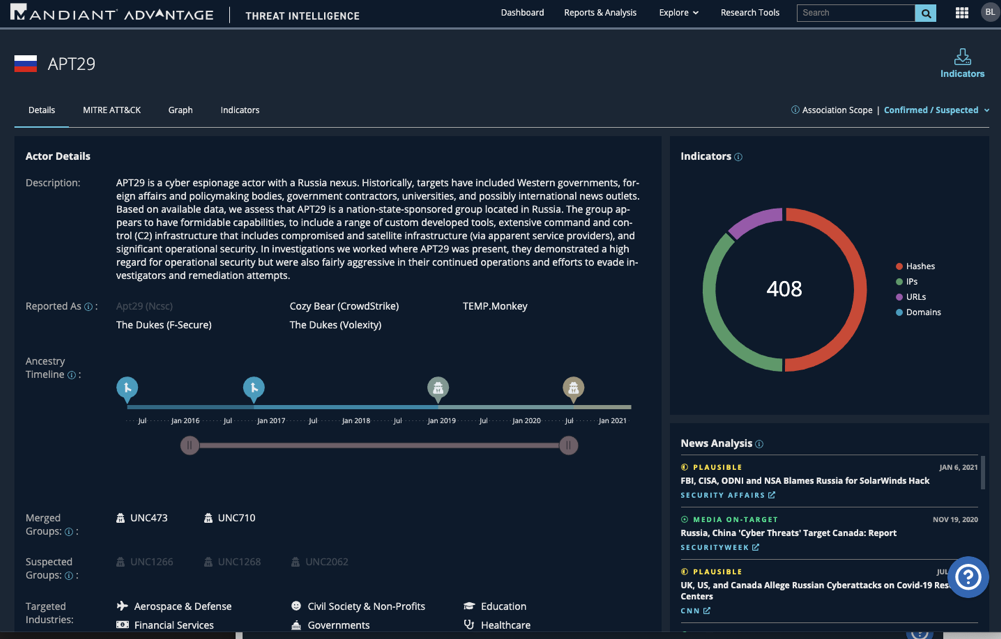
    Screenshot of Mandiant Advantage DashboardScreenshot of Mandiant Advantage Actor DetailsScreenshot of Mandiant Advantage Actor Graph