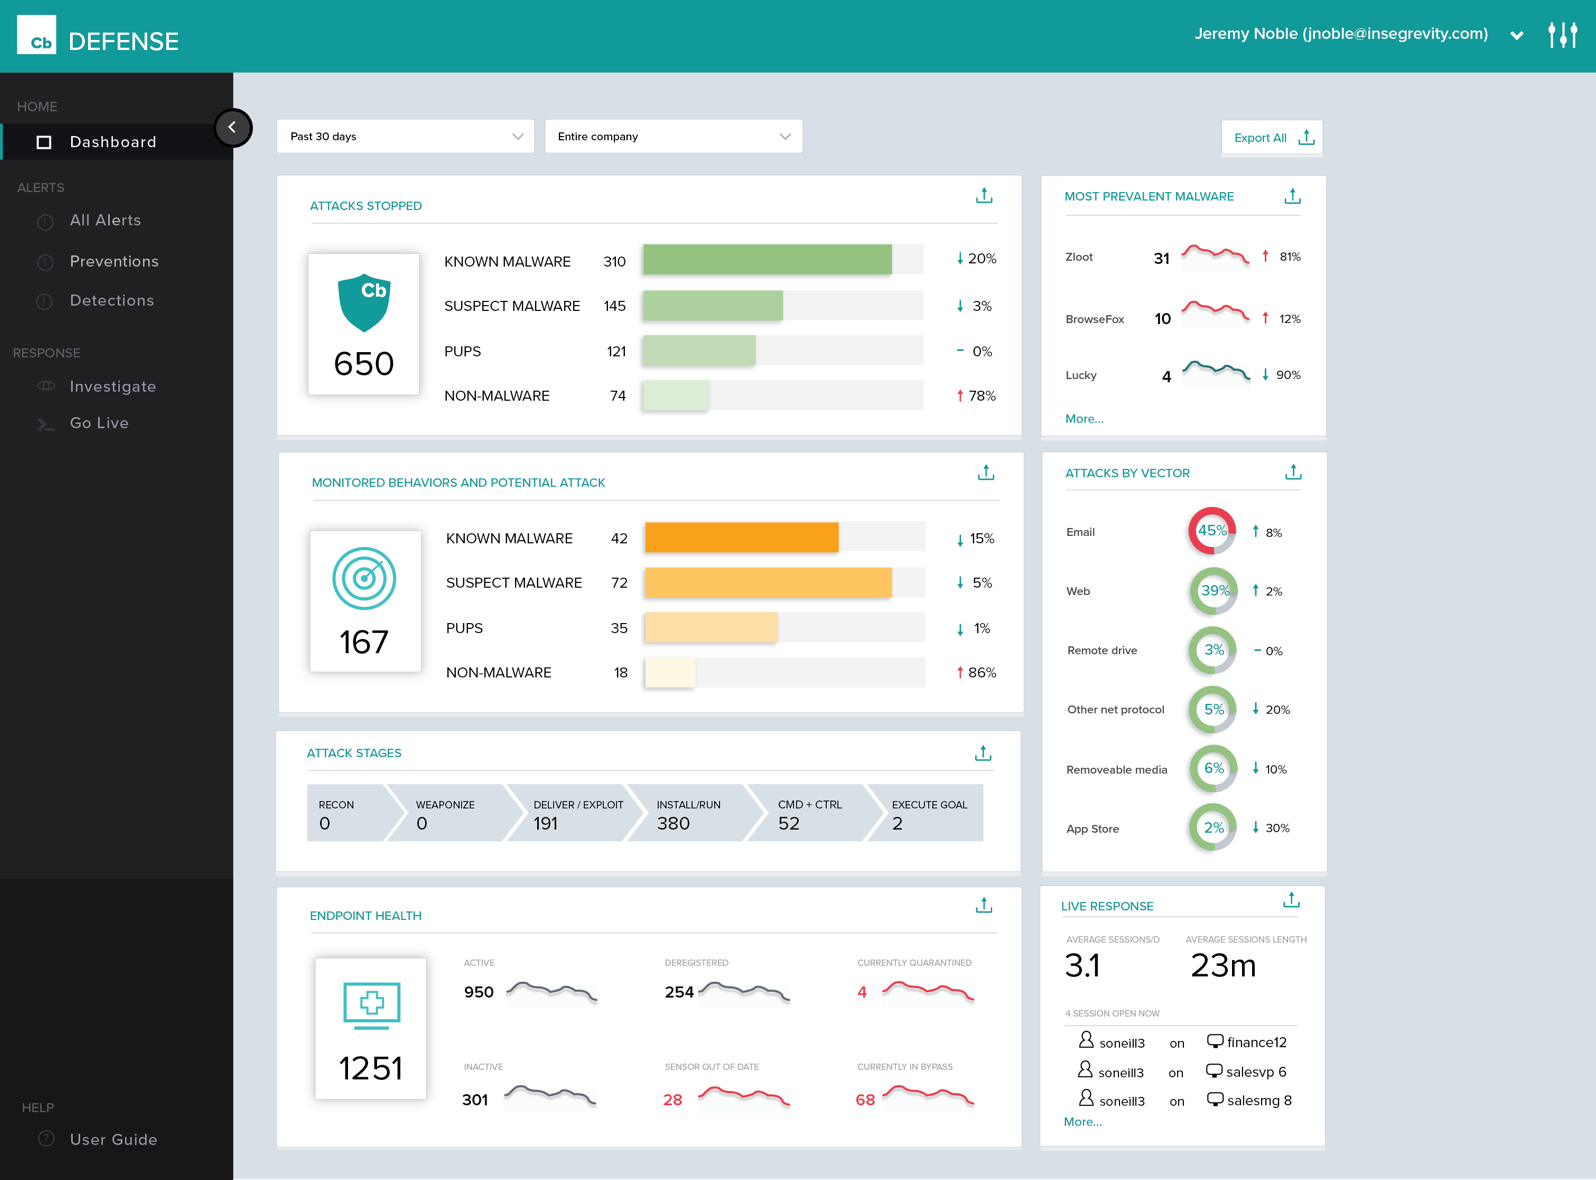
Carbon Black Endpoint is an endpoint security and "next-gen antivirus (NGAV)" that uses machine learning and behavioral models to analyze endpoint data and uncover malicious activity to stop all types of attacks before they reach critical systems.
N/A
IBM Security QRadar EDR
Score7.4 out of 10
N/A
IBM Security QRadar EDR (formerly ReaQta) combines automation and dashboards to minimize analyst workloads, detect anomalous endpoint behavior and remediate threats in near real time. With visibility across endpoints, it combines expected features, like MITRE ATT&CK mapping and attack visualizations, with dual-engine AI and automation. For teams that need extended support, managed detection and response (MDR) services offers 24/7 monitoring and response to help keep users…
Cb Defense has been working very well in our organization. It is giving us much better insight into the applications that people are running on their systems (without authorization). This software is also great because it provides visibility into systems that are remote (off the network but still have Internet access). The out of band feature is great to help ensure that the systems are protected even when a user is traveling.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
IBM Security QRadaar EDR provides all the security features at one place with a reasonable price. Though for smaller organizations, the price may be quite high. Plus since it can detect threats and malwares in real time, every business should try them out.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
History of Process Execution, really anything that happens in the system is easily seen within the Dashboard. I can determine if a bad actor has infected the system, be it malware, backdoor, rootkit, Trojan, then from that point, I can put the system into Quarantine.
Being able to quarantine the system from the Dashboard. With these type of tools, pulling the power and running a hard drive image is not needed. Put the system in quarantine, start the analysis. A year ago, the network engineer might move the system into a VLAN that has no access to anything, except the system performing the remote analysis... Now I do not have to rely on anyone to move a system, power it down, pull the drive, or image the drive. I can just start the analysis right from my workstation.
The Live Response, again goes hand in hand with the quarantine feature.
By now, I am sure you see a process. Its simple, and easy and all done from a cloud-based console, called the dashboard. .. deploy the agent, create the policy, and active live response, set up email alerts, and monitor your endpoints... you are now ready to perform a triage in the event of an infection. We have step 1, step 2, step 3... but, just remember, things do happen, nothing is perfect, but this product has its advantages.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
Policy management can be cumbersome. It is simple to set up a single policy but you have no way to apply the rules to multiple groups. If you need to set up the same rule to multiple policies, you need to type it over again.
Agent updates can be very slow to deploy. We use a mix of rolling out updates via the web console and our management appliance. It can take several weeks to update all agents.
We can be confused on why a rule will apply to a file. Sometimes something is blocked but we don't understand why.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
The console of the product is very easy to use. It provides great detailed information about all aspects of things occurring on the endpoint. It was easy to deploy and set up. The centralized cloud-based interface has made it easy to add two domains and manage them under a single pane with multiple admins. The only reason I wouldn't give it a higher score is a little bit of lag between updated info from the clients and also the lack of accountability in the deployment process. You set the deployment up for multiple machines and can't easily see if it was successful and/or it takes a while to see if it succeeded or failed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
First, I need to disclose that our support is provided by SecureWorks. We purchased CB Defense from them, and they provide 24x7 monitoring and notification services for the solution and its deployment on our endpoints. To date, we are very pleased with this arrangement
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cb is cloud-based and has a more advanced policy management. It also has better forensics information. Cost was similar, but Cb added cost savings in terms of IT management resources. We also have the ability to talk directly with engineers and have input on feature updates.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Bitdefender GravityZone combines multiple security services into a single platform to reduce the cost of building a trusted environment for endpoints. bit the IBM provides a vast support and always there to guide when in need With the majority of our users working in hybrid mode we needed a strong security control that could provide top-class protection with the minimum amount of False Positives (and, of course, of True Positives).
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
NOCs and SOCs heavily use IBM Security QRadar EDR and IBM Security QRadar EDR reduced labor costs to identify endpoint security threats and the treat remediation
IBM Security QRadar EDR offers a consistent approach to endpoint threat identification and resolution, reduces enterprise security operations support costs
In general, IBM Security QRadar EDR enhances enterprise security posture
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. TR verified that a representative sample of customers was invited. More Info