TrustRadius: an HG Insights company

Exabeam Fusion vs. Mandiant Advantage Automated Defense

Save this comparison

Save this comparison

Add Product

Recommended Comparisons

    Overview
    ProductRatingMost Used ByProduct SummaryStarting Price

    Exabeam Fusion

    Score4.1 out of 10
    N/AExabeam headquartered in San Mateo, Exabeam Fusion, a SIEM + XDR. The vendor states the modular Exabeam platform allows analysts to collect unlimited log data, use behavioral analytics to detect attacks, and automate incident response. The Exabeam platform can be deployed on-premise or from the cloud. Exabeam can also integrate information from the Exabeam Threat Intelligence Service, or into a third-party SIEM.N/A

    Mandiant Advantage Automated Defense

    Score8.2 out of 10
    Enterprise companies (1,001+ employees)
    Since 2004, Mandiant has been a partner to security-conscious organizations. Mandiant’s approach helps organizations develop more effective and efficient cyber security programs and instills confidence in their readiness to defend against and respond to cyber threats.

    $0

    By endpoint

    Pricing
    Exabeam FusionMandiant Advantage Automated Defense
    Editions & Modules
    No answers on this topic
    Standard
    $0
    By endpoint
    Premium
    $0
    By endpoint
    Enterprise
    $0
    By endpoint
    Offerings
    Pricing Offerings
    Exabeam FusionMandiant Advantage Automated Defense
    Free Trial
    NoYes
    Free/Freemium Version
    NoNo
    Premium Consulting/Integration Services
    NoNo
    Entry-level Setup FeeNo setup feeOptional
    Additional Details
    More Pricing Information
    Best Alternatives
    Exabeam FusionMandiant Advantage Automated Defense
    Small Businesses
    No answers on this topic
    No answers on this topic
    Medium-sized Companies
    No answers on this topic
    Palo Alto Networks WildFire
    Score9.8 out of 10
    Enterprises
    No answers on this topic
    Trellix Intelligent Sandbox
    Score7.1 out of 10
    All AlternativesView all alternativesView all alternatives
    User Ratings
    Exabeam FusionMandiant Advantage Automated Defense
    Likelihood to Recommend
    8.5
    (2 ratings)
    8.2
    (1 ratings)
    Usability
    9.0
    (2 ratings)
    8.2
    (1 ratings)
    Support Rating
    9.0
    (2 ratings)
    -
    (0 ratings)
    Implementation Rating
    -
    (0 ratings)
    7.3
    (1 ratings)
    User Testimonials
    Exabeam FusionMandiant Advantage Automated Defense
    Likelihood to Recommend
    Exabeam
    As a SIEM tool for investigations, Exabeam is the best in class. The AI assigns numeric values to observed logs them presents high scores to the analyst in a simple dashboard. We can see what is a real threat and ignore so many false positives. Exabeam is the best SIEM was used from an alert fatigue perspective. The simple interface allows other teams not just InfoSec to utilize the tool; helpdesk for asset diagnoses, HR for staffing questions, etc.
    Incentivized
    Read full review
    Mandiant
    I am having a very good experience with the Mandiant Advantage Automated Defense product where I can monitor the network with great ease and be regularly updated throughout the day without using some heavy tools and running queries. It is indeed a very good and easy-to-use tool that helps us monitor with great ease.
    Incentivized
    Read full review
    Pros
    Exabeam
    • Fast search times, unlike other competing solutions.
    • The ability for engineers to obtain access to the command line interface for troubleshooting, at least for on-premise deployments.
    • License is suitable for organisations with lots of logs to ingest.
    • Hardware required for on premise deployments is well supported.
    Incentivized
    Read full review
    Mandiant
    No answers on this topic
    Cons
    Exabeam
    • More and better drop-down menus, some items in threat hunter require you know subsets.
    • Less dashboards, combine AA and DL without having separate logins.
    • More complete playbooks are already built out. You have the structure set up for templates like malware and phishing, go further and completely build them out from start to finish, most companies would just use them and not personalize their configurations.
    • Quarterly health checkup diagnostics of systems sent out to users.
    Incentivized
    Read full review
    Mandiant
    • A more detailed view about the incidents and what they were highlighted
    • A false positive might take up to a week to get corrected at the backend and not be shown as an incident
    • Switching between clients and their dashboards can be made more efficient
    Incentivized
    Read full review
    Usability
    Exabeam
    Exabeam is very good at processing lots of logs without excessive licensing costs. It has a professional support team that's very quick to resolve any issues and provides custom parsers quickly and enables our analysts to search vast data sets without having to wait long for results to be returned. The product is getting more mature with new features every major release.
    Incentivized
    Read full review
    Mandiant
    Because I use it on a daily basis and it is a friendly tool.
    Incentivized
    Read full review
    Support Rating
    Exabeam
    Exabeam Fusion has so many diffferent out reach meetings, webinars, community virtual coffees, and events that you can always stay abreast of what if happening and get new ideas for use cases. Their support actually answers their phones and can respond in chat instantly. With our cloud deployment Exabeam support teams can instantly see our systems and help us.
    Incentivized
    Read full review
    Mandiant
    No answers on this topic
    Implementation Rating
    Exabeam
    No answers on this topic
    Mandiant
    I was quite satisfied with the implementation.
    Incentivized
    Read full review
    Return on Investment
    Exabeam
    • Reduced time to triage alerts.
    • Reduced number of alerts which need escalation to senior tiers.
    • The ability for analysts to quickly run playbooks for additional information and enrichment.
    • Ability to retain data for longer periods for forensics purposes.
    • Improved search performance compared with other SIEM solutions.
    Incentivized
    Read full review
    Mandiant
    • Reduced security engineering costs
    • Reduced IT/SOC overhead costs
    • Less time wasted pursuing false positives
    Incentivized
    Read full review
    ScreenShots

    Mandiant Advantage Automated Defense Screenshots
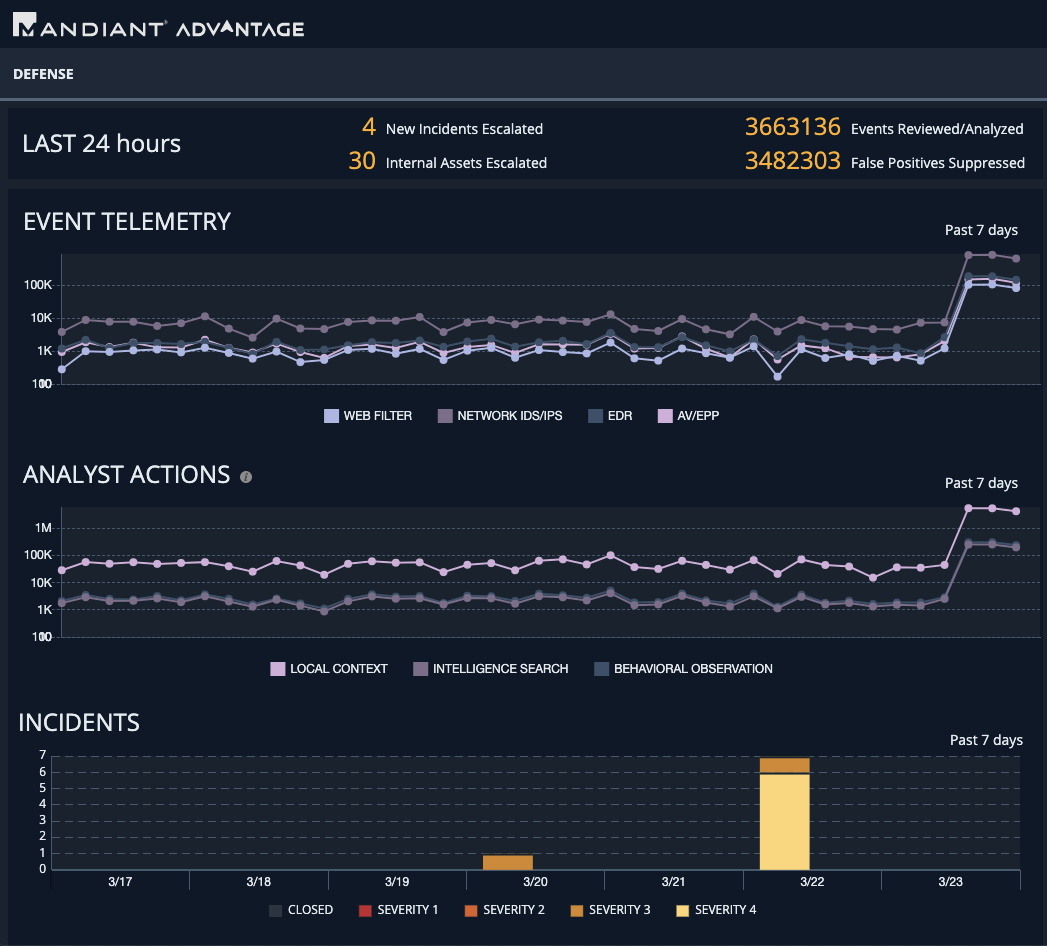
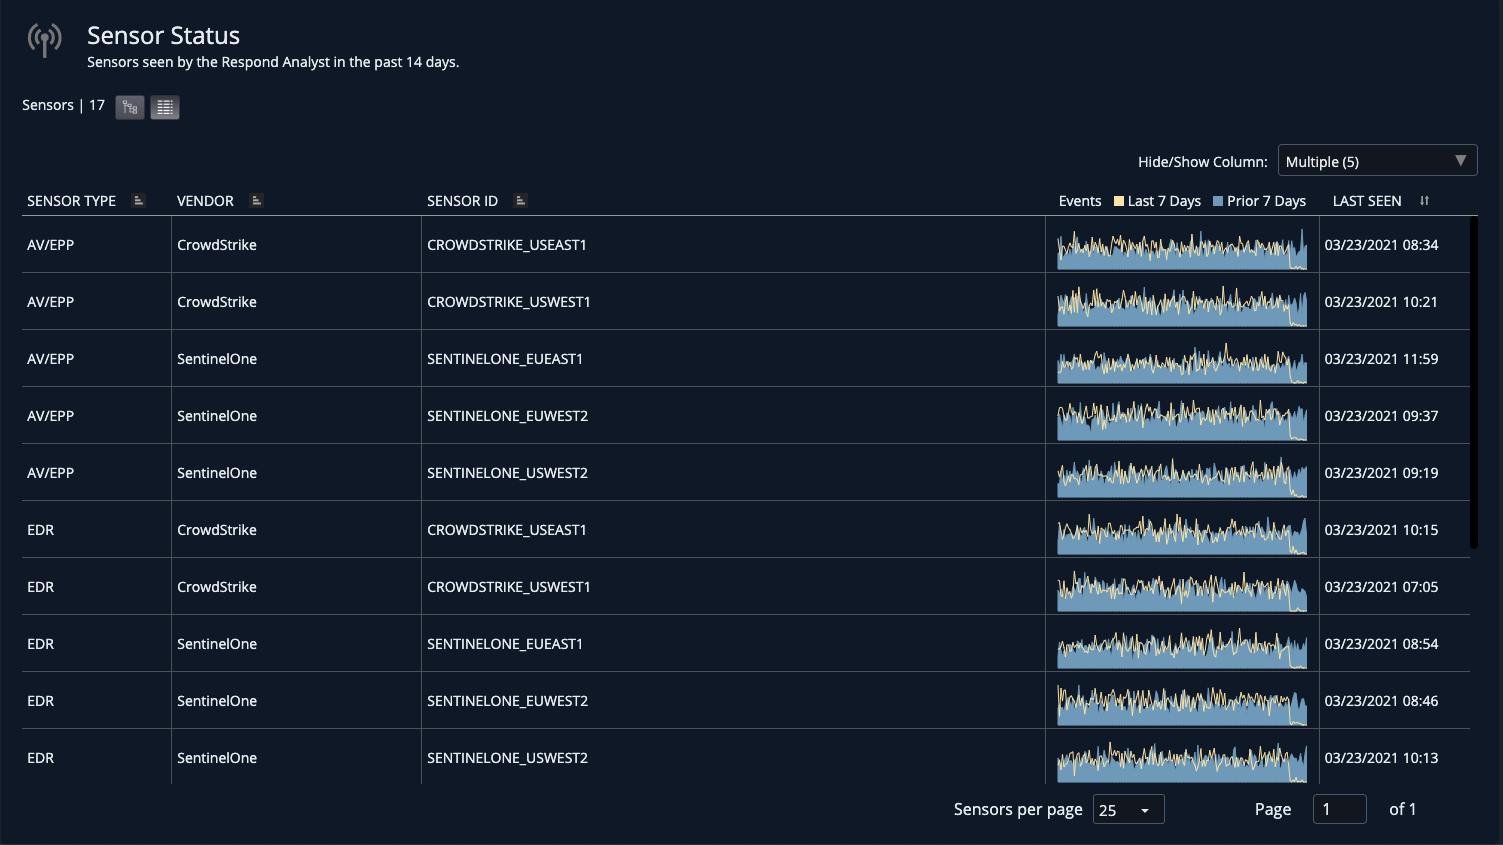
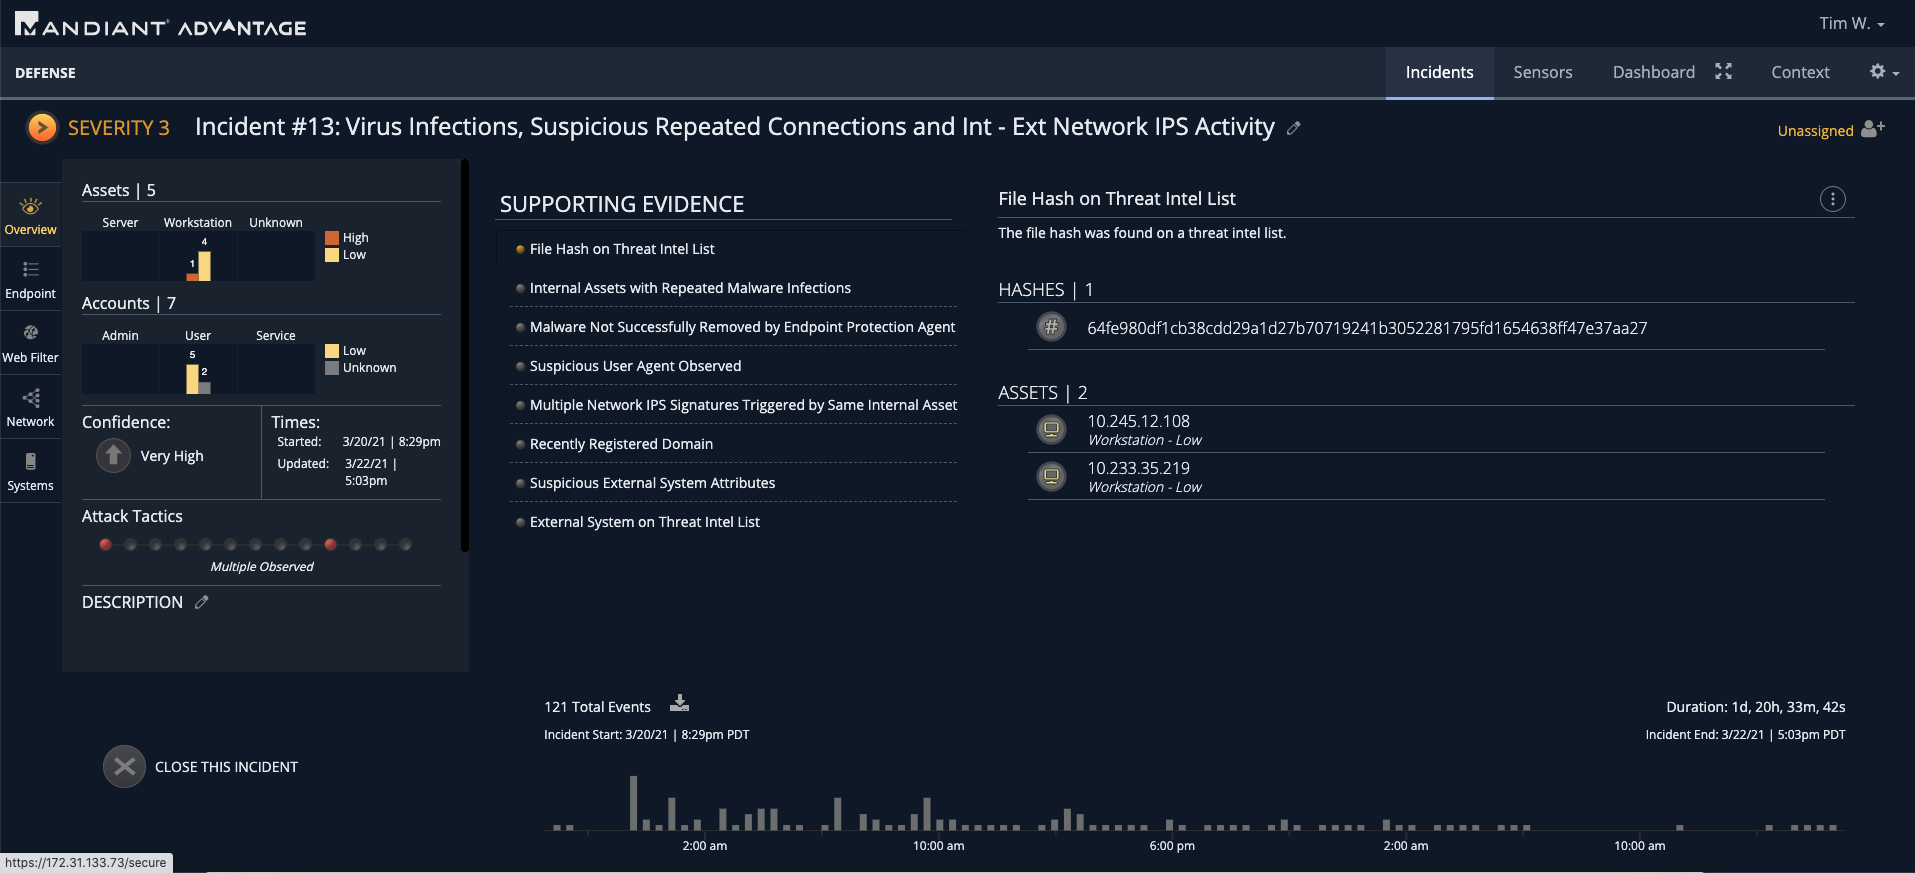
    Screenshot of Dashboard screenshotScreenshot of Sensor Status screenshotScreenshot of Incident response dashboard