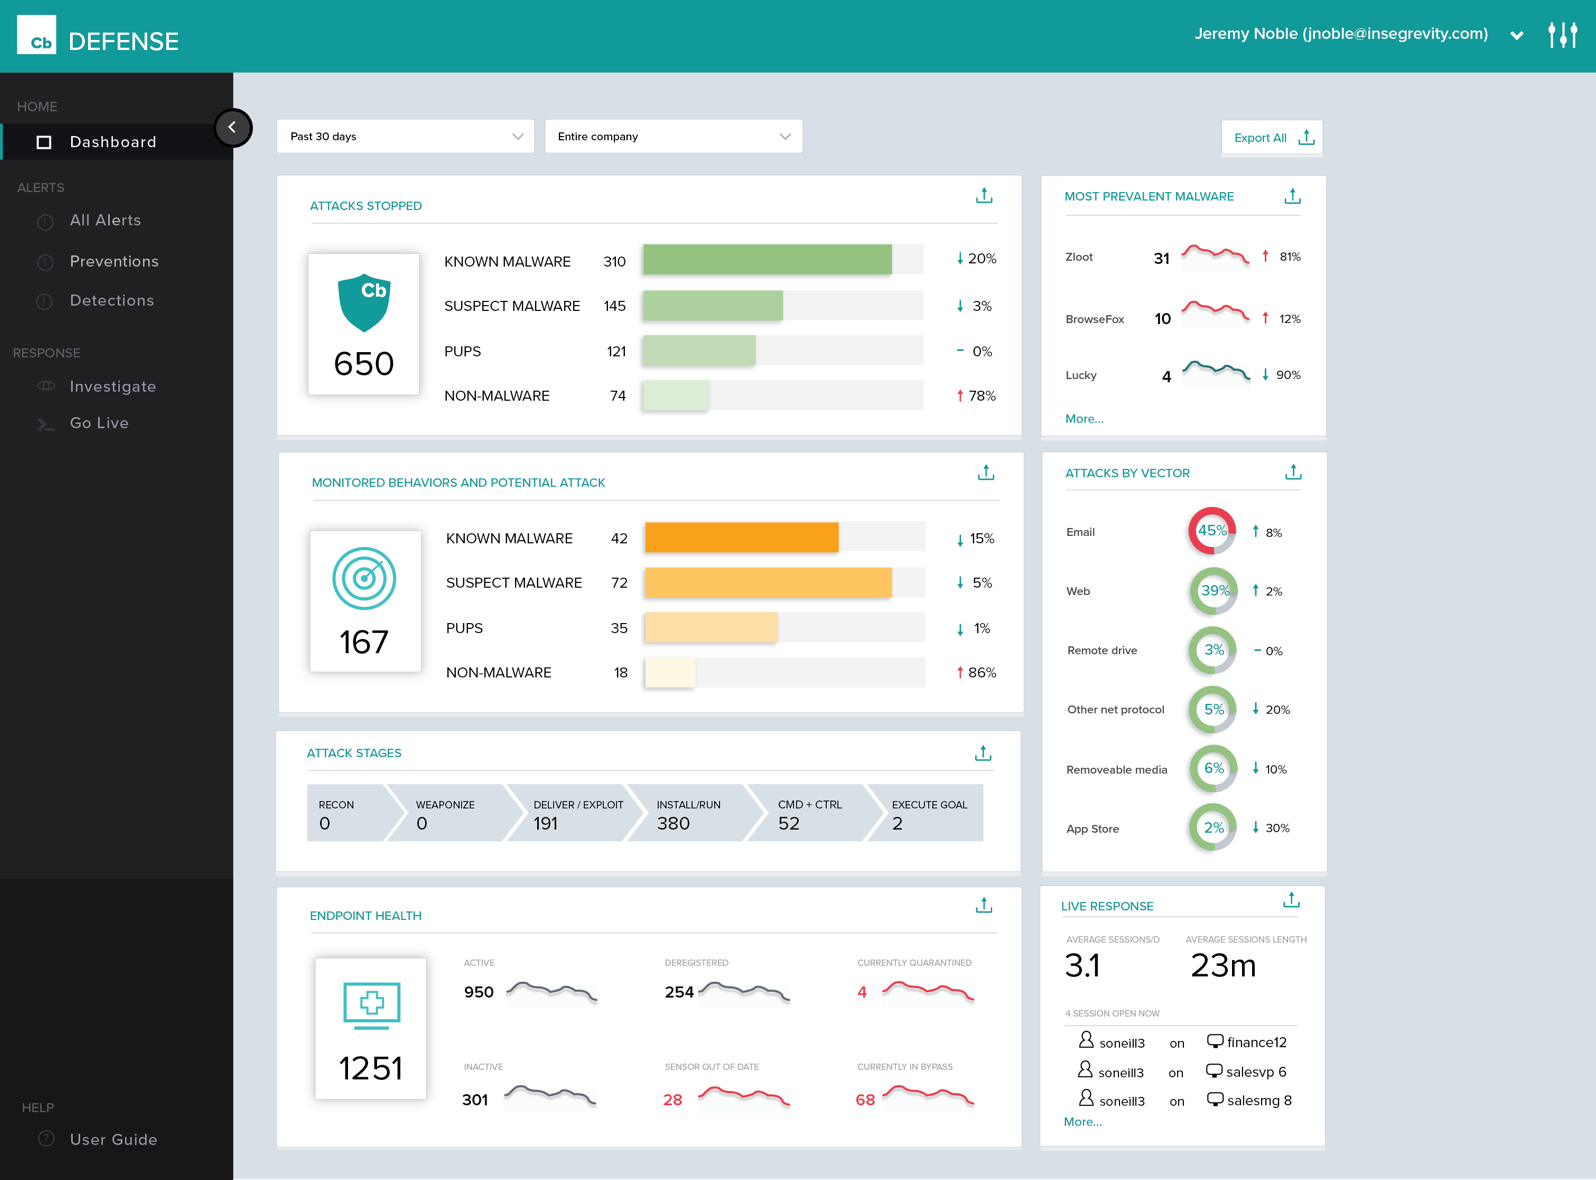
Carbon Black Endpoint is an endpoint security and "next-gen antivirus (NGAV)" that uses machine learning and behavioral models to analyze endpoint data and uncover malicious activity to stop all types of attacks before they reach critical systems.
N/A
Palo Alto Networks Cortex XDR
Score8.4 out of 10
N/A
Cortex XDR (formerly Traps) replaces traditional antivirus with multi-method prevention, a proprietary combination of malware and exploit prevention methods that protect users and endpoints from known and unknown threats.
N/A
Pricing
Carbon Black Endpoint
Palo Alto Networks Cortex XDR
Editions & Modules
No answers on this topic
No answers on this topic
Offerings
Pricing Offerings
Carbon Black Endpoint
Palo Alto Networks Cortex XDR
Free Trial
No
No
Free/Freemium Version
No
No
Premium Consulting/Integration Services
No
No
Entry-level Setup Fee
No setup fee
No setup fee
Additional Details
—
—
More Pricing Information
Community Pulse
Carbon Black Endpoint
Palo Alto Networks Cortex XDR
Considered Both Products
Broadcom
Verified User
Chose Carbon Black Endpoint
We evaluated 3 other competitors and determined that Cb Defense was the best "bang for the buck" when it comes to Next-Generation Anti Virus. Their support (and sales) teams have been very helpful and offered a tremendous level of transparency. Our sales representative went …
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cb Defense has been working very well in our organization. It is giving us much better insight into the applications that people are running on their systems (without authorization). This software is also great because it provides visibility into systems that are remote (off the network but still have Internet access). The out of band feature is great to help ensure that the systems are protected even when a user is traveling.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Malware that doesn’t leave files behind has become widely available. Anyone who can afford to reverse this trend should purchase technology. Application whitelisting isn’t for everyone, and Palo Alto Networks Traps can help. Enterprises looking for a low-affected, next-generation solution with high protection should consider it. PAN Traps is a great product at a reasonable price, and I highly recommend it.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
History of Process Execution, really anything that happens in the system is easily seen within the Dashboard. I can determine if a bad actor has infected the system, be it malware, backdoor, rootkit, Trojan, then from that point, I can put the system into Quarantine.
Being able to quarantine the system from the Dashboard. With these type of tools, pulling the power and running a hard drive image is not needed. Put the system in quarantine, start the analysis. A year ago, the network engineer might move the system into a VLAN that has no access to anything, except the system performing the remote analysis... Now I do not have to rely on anyone to move a system, power it down, pull the drive, or image the drive. I can just start the analysis right from my workstation.
The Live Response, again goes hand in hand with the quarantine feature.
By now, I am sure you see a process. Its simple, and easy and all done from a cloud-based console, called the dashboard. .. deploy the agent, create the policy, and active live response, set up email alerts, and monitor your endpoints... you are now ready to perform a triage in the event of an infection. We have step 1, step 2, step 3... but, just remember, things do happen, nothing is perfect, but this product has its advantages.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Policy management can be cumbersome. It is simple to set up a single policy but you have no way to apply the rules to multiple groups. If you need to set up the same rule to multiple policies, you need to type it over again.
Agent updates can be very slow to deploy. We use a mix of rolling out updates via the web console and our management appliance. It can take several weeks to update all agents.
We can be confused on why a rule will apply to a file. Sometimes something is blocked but we don't understand why.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The console of the product is very easy to use. It provides great detailed information about all aspects of things occurring on the endpoint. It was easy to deploy and set up. The centralized cloud-based interface has made it easy to add two domains and manage them under a single pane with multiple admins. The only reason I wouldn't give it a higher score is a little bit of lag between updated info from the clients and also the lack of accountability in the deployment process. You set the deployment up for multiple machines and can't easily see if it was successful and/or it takes a while to see if it succeeded or failed.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cortex XDR does a very good job of blocking suspicious and threatening items. However, as with all software of this nature, it will sometimes block known-good items. The difficulty is in manually whitelisting these known-good items. The interface to whitelist is confusing even for a seasoned IT professional and has been the single most frustrating experience of using Cortex XDR
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
First, I need to disclose that our support is provided by SecureWorks. We purchased CB Defense from them, and they provide 24x7 monitoring and notification services for the solution and its deployment on our endpoints. To date, we are very pleased with this arrangement
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The support we receive from Palo Alto is one of the best aspects of Traps. It is very easy to recommend their support. It seems much easier to connect directly with someone with a deep understanding of the product rather than other companies where you basically have to make an airtight case that it is some kind of non-standard issue that can't be solved with existing documentation. Palo Alto digs deep and helps with advanced troubleshooting to get things working.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Cb is cloud-based and has a more advanced policy management. It also has better forensics information. Cost was similar, but Cb added cost savings in terms of IT management resources. We also have the ability to talk directly with engineers and have input on feature updates.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
Traps is the slickest interface, easy to use and intuitive rule making, and the rest just didn't quite stack up to the performance level of Traps. McAfee and Kaspersky just hog processor and RAM power. I didn't like the interface and functionality of SentinelOne as much as Traps. Palo Alto really put a lot of time into the development of this software, and had some of the founding fathers of IT Security heading the development process. Can't beat that.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info