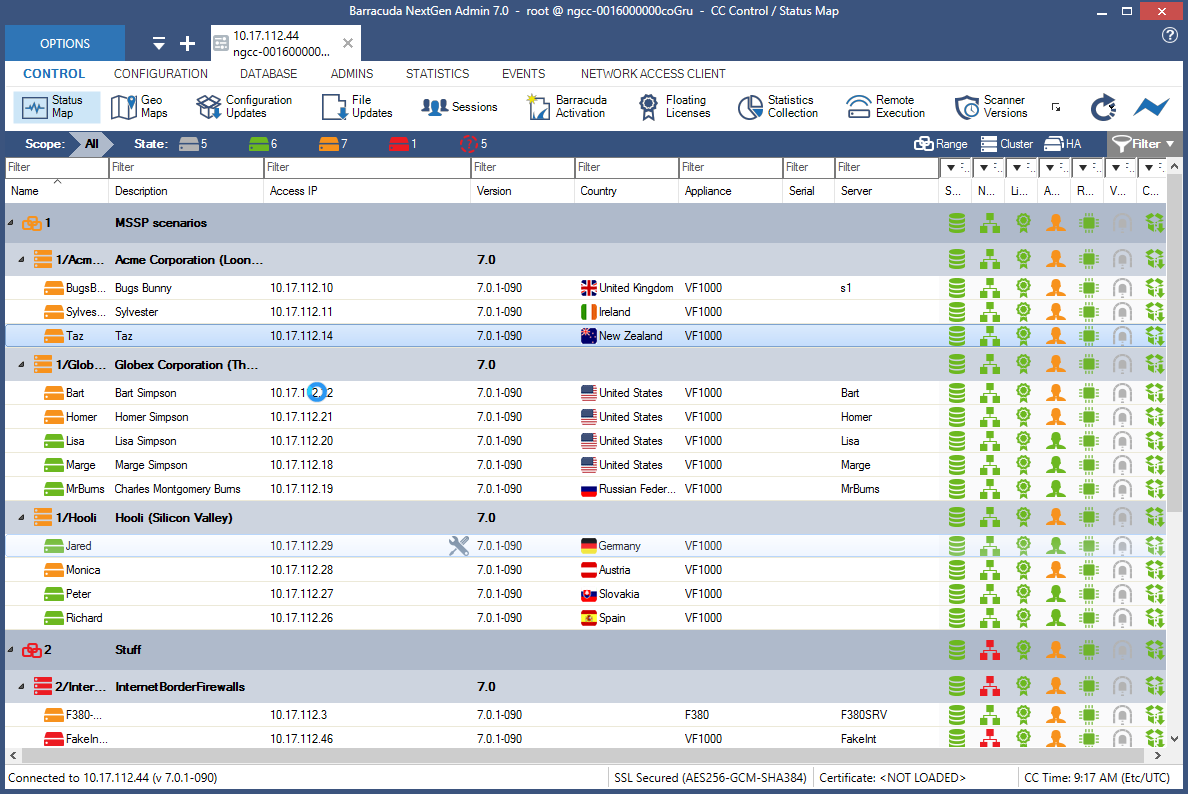
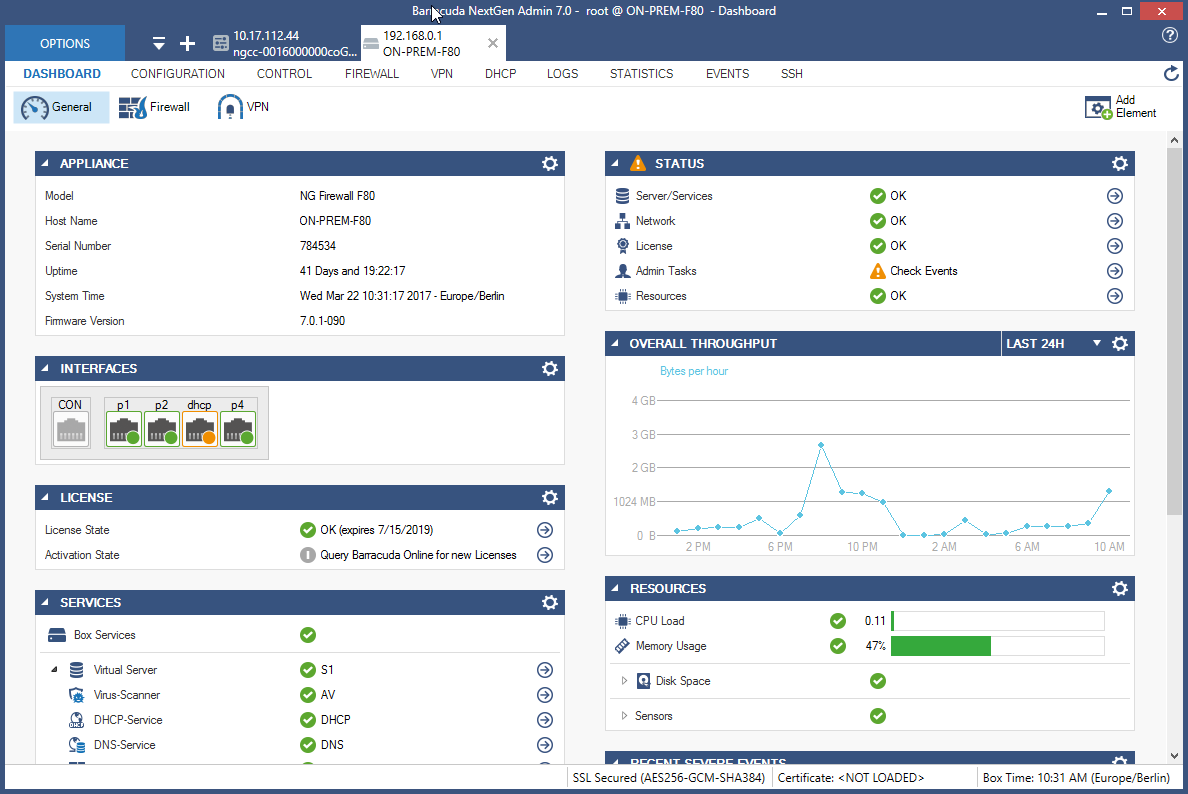
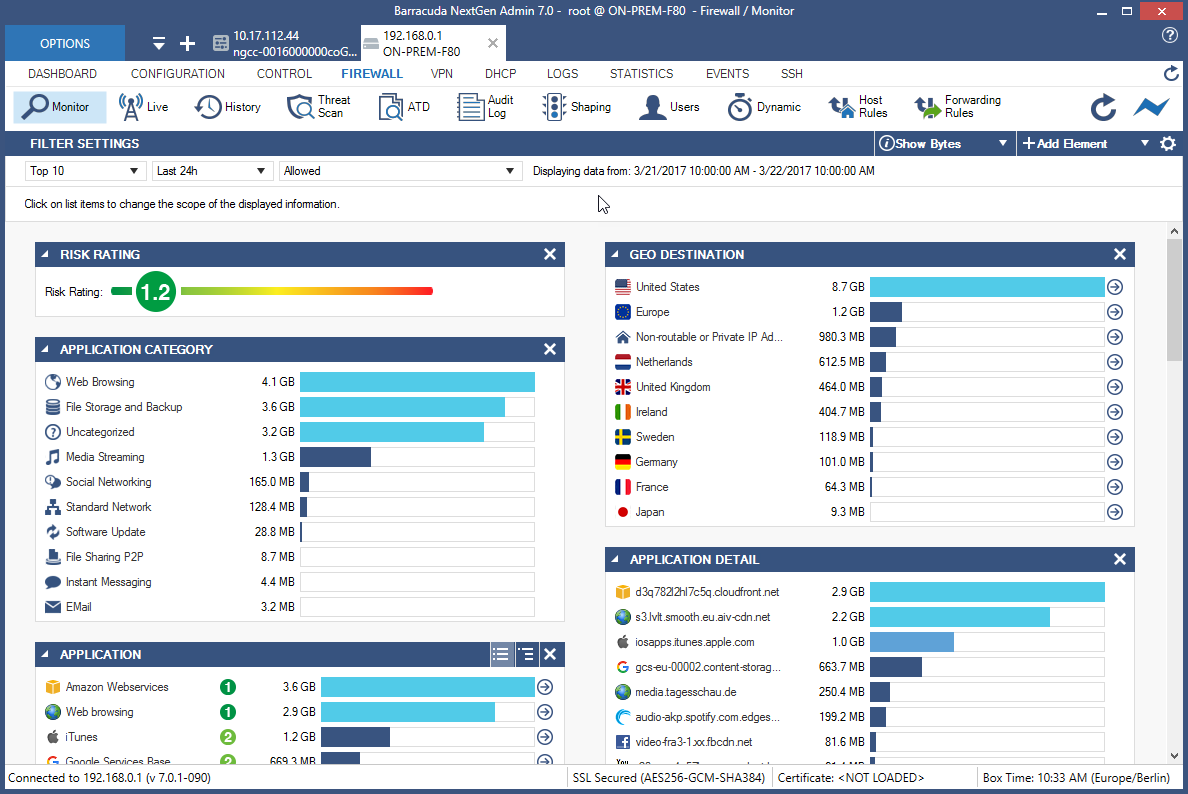
Barracuda Web Application Firewall, from Barracuda Networks in Campbell, California, protects web applications from bots, DDoS attacks, and other advanced threats to enterprise apps.
N/A
pfSense
Score9.9 out of 10
N/A
pfSense is a firewall and load management product available through the open source pfSense Community Edition, as well as a the licensed edition, pfSense Plus (formerly known as pfSense Enterprise). The solution provides combined firewall, VPN, and router functionality, and can be deployed through the cloud (AWS or Azure), or on-premises with a Netgate appliance. It as scalable capacities, with functionality for SMBs. As a firewall, pfSense offers Stateful packet inspection, concurrent…
Easy to use and reliable, with very little maintenance required and zero downtime to date. For the education sector, ease of use is hugely important as IT Managers/Technicians are often "Jack of all trades" with a good, broad general knowledge but perhaps lacking specific expertise in certain aspects. Being provided with easy-to-follow tutorials and instructions has been very useful in setting up and configuring the firewall, especially as my background is more in desktop support.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
I believe PFSense is well suited for both home lab environments as well as up to small to mid-size business environments on a tight budget. However, I would implore that anything in production requires the use of the authorized hardware that PFSense sells to receive support. However, in my experience, PFSense is a solid set-and-forget firewall solution.
Easy to use. Good user interface design! Easy to understand and easy to set up.
Lower hardware requirement. 3 years ago, we used an old PC to run it. Now, we have changed to a router device with Celeron CPU and 8GB RAM. It runs smoothly with a 1000G commercial broadband.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
STM crashes sometimes happen due to unusual traffic pattern
Obfuscation on the client side user credentials which appears in the developer tools of browser
URL Profiles redundancy during the learning of traffic needs to be fixed
Dos Protection should be more granular like escalation period to throw JS challenge, Captcha and rate limit when escalation period hits until the WAF stops the attack
Client Fingerprinting should work as expected when verifying the clients as in rare some scenarios, it creates issues
I did kind of mention a Con in the Pro section with OpenVPN.
When I create a config for an employee other employees are able to login to that config.
I could be doing something wrong when I am making it - I am not afraid to admit that as I am pretty new to all of this, but it seems like it builds a key and I would think the key would be unique in some way to each employee, but I could be wrong.
I actually do not have a lot of Con's for this software - I did not get to set this up on our work network so I am not sure of any downfalls when installing.
I installed this on my personal machine in a Hyper-V environment to get a feel for it before I started working on it at work and it seemed pretty smooth. I didn't run into any issues.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
-User friendly interface for quick learning -Quick deployment for deploying applications -Easy to manage for naive -System components and upgradation of the WAF is very easy go with -Back restoration is very to make it up and ready anytime -Seperate JSON and XmL profiles for each URLs of the application is plus -Amazing and world class support engineer in comparison other vendors and always available to support -Quick resolution on bugs with their patch applying process
The pfSense UI is easy to navigate and pretty go look at. It is much better than some high dollar firewalls that just throw menus you you. The pfSense UI is quick and responsive and makes sense 99% of the time. Changes are committed quickly and the hardware rarely requires a reboot. It just runs.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
The Barracuda Web Application Firewall is easy to use. Support from Barracuda is great also. Load Balancing of the Web Application Firewall is also nice. This allows you to do maintenance or have large loads for the end-user. Threat monitoring of our network and traffic coming into our services within our cloud solution.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
We have been using their Backup products especially Backup Appliances and legacy products like Intronis. We are also using their Cloud Backup Solutions for O365. This is the reason we opted for this product.
Meraki has a unified management login for all devices, which is nice. It also has decent content filtering, both areas where pfSense is weaker. Where pfSense far ouclasses Meraki is in the ease of use and the other width of features. These include features such as better VPN interoperability, non-subscription based pricing, auditability, not relying on the infrastructure of a third party, more transparency of what's actually going on, easier to deploy replacements if hardware fails. Additionally, the NAT management for pfSense seems to be a bit better, as you can NAT between any network segment and not just the LAN segments out the WAN interfaces.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info
pfSense can be installed on commodity hardware with no licensing fees. With a simple less than 10 minute restore time, on most hardware, it's an extremely inexpensive way to achieve the same results that some of the more expensive vendors provide.
The easy to use interface has allowed configuration management to be preformed by lower level technicians with quick and easy training.
A de minimis incentive was given to thank the reviewer for their time. The incentive was not used to bias or drive a particular response, nor was the incentive contingent on a positive endorsement. More Info